Learn
Learn about agentic coding security and Endor Labs
Ebook/Report
Malware in Open Source Ecosystems
April 1, 2026
No items found.
Blog
New research: malware in open source ecosystems surges 14x as attackers hijack trusted packages
April 1, 2026
News
Malware
Security
Blog
Axios compromised: hijacked maintainer account pushes malicious npm versions
March 30, 2026
Security
Malware
Ebook/Report
A Practitioner’s Guide to Responding to the TeamPCP Supply Chain Attacks
March 27, 2026
Malware
Blog
CanisterWorm: Malicious npm Packages Deploy Self-Propagating Supply Chain Worm
March 21, 2026
Security
Malware
Solution Brief
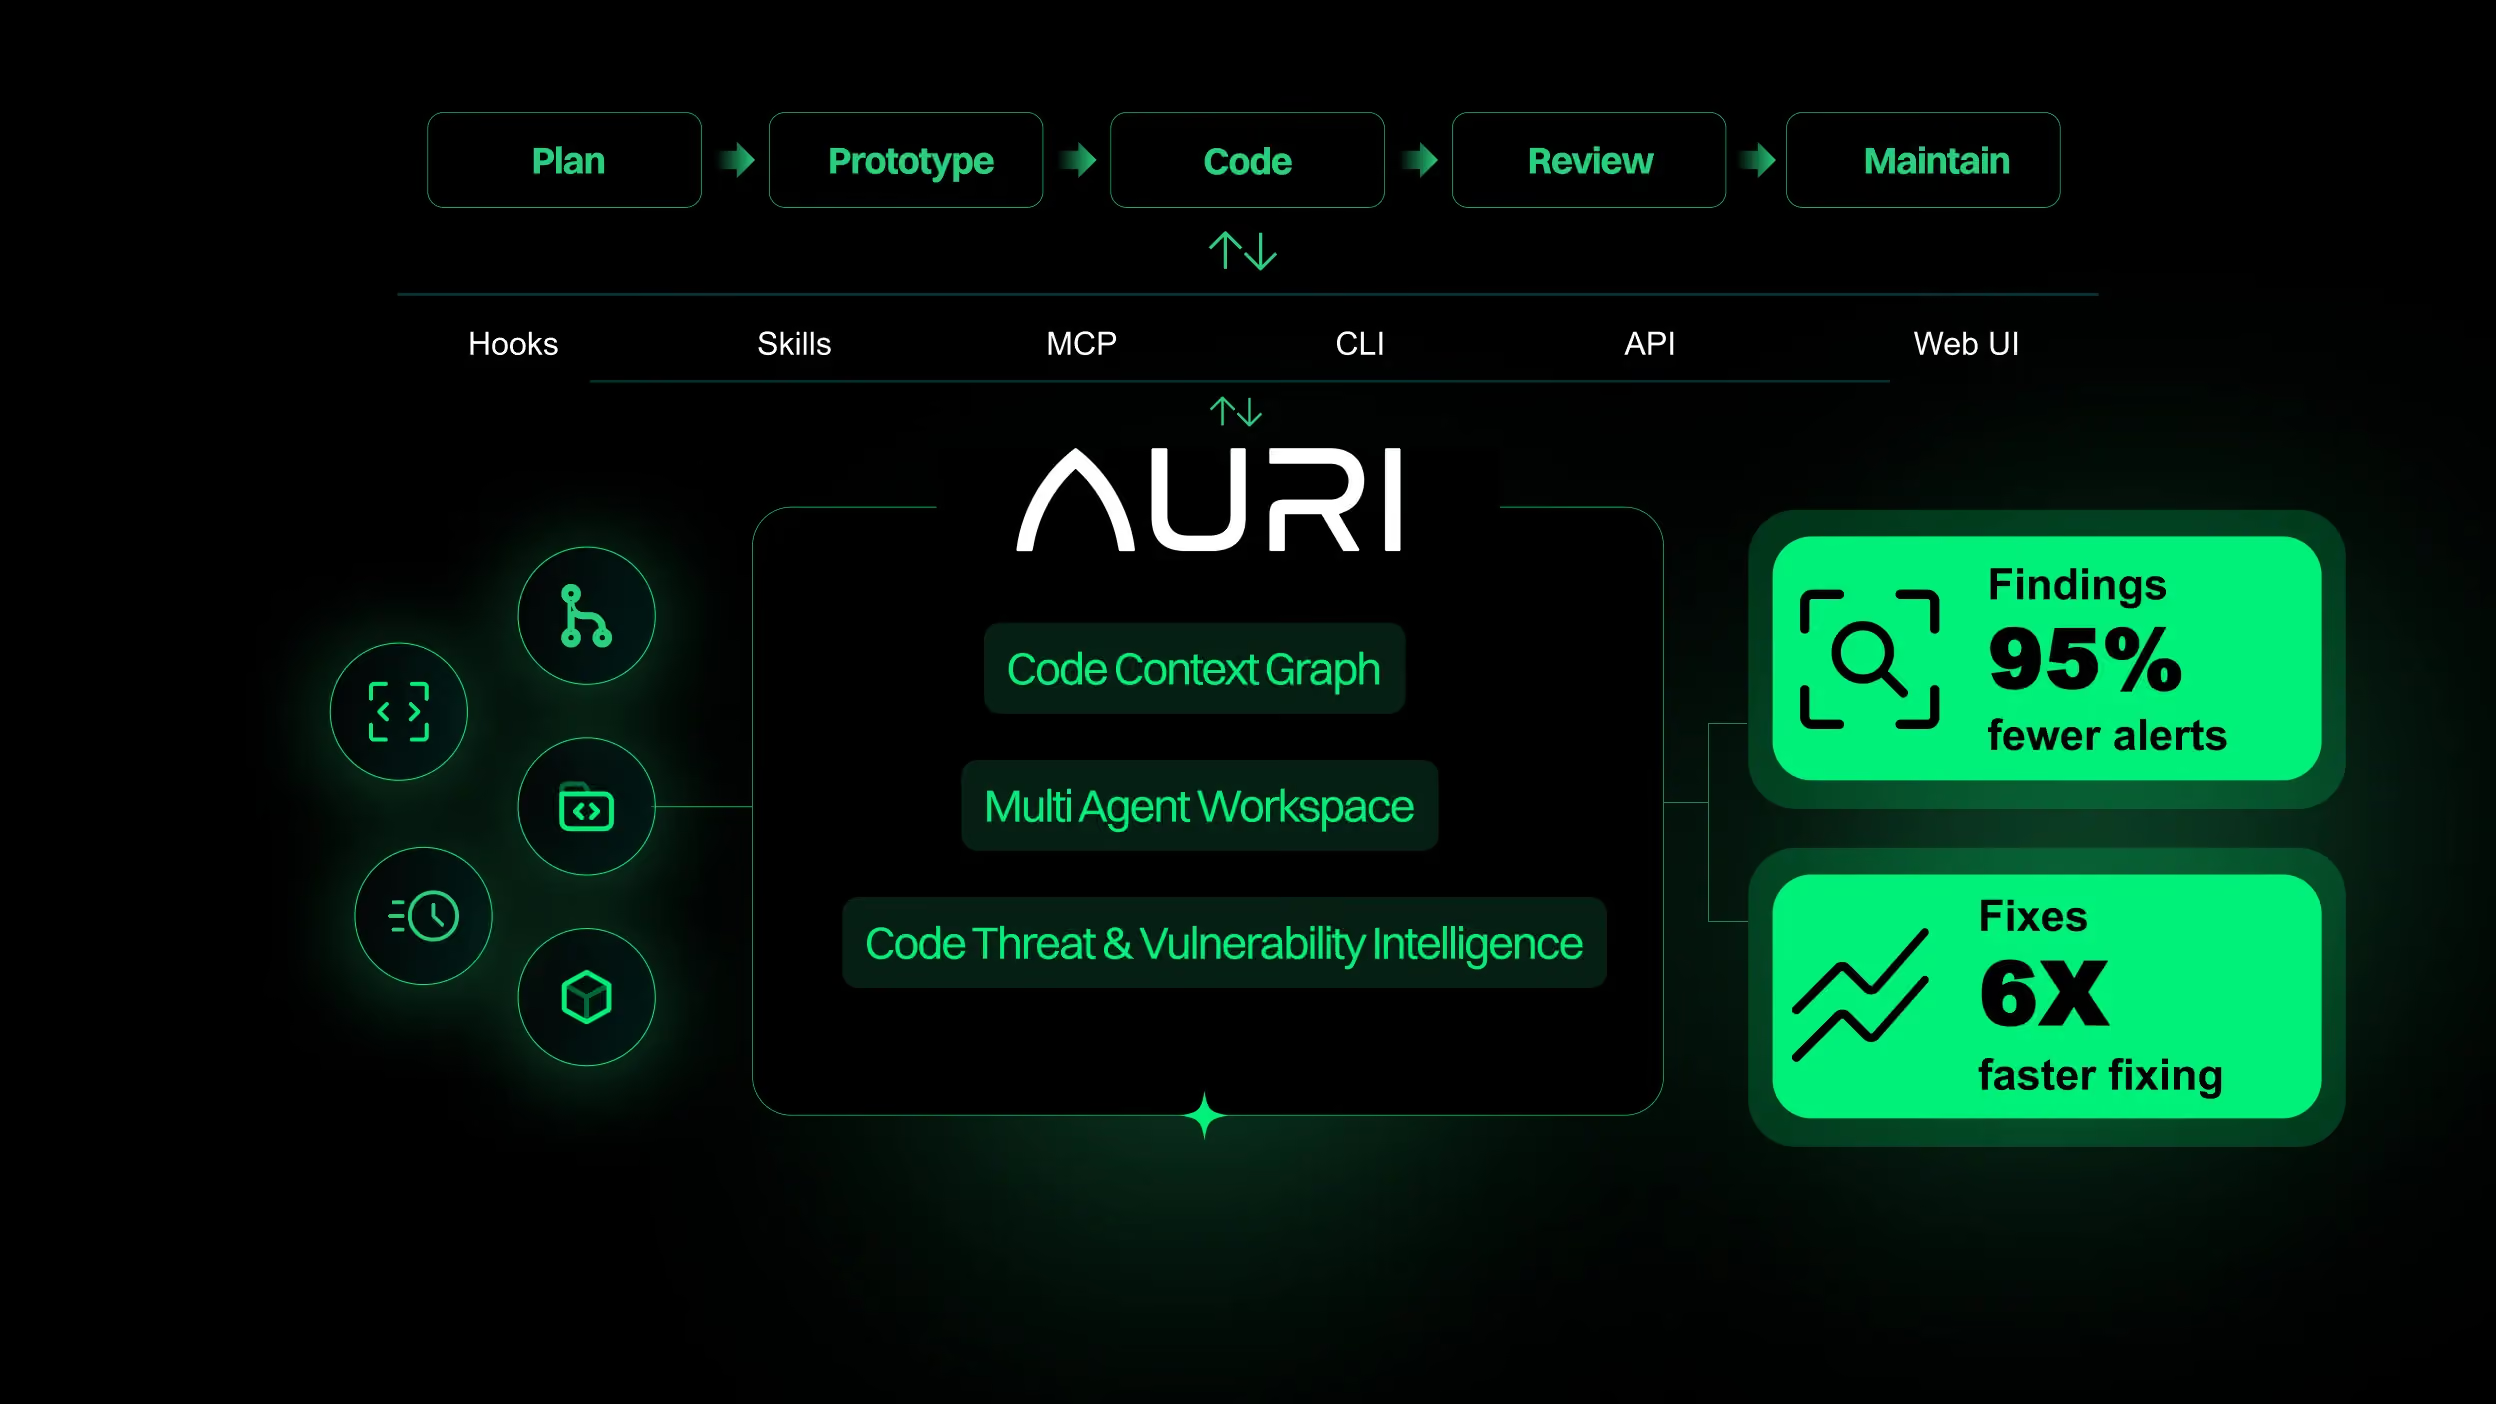
AURI: Security Intelligence for Agentic Software Development
March 19, 2026
AI/ML
Security
Blog
Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution
March 18, 2026
Malware
Blog
npm is serving malware to 134,000 developers, and the maintainer can’t stop it
March 18, 2026
Security
Malware

Blog
How the EU Cyber Resilience Act (CRA) rewrites the rules of software liability
March 13, 2026
Opinion
Compliance & SBOM
Blog
The Return of PhantomRaven: Detecting Three New Waves of npm Supply Chain Attacks
March 10, 2026
Security
Malware
Blog
Intelligence and governance in the software supply chain with Endor Labs and Cloudsmith
March 10, 2026
AI/ML
News
Partner blogs
Blog
Introducing AURI: Security Intelligence for AI Coding Agents and Developers
March 3, 2026
AI/ML
News
Blog
Remote Code Execution (RCE) in Ghost CMS (CVE-2026-29053): A Transitive Dependency Wreaks Havoc
March 2, 2026
Security
News
Open Source

Ebook/Report
EU Cyber Resilience Act
February 27, 2026
Compliance & SBOM
Blog
CVE-2026-27959: Userinfo Host Header Injection in Koa
February 25, 2026
Security
Open Source
Blog
AI SAST Finding: Path Traversal in OpenClaw via LLM Guardrail Bypass
February 19, 2026
Security
Open Source
Blog
Supply Chain Attack targeting Cline installs OpenClaw
February 18, 2026
Malware
Security
Open Source
Blog
How AI SAST Traced Data Flows to Uncover Six OpenClaw Vulnerabilities
February 18, 2026
Security
Open Source
Blog
The Missing Layer: Why Container OS Libraries Need Reachability Analysis
February 13, 2026
Security
Blog
Introducing Full Stack Reachability: Container Scanning That Actually Reduces Noise
February 11, 2026
No items found.
Blog
CVE-2026-25049 Expression Escape Vulnerability Leading to RCE in n8n
February 4, 2026
Security
News
Open Source
Blog
7 Snyk Alternatives for Engineering Teams in 2026
February 2, 2026
Developer Productivity
DevSecOps Tools
Blog
npm Account Takeovers are a Growing Malware Trend
January 29, 2026
Malware
Open Source
Security
Blog
CVE-2026-22709: Critical Sandbox Escape in vm2 Enables Arbitrary Code Execution
January 27, 2026
Open Source
Security
SCA
Blog
Classic Vulnerabilities Meet AI Infrastructure: Why MCP Needs AppSec
January 23, 2026
Open Source
Security
Blog
How Fake Font Packages Abused npm as a CDN
January 23, 2026
Security
Open Source
Blog
Your Next Breach Won’t Be a CVE: Connecting Real Incidents to AI-Aware Code Review
January 21, 2026
AI/ML
First Party Code
Customer Story
Astronomer Modernizes AppSec with Endor Labs
January 20, 2026
Customer Stories
SCA
Tech
Compliance & SBOM
Blog
Eight for One: Multiple Vulnerabilities Fixed in the Node.js Runtime
January 13, 2026
Open Source
Security
Blog
n8mare on auth street: supply chain attack targets n8n ecosystem
January 9, 2026
Security
Malware
Open Source
Blog
CVE-2025-12543: Host Header Validation Bypass in Undertow
January 9, 2026
Open Source
Security
Blog
CVE-2025-68428: Critical Path Traversal in jsPDF
January 6, 2026
Security
Open Source
Blog
Bringing Malware Detection Into AI Coding Workflows with Cursor Hooks
December 17, 2025
AI/ML
Malware
Open Source
Security
Blog
When Regex Isn’t Enough: How We Discovered CVE-2025-13780 in pgAdmin
December 12, 2025
Open Source
Security
Blog
When a Broken Fix Leads to RCE: How We Found CVE-2025-66626 in Argo
December 12, 2025
Security
Open Source
Blog
From Vision to Reality: How Endor Labs Delivers Developer-First Security
December 9, 2025
Developer Productivity
Blog
Developer Experience: The Key to Successful Security
December 9, 2025
Developer Productivity
Blog
Critical Remote Code Execution (RCE) Vulnerabilities in React and Next.js
December 3, 2025
Security
Open Source
Customer Story
Rubrik Hits Aggressive SLAs via Endor Labs
December 2, 2025
Customer Stories
SCA
Tech
Compliance & SBOM
Malware
Blog
Shai-Hulud 2 Malware Campaign Targets GitHub and Cloud Credentials Using Bun Runtime
November 24, 2025
Security
News
Malware
Blog
The OWASP Top 10 Gets Modernized
November 21, 2025
Open Source
News

Ebook/Report
AI SAST: Combining Agents, Program Analysis, and Rules for High-Confidence Code Security
November 19, 2025
Security
Developer Productivity
Blog
Introducing AI SAST That Thinks Like a Security Engineer
November 19, 2025
First Party Code
News
Blog
Announcing Native Support for OWASP Secure Pipeline Verification Standard
November 10, 2025
Open Source
News
Blog
Critical SQL Injection Vulnerability in Django (CVE-2025-64459)
November 6, 2025
Security
Open Source
Malware
Blog
Why AI Code Gets Less Secure With Every Prompt
October 28, 2025
AI/ML
First Party Code
Blog
From Shift Left to Shift Down: Making SAST Work for Developers
October 27, 2025
First Party Code
Opinion
Blog
Why SAST Failed (And What’s Next)
October 16, 2025
Opinion
First Party Code
Blog
Rethinking the Interface: How Agentic UX is Shaping the Future of Endor Labs
October 2, 2025
AI/ML
Tech
Blog
Why Cooldown Windows Belong in Every npm Security Strategy
September 22, 2025
Open Source
Malware
News
Blog
Zero Trust for Open Source: Why Enterprises Need a New AppSec Playbook
September 22, 2025
Open Source
Opinion
Video
Fireside Chat: Building an AppSec Program for Cursor
September 19, 2025
Security
SCA
AI/ML
Malware

Blog
How to Defend Against NPM Software Supply Chain Attacks
September 16, 2025
Open Source
Security
Malware

Blog
npm Malware Outbreak: Tinycolor and CrowdStrike Packages Compromised
September 16, 2025
Security
News
Open Source
Malware

Blog
Endor Labs Drives 225% Revenue Growth, Pioneers the Future of Secure SDLC
September 16, 2025
AI/ML
News
Blog
Major Supply Chain Attack Compromises Popular npm Packages Including chalk and debug
September 8, 2025
Security
Open Source
Malware
Blog
Nx build platform compromised by supply chain attack – How attackers collude with AI code assistants
August 27, 2025
Security
Malware
Blog
How We Cracked SCA for C/C++ Codebases
August 21, 2025
No items found.
Customer Story
Cursor Develops a Secure Product with Endor Labs
August 20, 2025
Customer Stories
SCA
Tech
Blog
When CodeRabbit became PwnedRabbit: A cautionary tale for every GitHub App vendor (and their customers)
August 20, 2025
CI/CD
Open Source
Security

Blog
Shadow AI in Your Codebase: A Hidden Supply Chain Risk
August 20, 2025
AI/ML
Open Source
Security
Customer Story
Five9 Transforms Software Supply Chain Security with Endor Labs
August 20, 2025
Customer Stories
SCA
Tech
Blog
Under the Hood: How I Vet Early-Stage Startups for Critical Security Programs
August 20, 2025
SCA
Customer Stories

Blog
The Most Common Security Vulnerabilities in AI-Generated Code
August 12, 2025
AI/ML
First Party Code
Security
Blog
The Last Mile of AI Productivity Is Code Review
August 11, 2025
AI/ML
First Party Code
Security
Video
Fireside Chat: CISOs on AI, Shift Left, and Building Trust at People.ai and AppLovin
August 7, 2025
Security
SCA
AI/ML
Video
Fireside Chat: Building a High-Trust Product Security Program at Zebra
August 6, 2025
Security
SCA
Blog
How to Detect LLM Prompt Injection Risks
August 6, 2025
AI/ML
First Party Code
Security
Blog
Why Your AI Code Assistant Might Be Shipping CVEs
August 5, 2025
AI/ML
Open Source
Security
Blog
Anti-Pattern Avoidance: A Simple Prompt Pattern for Safer AI-Generated Code
August 5, 2025
AI/ML
Security
First Party Code
Want to stay in the loop?
Sign up for our newsletter.