Endor Labs vs Snyk

Snyk was built for the cloud era. Endor Labs was built for the AI era.
Snyk reads manifests and flags what it finds. Endor Labs builds a call graph of your code and dependencies, proves which findings are reachable, and fixes them without breaking the build. Already on Snyk? We work around your contract so you're never paying for two tools.

Loved by security teams, painless for developers at:

Endor Labs delivered on its promise to make SCA way more efficient and bubble up what actually matters much quicker.
Idan Fast
Co-Founder & CTO, Grip Security

Why customers choose Endor Labs over Snyk
Only the findings that matter
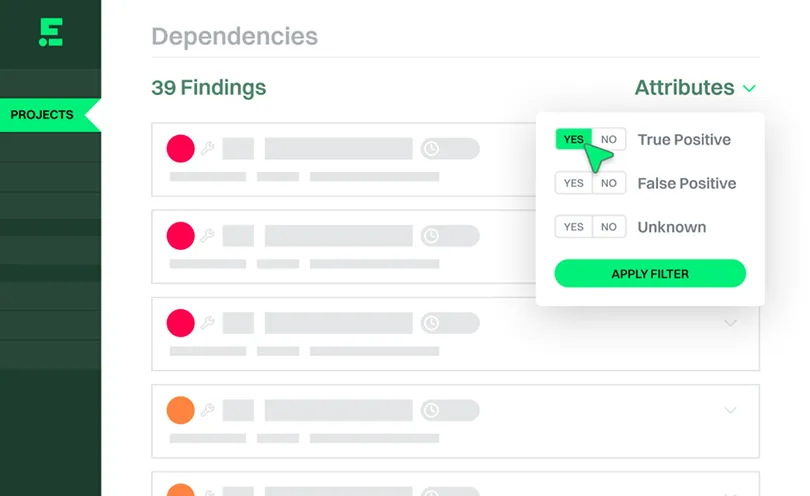
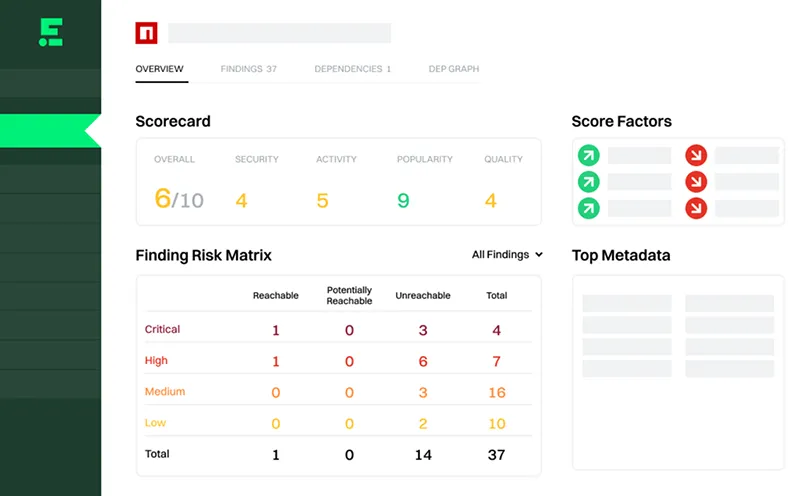
Function-level reachability across direct and transitive dependencies, with the call path on every finding. Customers see 92% fewer SCA findings on average.
Fixes that don't break the build
Upgrade Impact Analysis shows what an upgrade breaks before anyone merges. When no upgrade works, Endor Patches backport the fix.
Secure code by default
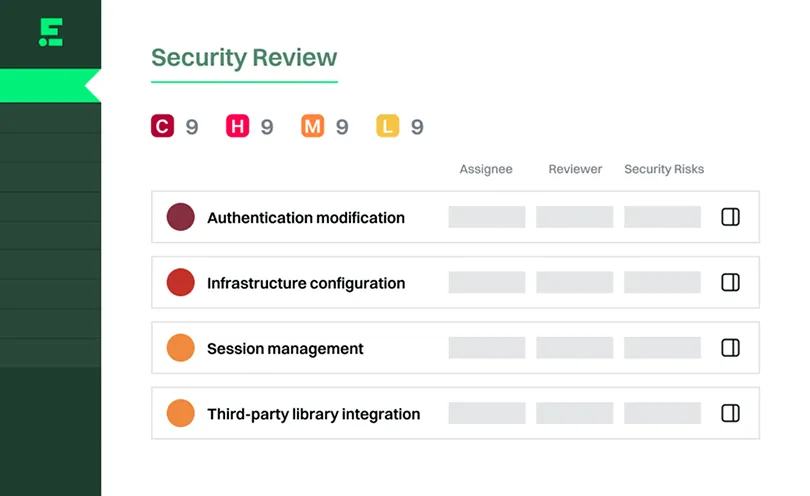
Reachability, upgrade context, and a security review run inside Cursor and Claude Code through our MCP server. No agent to install on every machine.

How Endor Labs compares to Snyk

Snyk
Platform
MCP Server for AI Agents
Features a native MCP server for modern, agent-based risk detection across the SDLC.
Snyk Studio ships an MCP server, but it runs on manifest-based SCA with reachability in three languages and no upgrade-impact context, and Evo governance needs an agent installed on every developer machine.
API-First Architecture
Designed API-first so every platform capability is fully accessible for custom automation and headless operation.
Offers limited and frequently changing APIs that are difficult to use for reliable enterprise automation.
Granular Policy Engine
Uses a flexible, customizable Rego-based engine for highly specific security enforcement at scale.
Policies are limited to basic "if this, then that" logic, making it difficult to implement sophisticated automation.
Secure Scanning Environment
Offers flexible deployment options that allow for scanning code without it ever leaving your secure environment.
Cloud-only. Snyk Code Local Engine is deprecated and no new on-prem deployments are onboarded.
Software Composition Analysis (SCA)
Direct, Transitive, and "Phantom" Dependencies
Correlates manifest data with source code and the file system to find 100% of dependencies, including those not declared in manifests.
Relies on manifest-only scanning that misses "phantom" dependencies and hidden risks in complex environments.
Function-Level Reachability
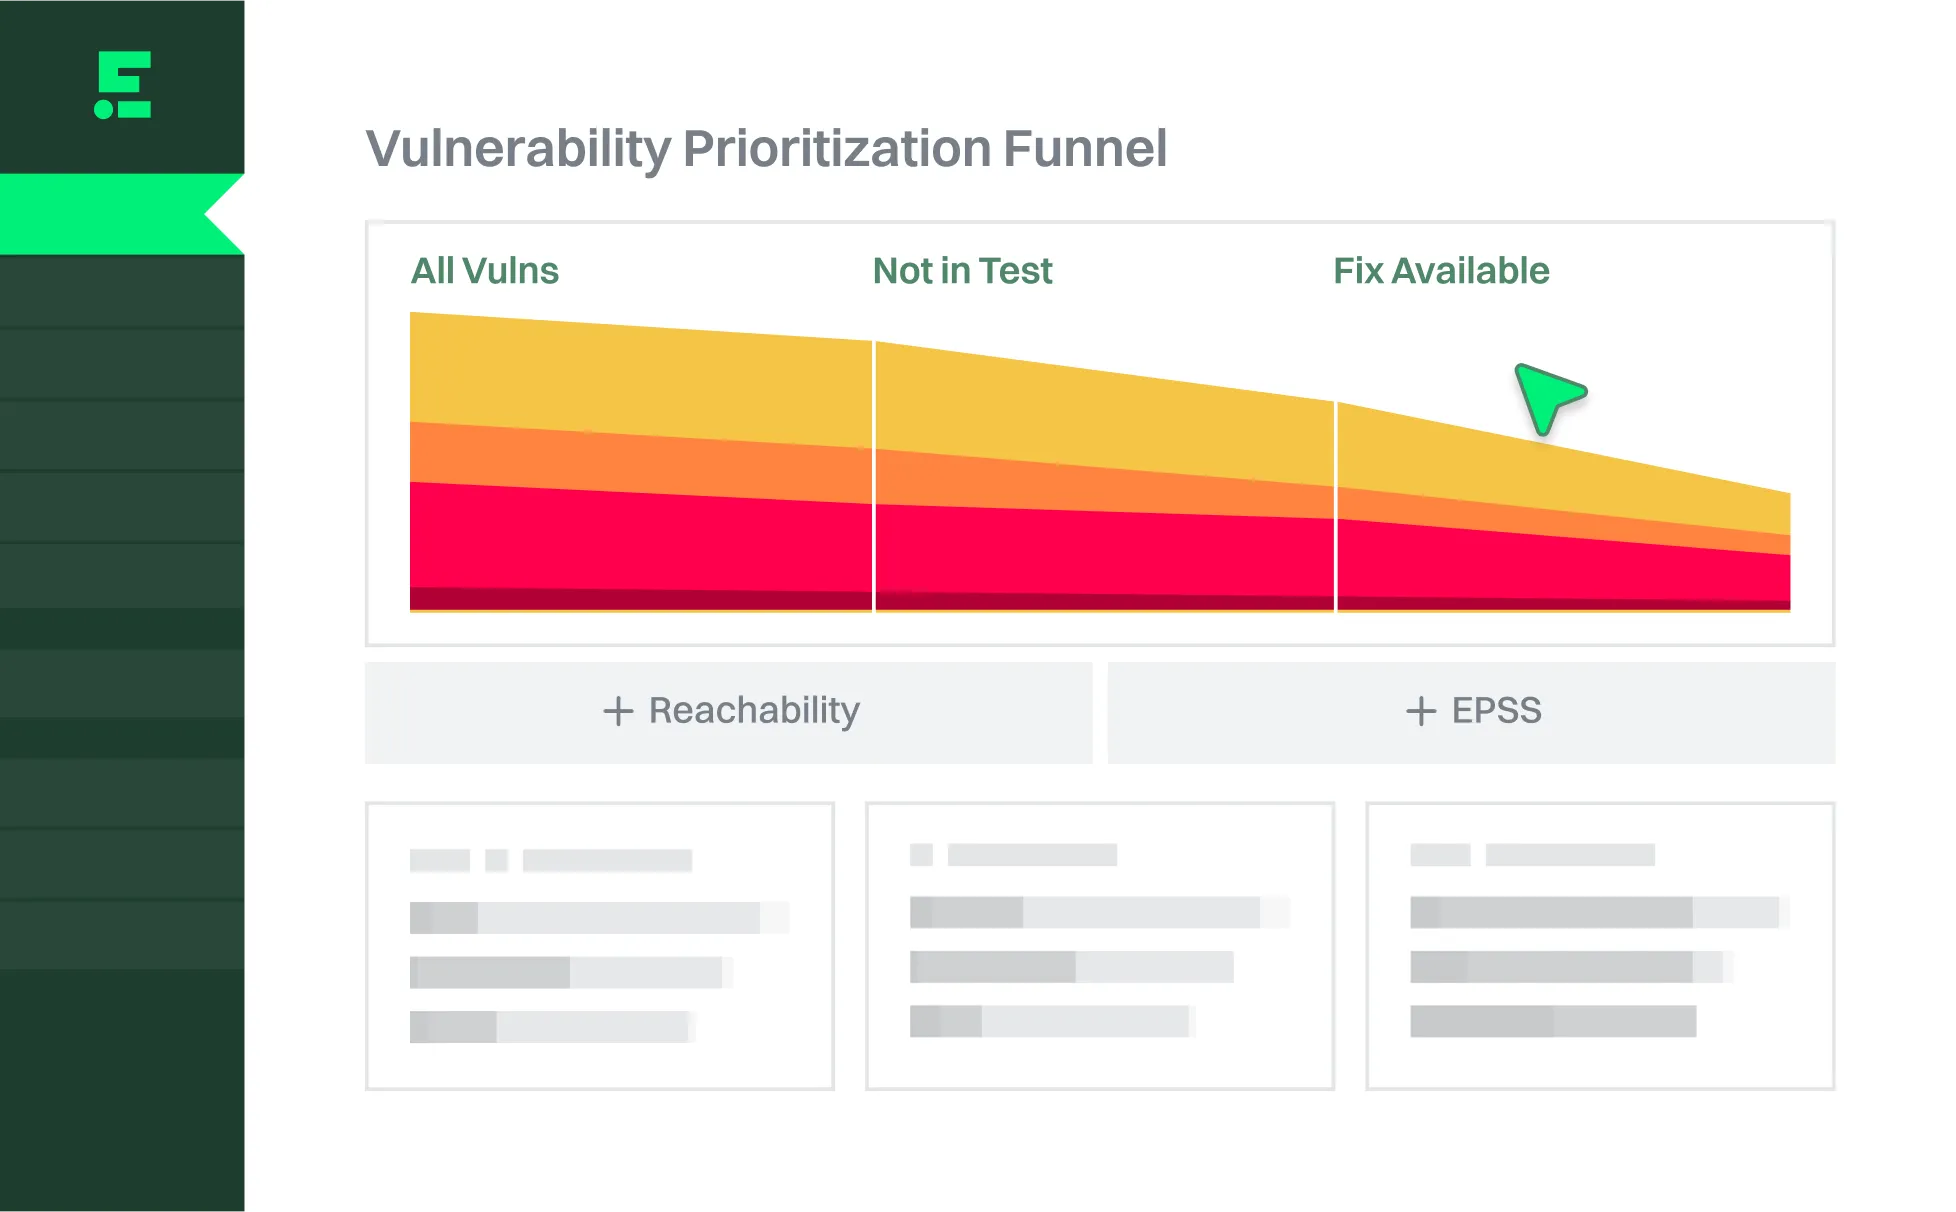
Builds a complete call graph to eliminate up to 95% of non-exploitable findings by verifying if vulnerable functions are actually called.
Reachability is GA for Java, JavaScript/TypeScript, and Python only; C# and the CLI are early access. No container reachability, and no documented call paths into transitive dependencies.
Multi-Faceted Prioritization
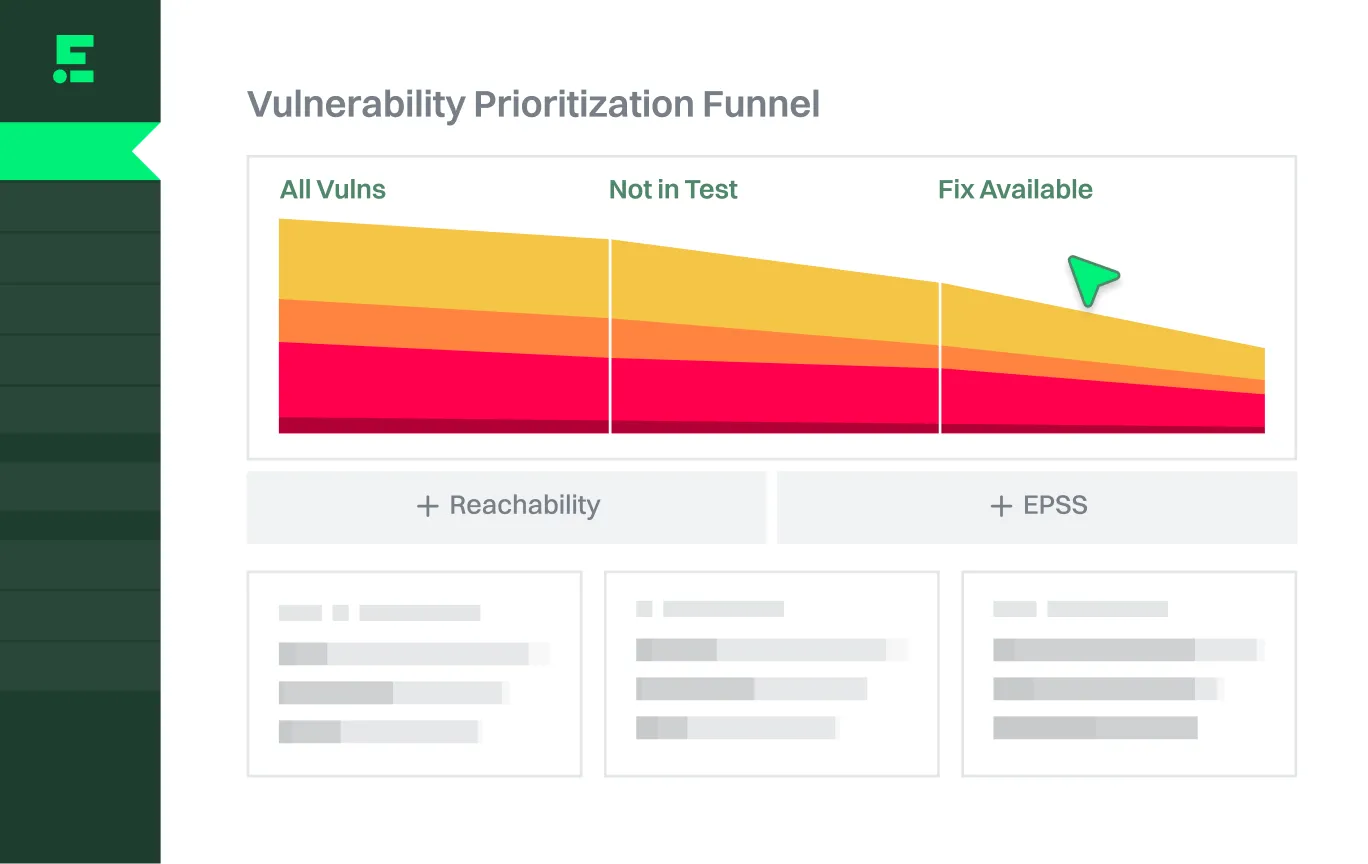
Combines reachability, EPSS, and fix availability to focus teams on the most critical, actionable risks.
Risk Score blends EPSS and exploit data, but it sits on manifest-inferred dependencies that Snyk's own docs say "may be partial."
Coding Agent Governance
Governs what coding agents do and the code they write through native hooks and one policy engine. No endpoint agent. Package Firewall blocks bad packages at install.
Evo ADS governs agents through software installed on every developer machine via Jamf or Intune, billed per active machine per day.
OSS Upgrades and Breaking Changes
Performs upgrade impact analysis to ensure fixes won't break application functionality.
Breakability (Enterprise only) has an LLM read release notes and changelogs to guess risk. No portfolio-wide view, no backported patches.
Patching Hard-to-Upgrade Vulnerabilities
Provides Endor Patches to secure critical vulnerabilities when a version upgrade is not feasible or safe.
Offers no native patching capability, forcing teams to choose between remaining at risk or breaking their code.
Malicious Code Detection
Uses behavior-based analysis to natively detect typosquatting and suspicious package behavior.
Install-time blocking is in private preview for npm and PyPI only. GA protection is a severity threshold in Artifactory Gatekeeper, after the package is already published.
Unmaintained and Unpinned Dependencies
Surfaces operational risks and flags unused dependencies for removal to reduce the attack surface.
Surfaces everything in the manifest regardless of use, creating significant noise and research work for developers.
Modern Build Systems (Bazel, C/C++)
Provides best-in-class, functional support for Bazel, C/C++, and modern package managers like UV.
Bazel works only through the Dep Graph API, for Bazel 7 and Open Source scans. SCM scans hit API limits above 100,000 files. uv support is early access.
Transparency and Scan Accuracy
Transparently reports any scan failures or challenges so teams never have a false sense of security.
Suffers from widespread "silent failures" during imports and scans that make results difficult to trust or diagnose.
SAST
Multi-Agent Review for Business Logic
Uses specialized AI agents to assess code context and automatically prioritize complex logic flaws.
Rules-based data-flow engine with monthly rule drops and no LLM triage pass, so logic, auth, and AI-era flaws that rules can't express go undetected.
OWASP Top 10 and CWE Visibility
Employs AI-native analysis and transparent, explainable results to provide high-fidelity filtering of top security risks.
Uses a "black box" rule engine with limited transparency into detection logic, making findings difficult to verify.
Custom and Community Rules
Features interoperable rules that are easily extended to address custom internal libraries and specific configurations.
Rule Extensions (Enterprise only) let you add functions to Snyk's rules. There is no custom rule language, and Snyk's own release notes say monthly updates bring "significantly more findings."
Secrets
Hardcoded Secrets Detection
Scans full git history across every branch, validates each secret as live or not, and collapses duplicates into one finding.
Snyk Secrets shipped in August 2026 (ML plus regex). Its docs do not describe git-history scanning, live validation, or deduplication.
Containers
App and OS Layer Visibility
Provides reachability analysis to determine which OS-level packages are actually used by your application.
Lacks container reachability, leading to high false positive rates for packages that are present but never used.
SCA and Container Correlation
Automatically connects container vulnerabilities to application source code for a unified risk view.
Silos SCA and container results, requiring manual effort to determine if a vulnerability exists in the app or the OS.
Build Integrity and Artifact Signing
Secures the supply chain with built-in artifact signing and verifiable build integrity.
Lacks native features for high-integrity artifact signing and supply chain verification.
"Endor Labs reduced our SCA alerts by 76%, which let us give back 11,424 development hours.”
Black and white portrait of a man with a mustache and beard, wearing a suit and tie.
Greg Pettengill
Principal Product Security Engineer,  Five9
Protect
Proactive Protection from Malware Attacks
Protect your software supply chain from rising malware attacks. Endor Labs blocks malicious open-source dependencies early and reduces incident response
Switch
Ready to switch to Endor Labs?
Scan your entire organization in just a few clicks with apps for GitHub, GitLab, BitBucket, and Azure DevOps. Or customize your scanning experience in just about any CI pipeline with our low-code deployment options.

We’re looking for better ways to scale how we identify business logic risks and unknown unknowns in our codebase. Traditional static analysis tools haven’t really given us the lift we need. Being able to detect risks that we’d otherwise miss manually or through traditional automation would be hugely valuable.”
Mark Breitenbach
Security Engineer, Dropbox
Mark BreitenbachCompany Logo

We’re excited to partner with Endor Labs as we continue to strengthen our security posture in this AI era. Their focus on actionable insights and seamless integration aligns with our commitment to building secure, reliable products for our customers."
Mark Turner
Head of Product Security, Atlassian
Mark TurnerCompany Logo

Endor Labs' native Bazel integration is the best on the market. It’s eliminated the previous complexity, delivering the confidence required to shift left and reliably identify/remove unused dependencies."
Kevin Vaughan
Sr. Manager Information Security, Rubrik
Kevin VaughanCompany Logo

I truly love what EndorLabs does to the security landscape. My brain explodes every time I see a new feature being rolled out. For example, the recent C/C++ support got me wondering how they managed to solve this for a language without a standard package manager and manifest file support."
Mohanraj Ravichandran
Product Security Engineer, Netskope
Mohanraj RavichandranCompany Logo

Since switching from our previous SCA tool, Endor Labs has cut the findings we send to developers by 95%, which returned time to ship features faster, and helped us remediate exploitable vulnerabilities quickly with precise reachability and clear upgrade guidance."
Shreyas Sriram, Security Engineer
Robinhood‍
Shreyas Sriram, Security EngineerCompany Logo

Endor Labs represents the next major innovation in application security. We believe that the reachability analysis provided by Endor Labs will be a must-have technology for enterprises, focusing developers’ efforts on only the most critical and reachable vulnerabilities and saving them countless hours."
Matt Carbonara
Head of Enterprise Tech Investing, Citi Ventures
Matt CarbonaraCompany Logo

As a fast-growing AI company, we prioritize feature velocity without compromising security. Endor Labs’ unique reachability-based analysis and native integrations into our AI-native software development stack keep our developers focused on rapidly finding and fixing real risks in the SDLC, so we ship faster with confidence."
Sunil Agrawal
CISO, Glean
Sunil AgrawalCompany Logo

As a society, we are going to generate more and more code. I am confident that Endor Labs is the AppSec platform of choice if you want to be on the cutting edge of where software development is going.”
Aman Sirohi
SVP - Chief Security Officer & Platform, People.ai
Aman SirohiCompany Logo

FAQs

How does Endor Labs’ approach to prioritizing vulnerabilities differ from Snyk?

Snyk primarily relies on manifest-based scanning, which often results in high false-positive rates and missed dependencies. In contrast, Endor Labs uses function-level reachability analysis to build a complete call graph of your application code. This allows security teams to focus on the vulnerabilities that are actually reachable and exploitable, rather than drowning in a mountain of irrelevant alerts.

Why do developers frequently prefer Endor Labs over Snyk?

Developers often ignore Snyk's alerts because they lack context and result in noisy alerts that disrupt their workflow. Endor Labs meets engineers where they work by providing tailored context and clear evidence for why a finding matters as well as an automated remediation path. By reducing the findings sent to developers by up to 95%, Endor Labs rebuilds trust and allows teams to ship features faster.

Does Endor Labs find dependencies that Snyk misses?

Traditional tools like Snyk often miss "phantom dependencies" that aren't declared in manifest files. Endor Labs ensures 100% visibility by correlating manifest data with the source code and actual file system. This comprehensive approach allows Endor Labs to identify significantly more dependencies and vulnerabilities in complex projects than manifest-only scanners.

Is Endor Labs slower than Snyk because of its deeper analysis?

While Snyk may emphasize fast scans, speed is a trade-off for depth; shallow scans often miss critical risks or create more downstream triage work. Endor Labs offers flexibility, providing quick scans for immediate feedback and deep scans to prioritize remediation with engineering teams. Ultimately, the time saved by having accurate, reachable results far outweighs the seconds saved during an initial scan.

Can Endor Labs automate security workflows as effectively as Snyk?

Endor Labs is built API-first by design, allowing for seamless automation and integration that Snyk’s often-limited or frequently changing APIs struggle to support. It features a customizable Rego-based policy engine that offers significantly more flexibility than Snyk’s basic "if this, then that" logic. This enables organizations to automate triage and route findings to the correct teams without manual intervention.

Does Endor Labs offer the same breadth of coverage as the Snyk platform?

Endor Labs provides a comprehensive, AI-native platform covering SCA, SAST, Secrets, Containers, and AI Governance. Unlike Snyk’s siloed approach, Endor Labs correlates findings across these layers—for example, connecting container vulnerabilities directly to your application source code. This provides a unified view of your risk posture and ensures that security teams are not managing disconnected tools.

How does Endor Labs ensure the security of the software supply chain beyond just finding CVEs?

Endor Labs goes beyond basic vulnerability scanning to include malicious package detection, artifact signing, and SBOM management. Snyk's install-time blocking is in private preview for npm and PyPI; Endor Labs Package Firewall is generally available across seven ecosystems and blocks packages before install scripts run. Additionally, Endor Labs supports high-integrity SBOMs and VEX documents, making it easier for teams to meet strenuous compliance and certification targets.

Don’t waste time researching SCA findings

Compare your projects inside Endor Labs, for free.