Fix CVEs 6.2x faster, without breaking changes




How AURI Fix works
Your Tools, Your Languages
— All Secured

FAQs
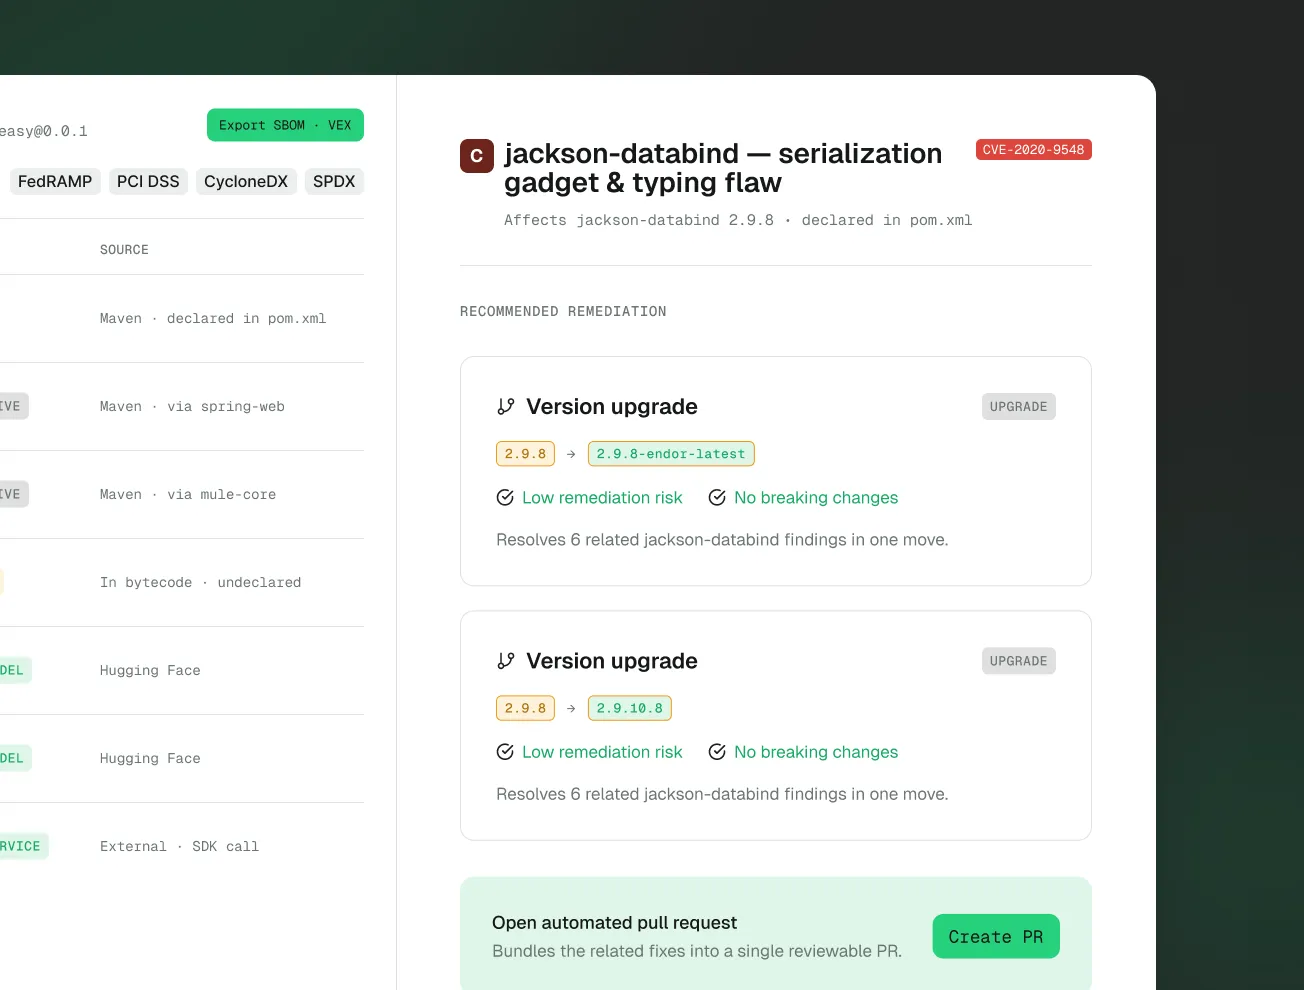
AURI Fix brings four remediation options for open source vulnerabilities under one decision engine: upgrade the dependency, mitigate in your own code, patch the dependency, or replace it. It assesses reachability and exploitability in the context of your application, then recommends the option with the least effort, disruption, and maintenance.
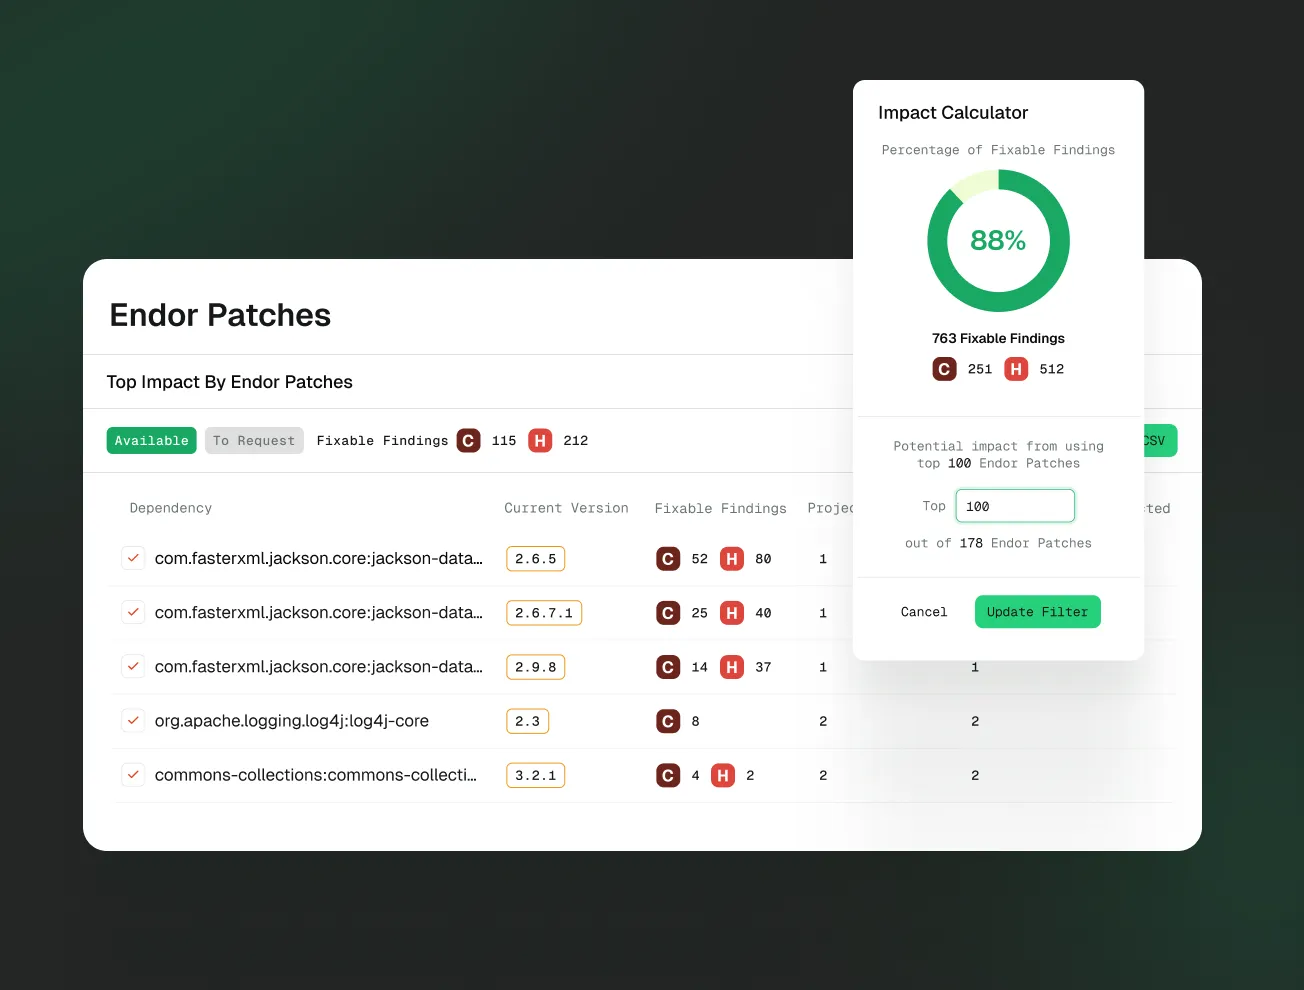
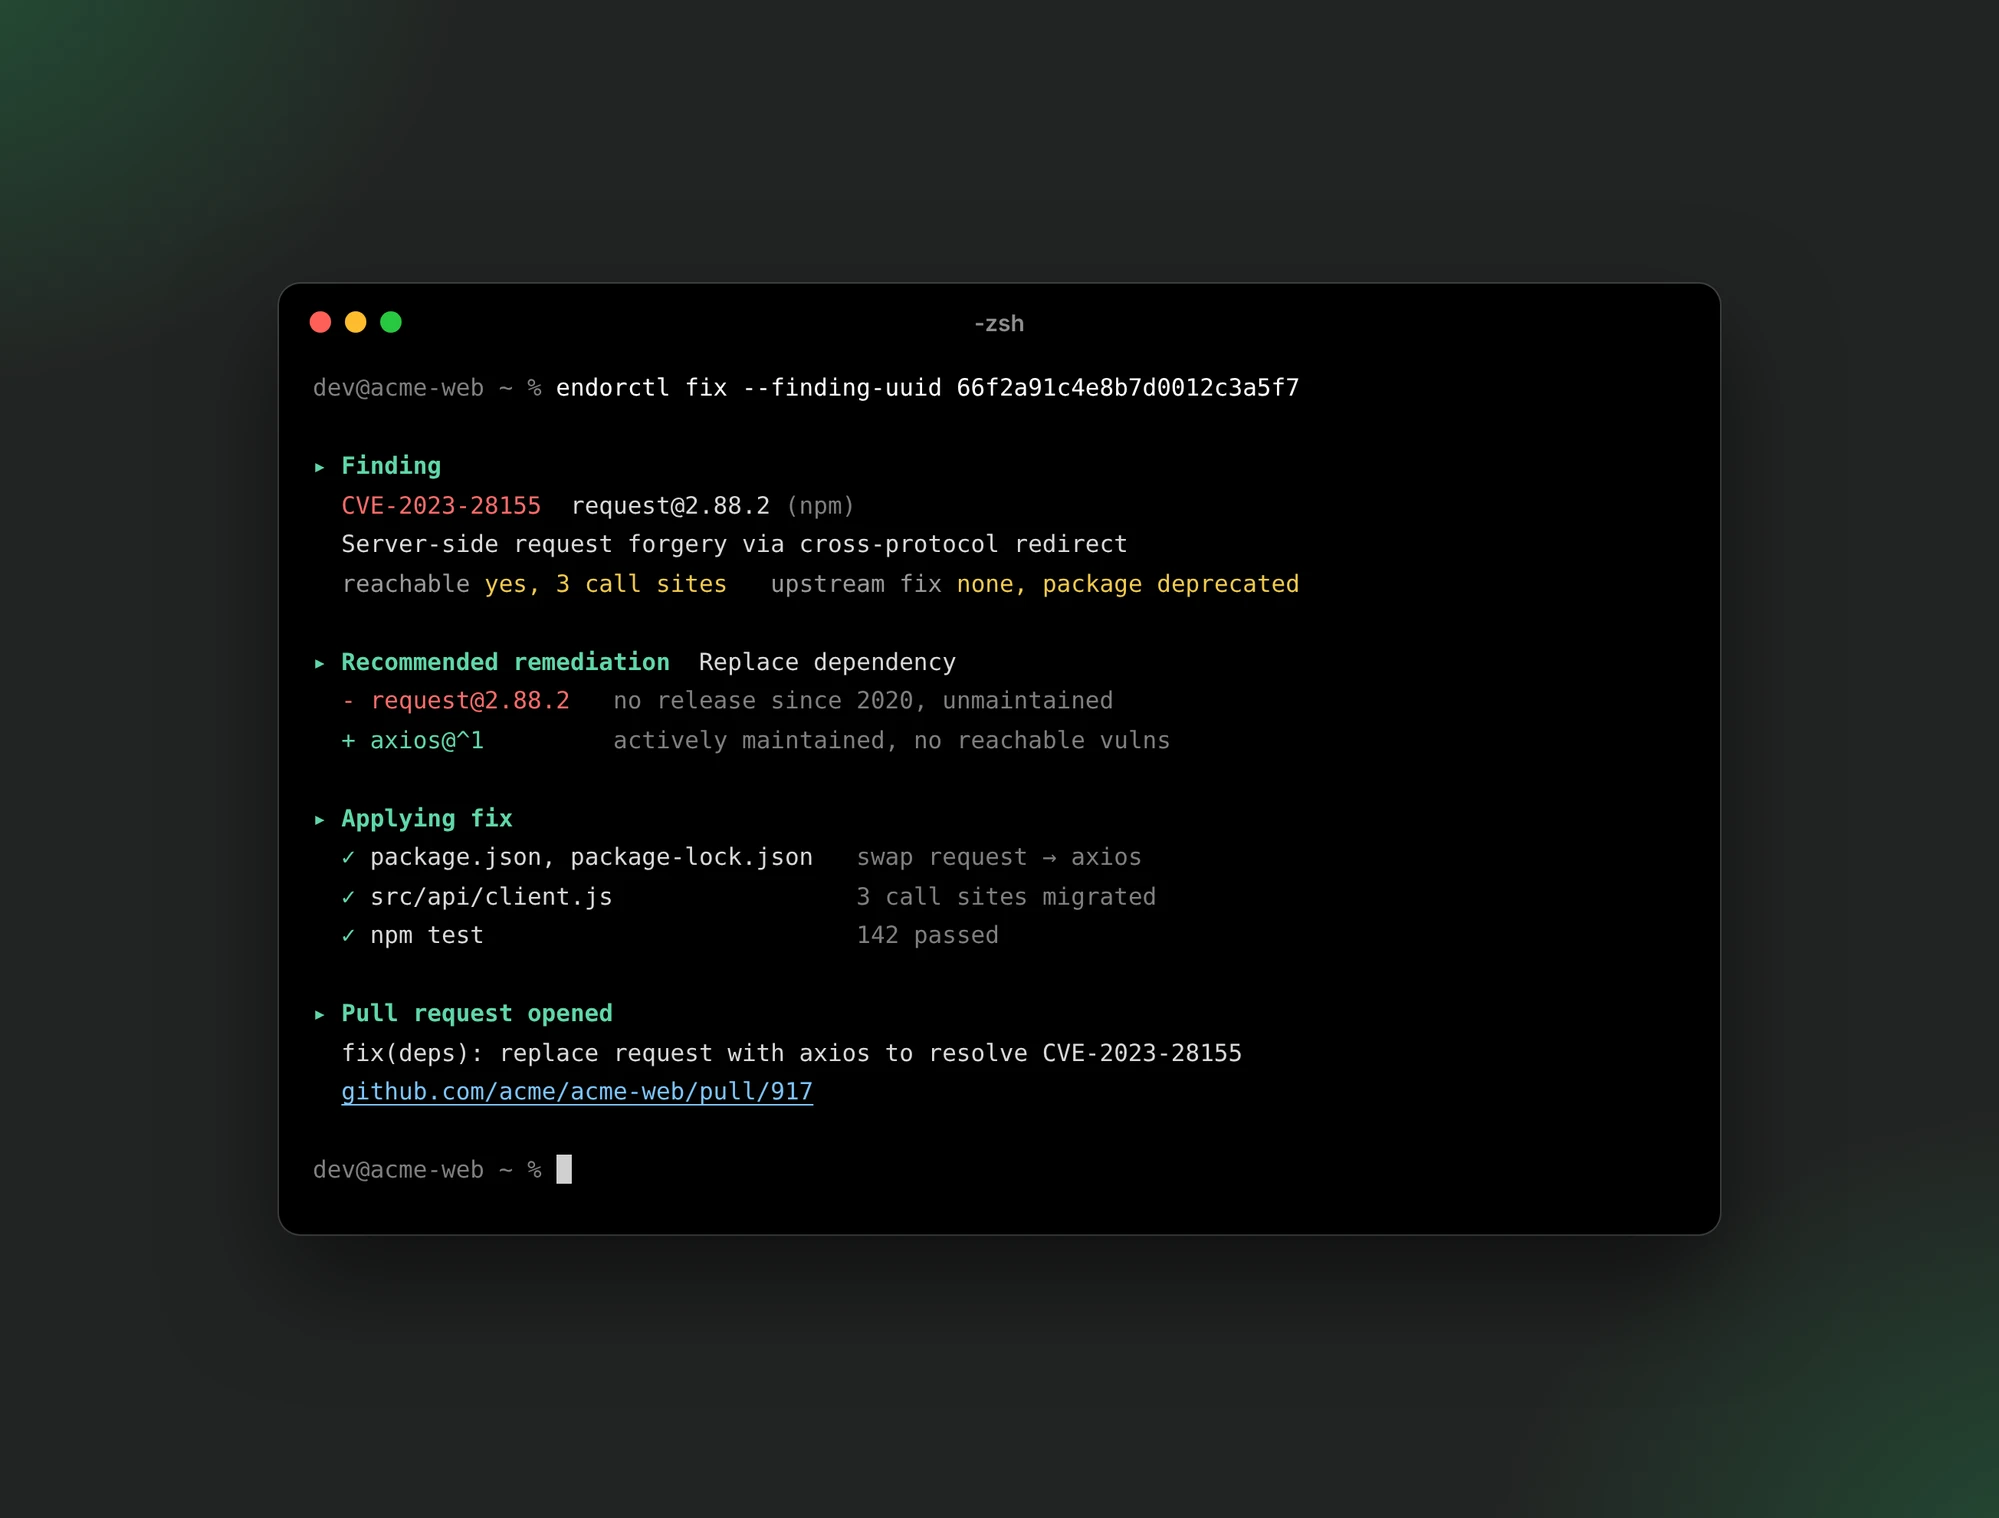
It works through a decision tree for each finding. If the vulnerability isn't reachable and exploitable, it accepts and documents the risk. If a safe upgrade exists, it opens a pull request. If the exposure comes from a configuration setting or from how your code uses the library, it applies a mitigation in your code. If the upgrade is blocked, it applies an Endor Patch. If the dependency itself is the problem, it uses Endor Scores to recommend a replacement.
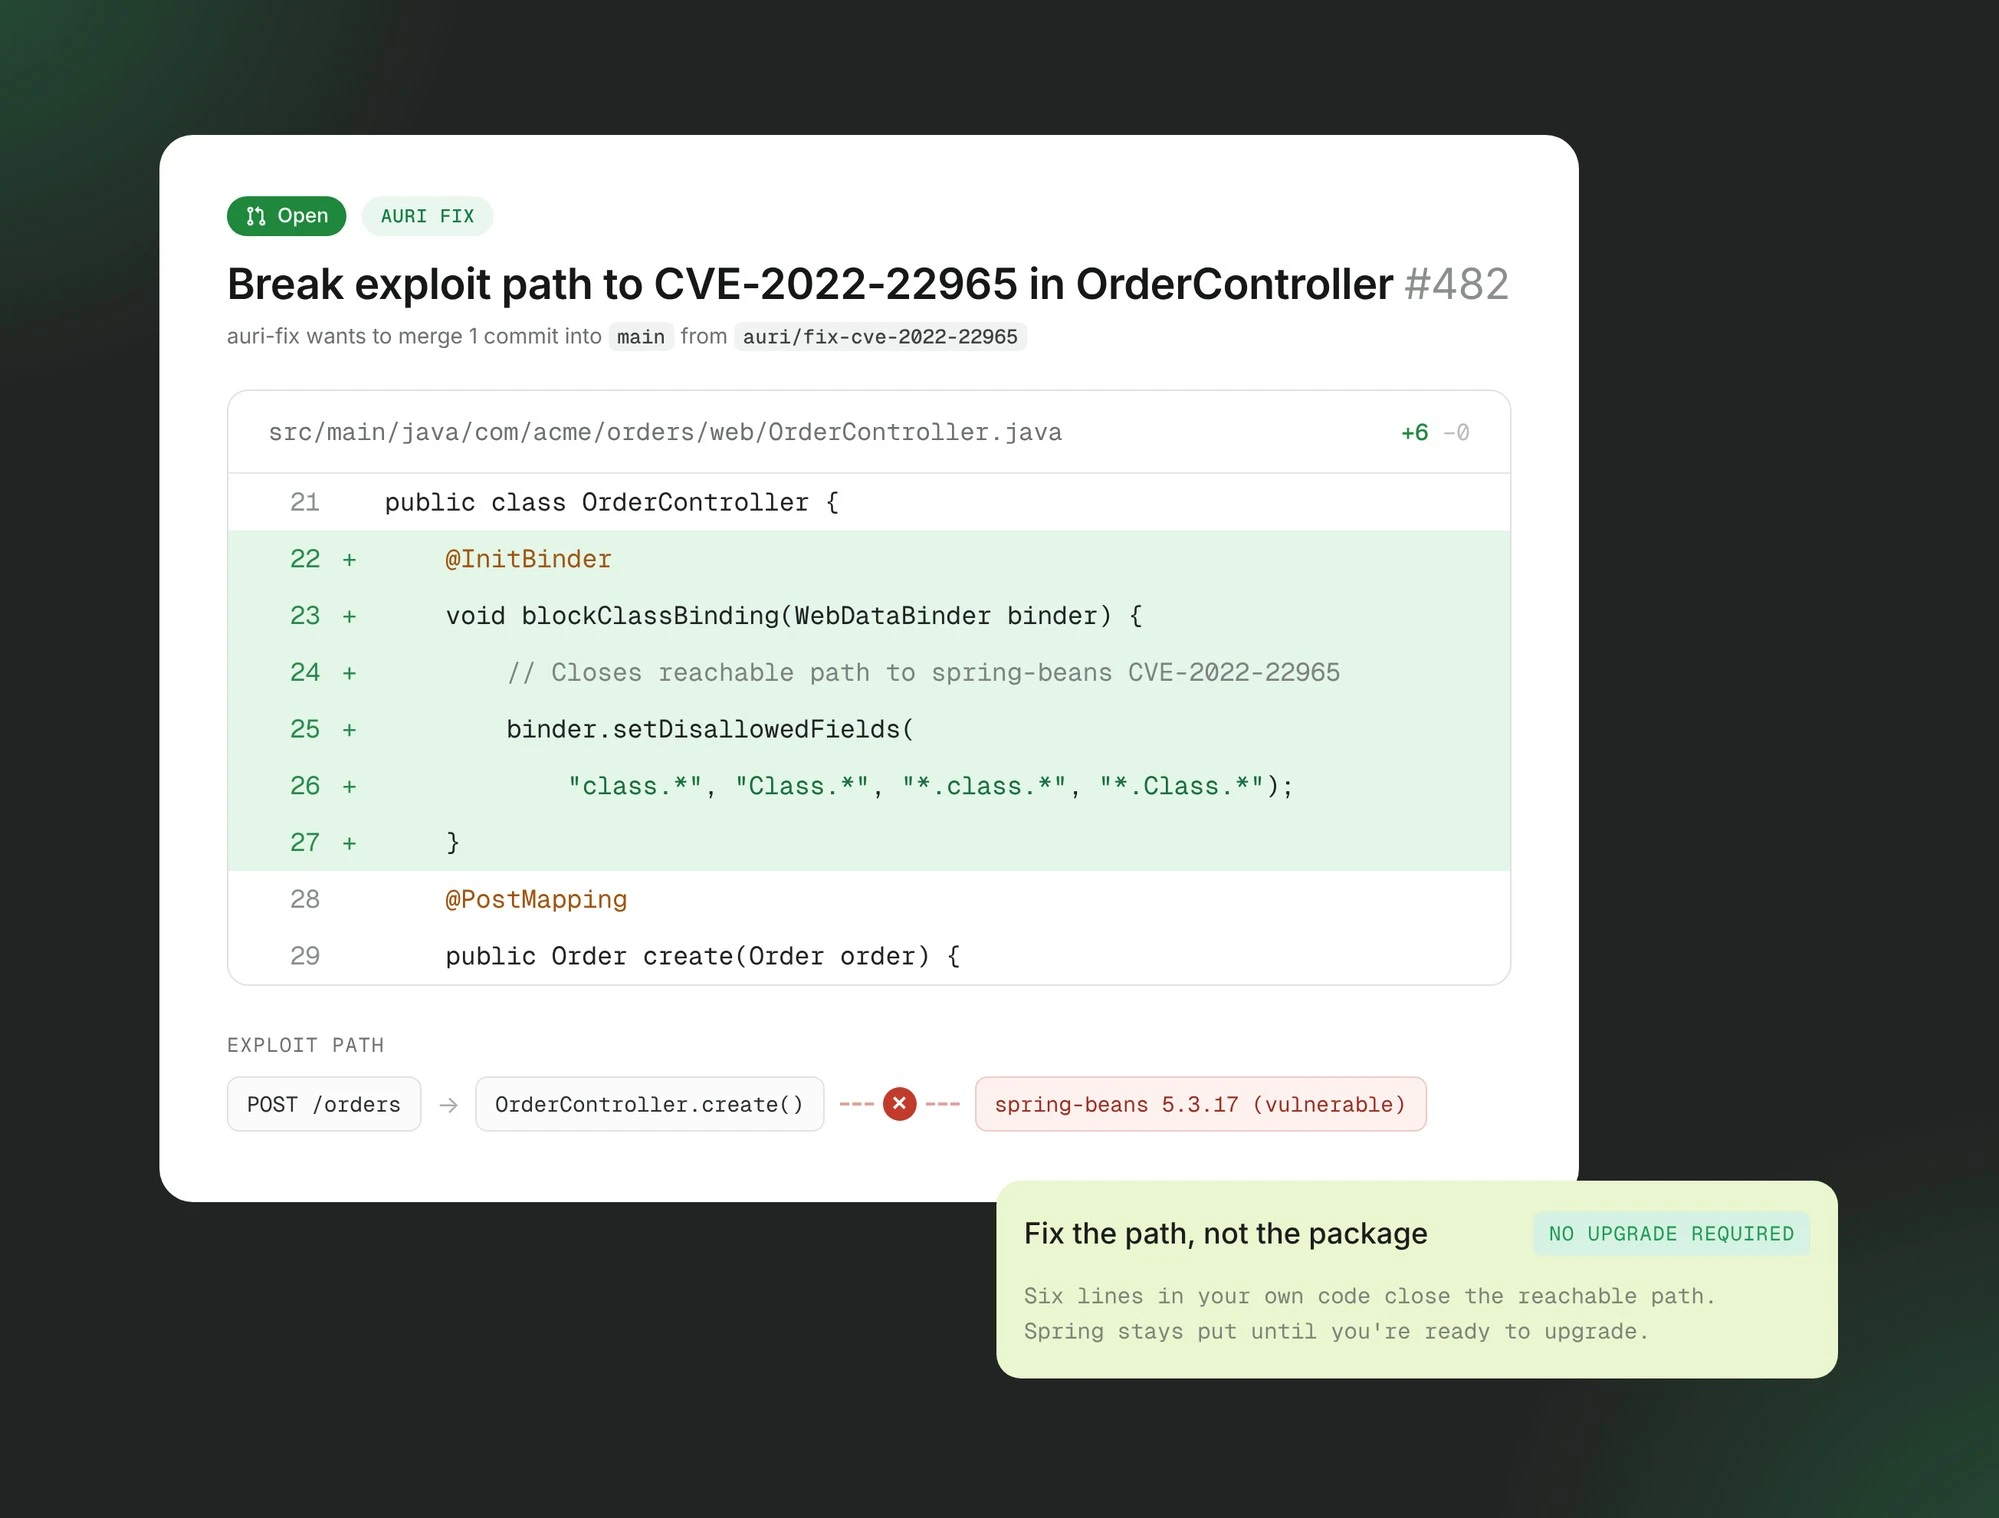
A code mitigation changes your application, not the dependency. It controls an input or changes a configuration setting so the vulnerable function can't be exploited, typically in fewer than 10 lines. Endor Patches change the dependency itself by backporting the upstream security fix to the version you already run. Code mitigation is in private beta.
Upgrade Impact Analysis scores the risk of each upgrade before work starts, code mitigations have a median size of 6 lines, and Endor Patches contain only the security fix. Every fix arrives as a pull request or a patched version that your team reviews and tests before it ships.
A code mitigation leaves the vulnerable version in place, so AURI Fix generates a VEX report with each fix that records why the vulnerability is no longer exploitable. Downstream scanners and your customers' security teams can suppress the finding based on that evidence.
Run AURI Fix from the Endor Labs CLI with endorctl fix, then choose a workflow. With policy-based workflows, the Endor Labs policy engine opens a pull request for your team to review, test, and merge. With agentic workflows, an AURI agent triages which findings to fix first, chooses the remediation method, applies the fix, and opens the pull request for your approval.