Malicious Package Detection

Stop open source malware before it runs
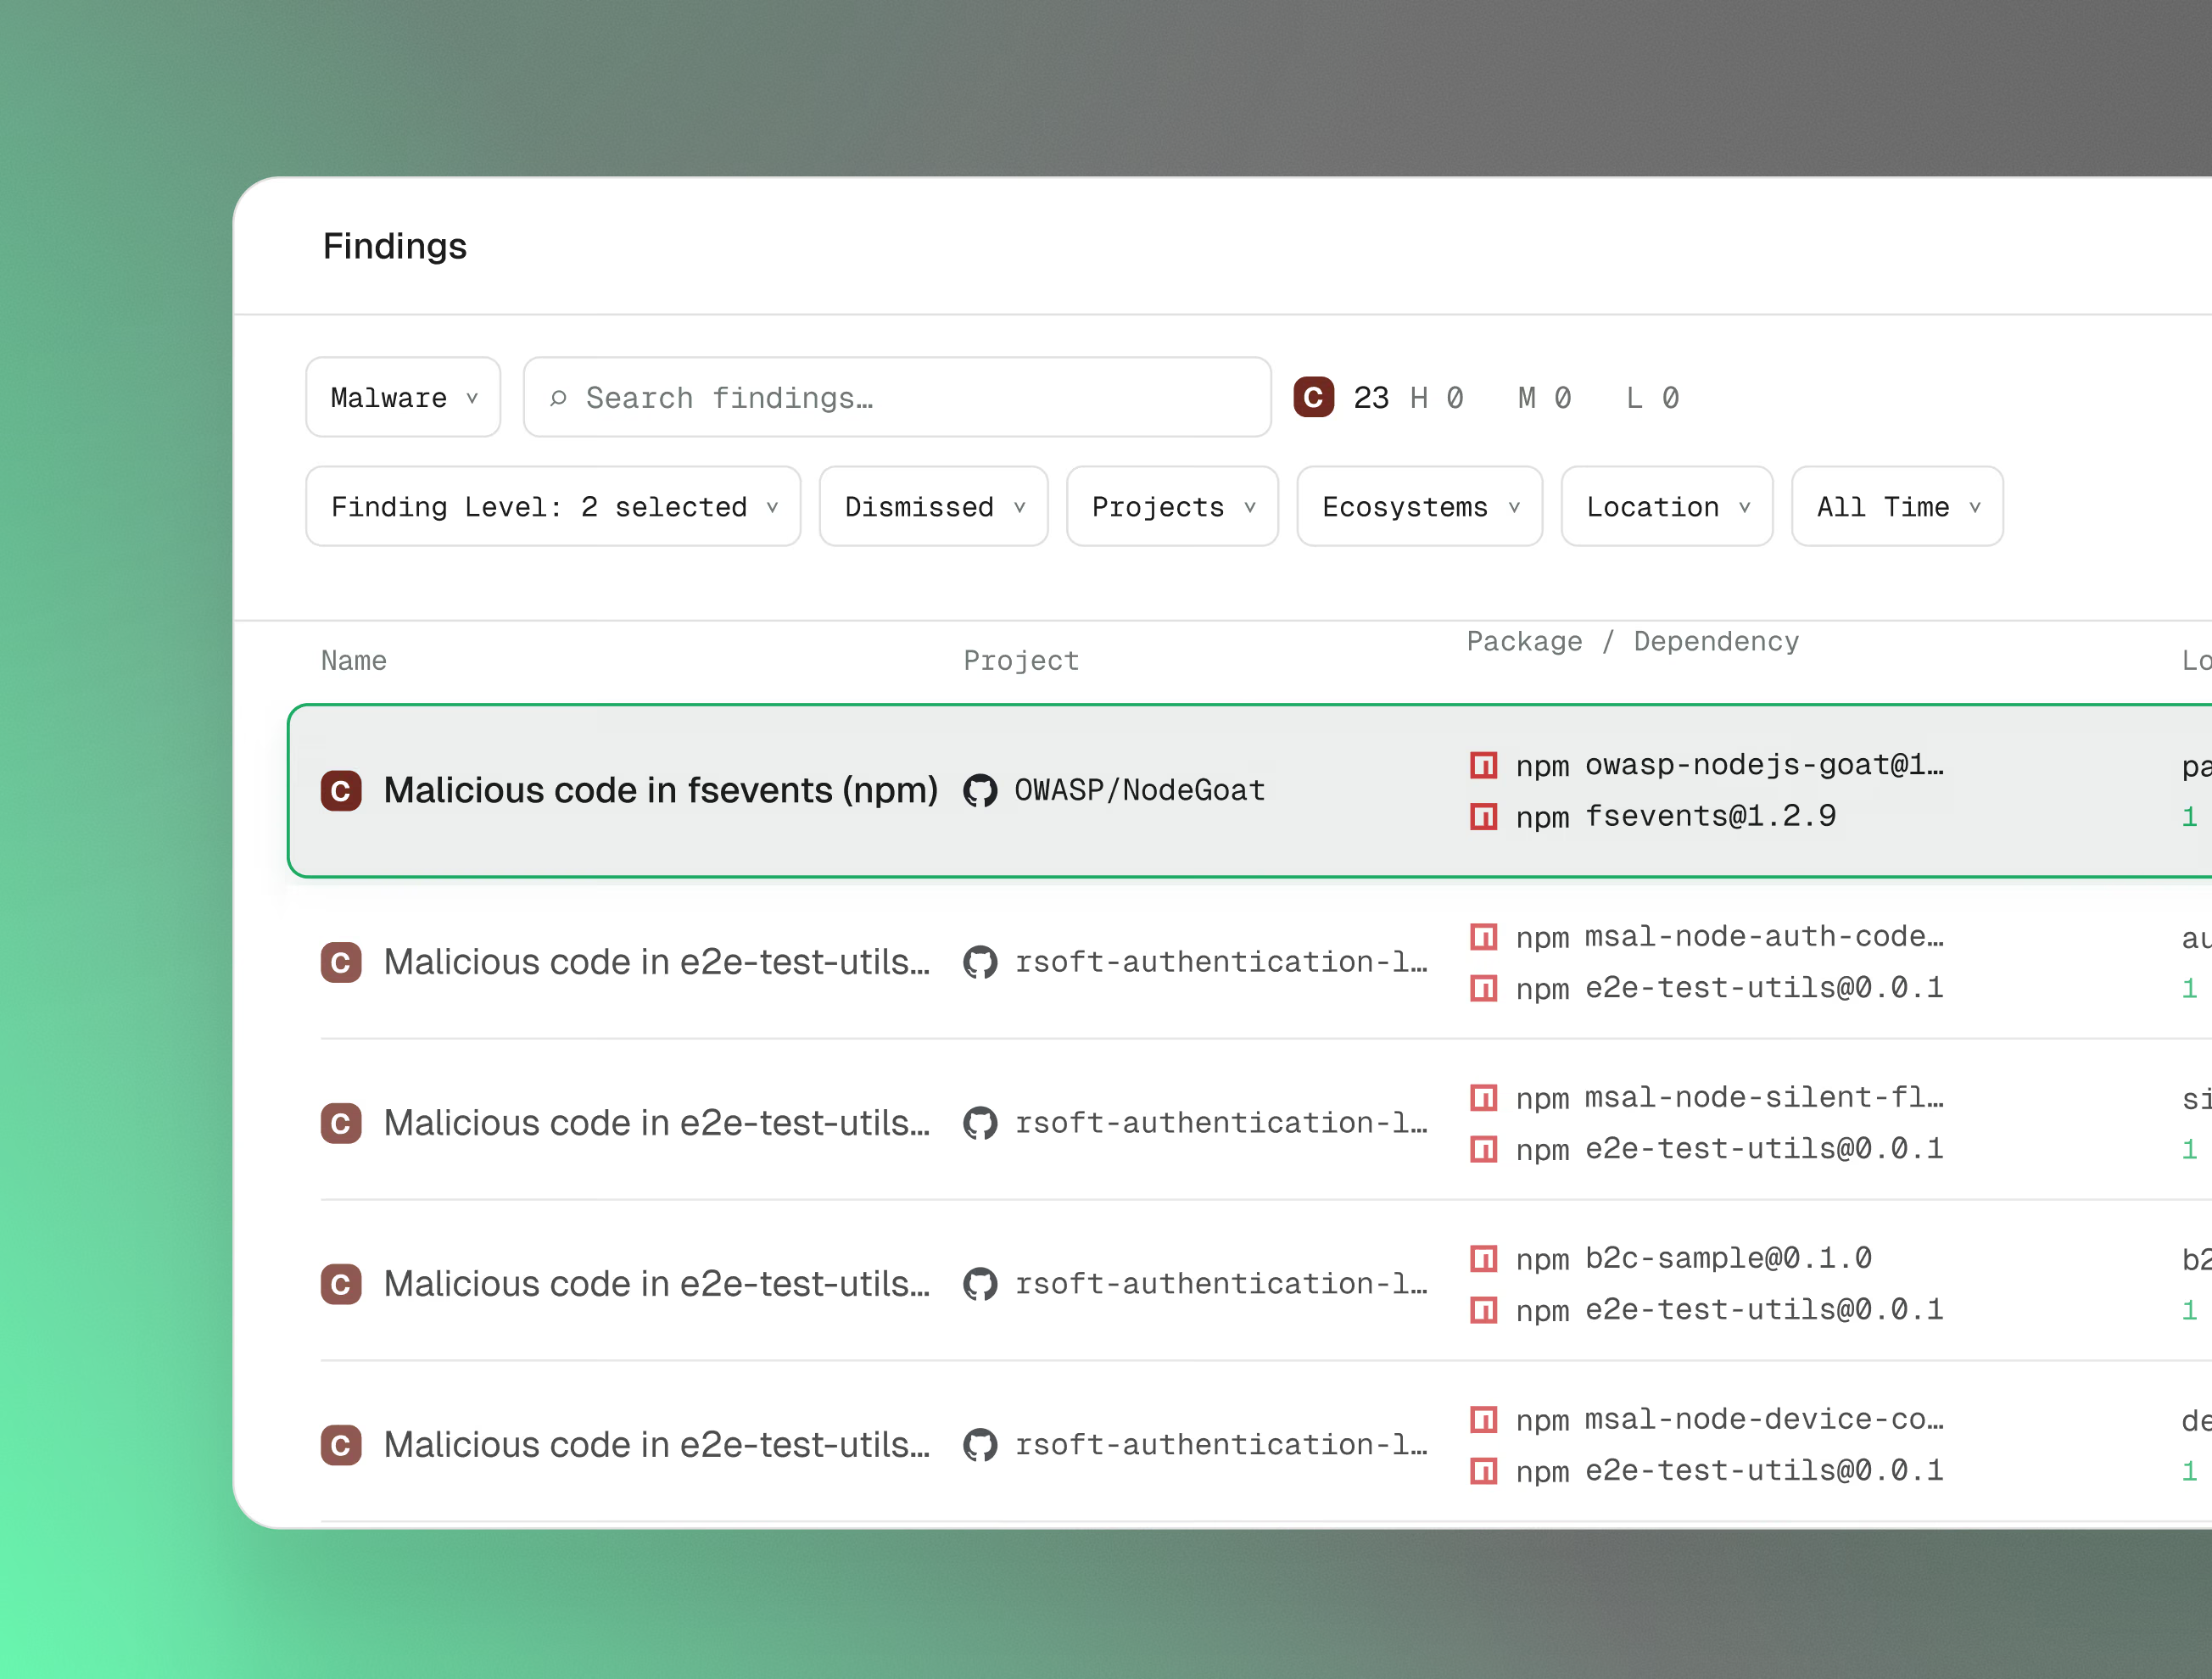
Open source malware is now its own category of supply chain risk, and AI coding agents install dependencies faster than any human can review. Malicious Package Detection scans every package across the IDE, CI, and your existing applications — catching malware public feeds miss, with expert verification from the Endor Labs security research team.
Loved by security teams, painless for developers at:

How Malicious Package Detection works
Catch malware that public feeds and CVE scanners miss
Roughly 40% of known malicious packages aren't available through public registries, and malware has no CVE — so advisory-matching scanners never see it. Malicious Package Detection scans against 150+ signals and routes unclear findings to Endor Labs researchers for verification.
Stop AI agents from installing malicious packages autonomously
AI agents install dependencies between an LLM suggestion and the next prompt, and install scripts that execute immediately — so a bad suggestion can compromise a workstation before anyone reviews it. Detection runs in the IDE before the install script ever runs.
Cut incident response time when the next campaign breaks
When a campaign like Shai-Hulud hits the news, teams can spend days hunting through repositories and lockfiles to confirm exposure. Malicious Package Detection answers 'are we affected?' across every application in minutes.
“Endor Labs' unique reachability-based analysis and native integrations into our agentic software development stack keep our developers focused on rapidly finding and fixing real risks in the SDLC, so we ship faster with confidence.”
Sunil Agrawal Photo
Sunil Agrawal
CISO, Glean
Malware intelligence
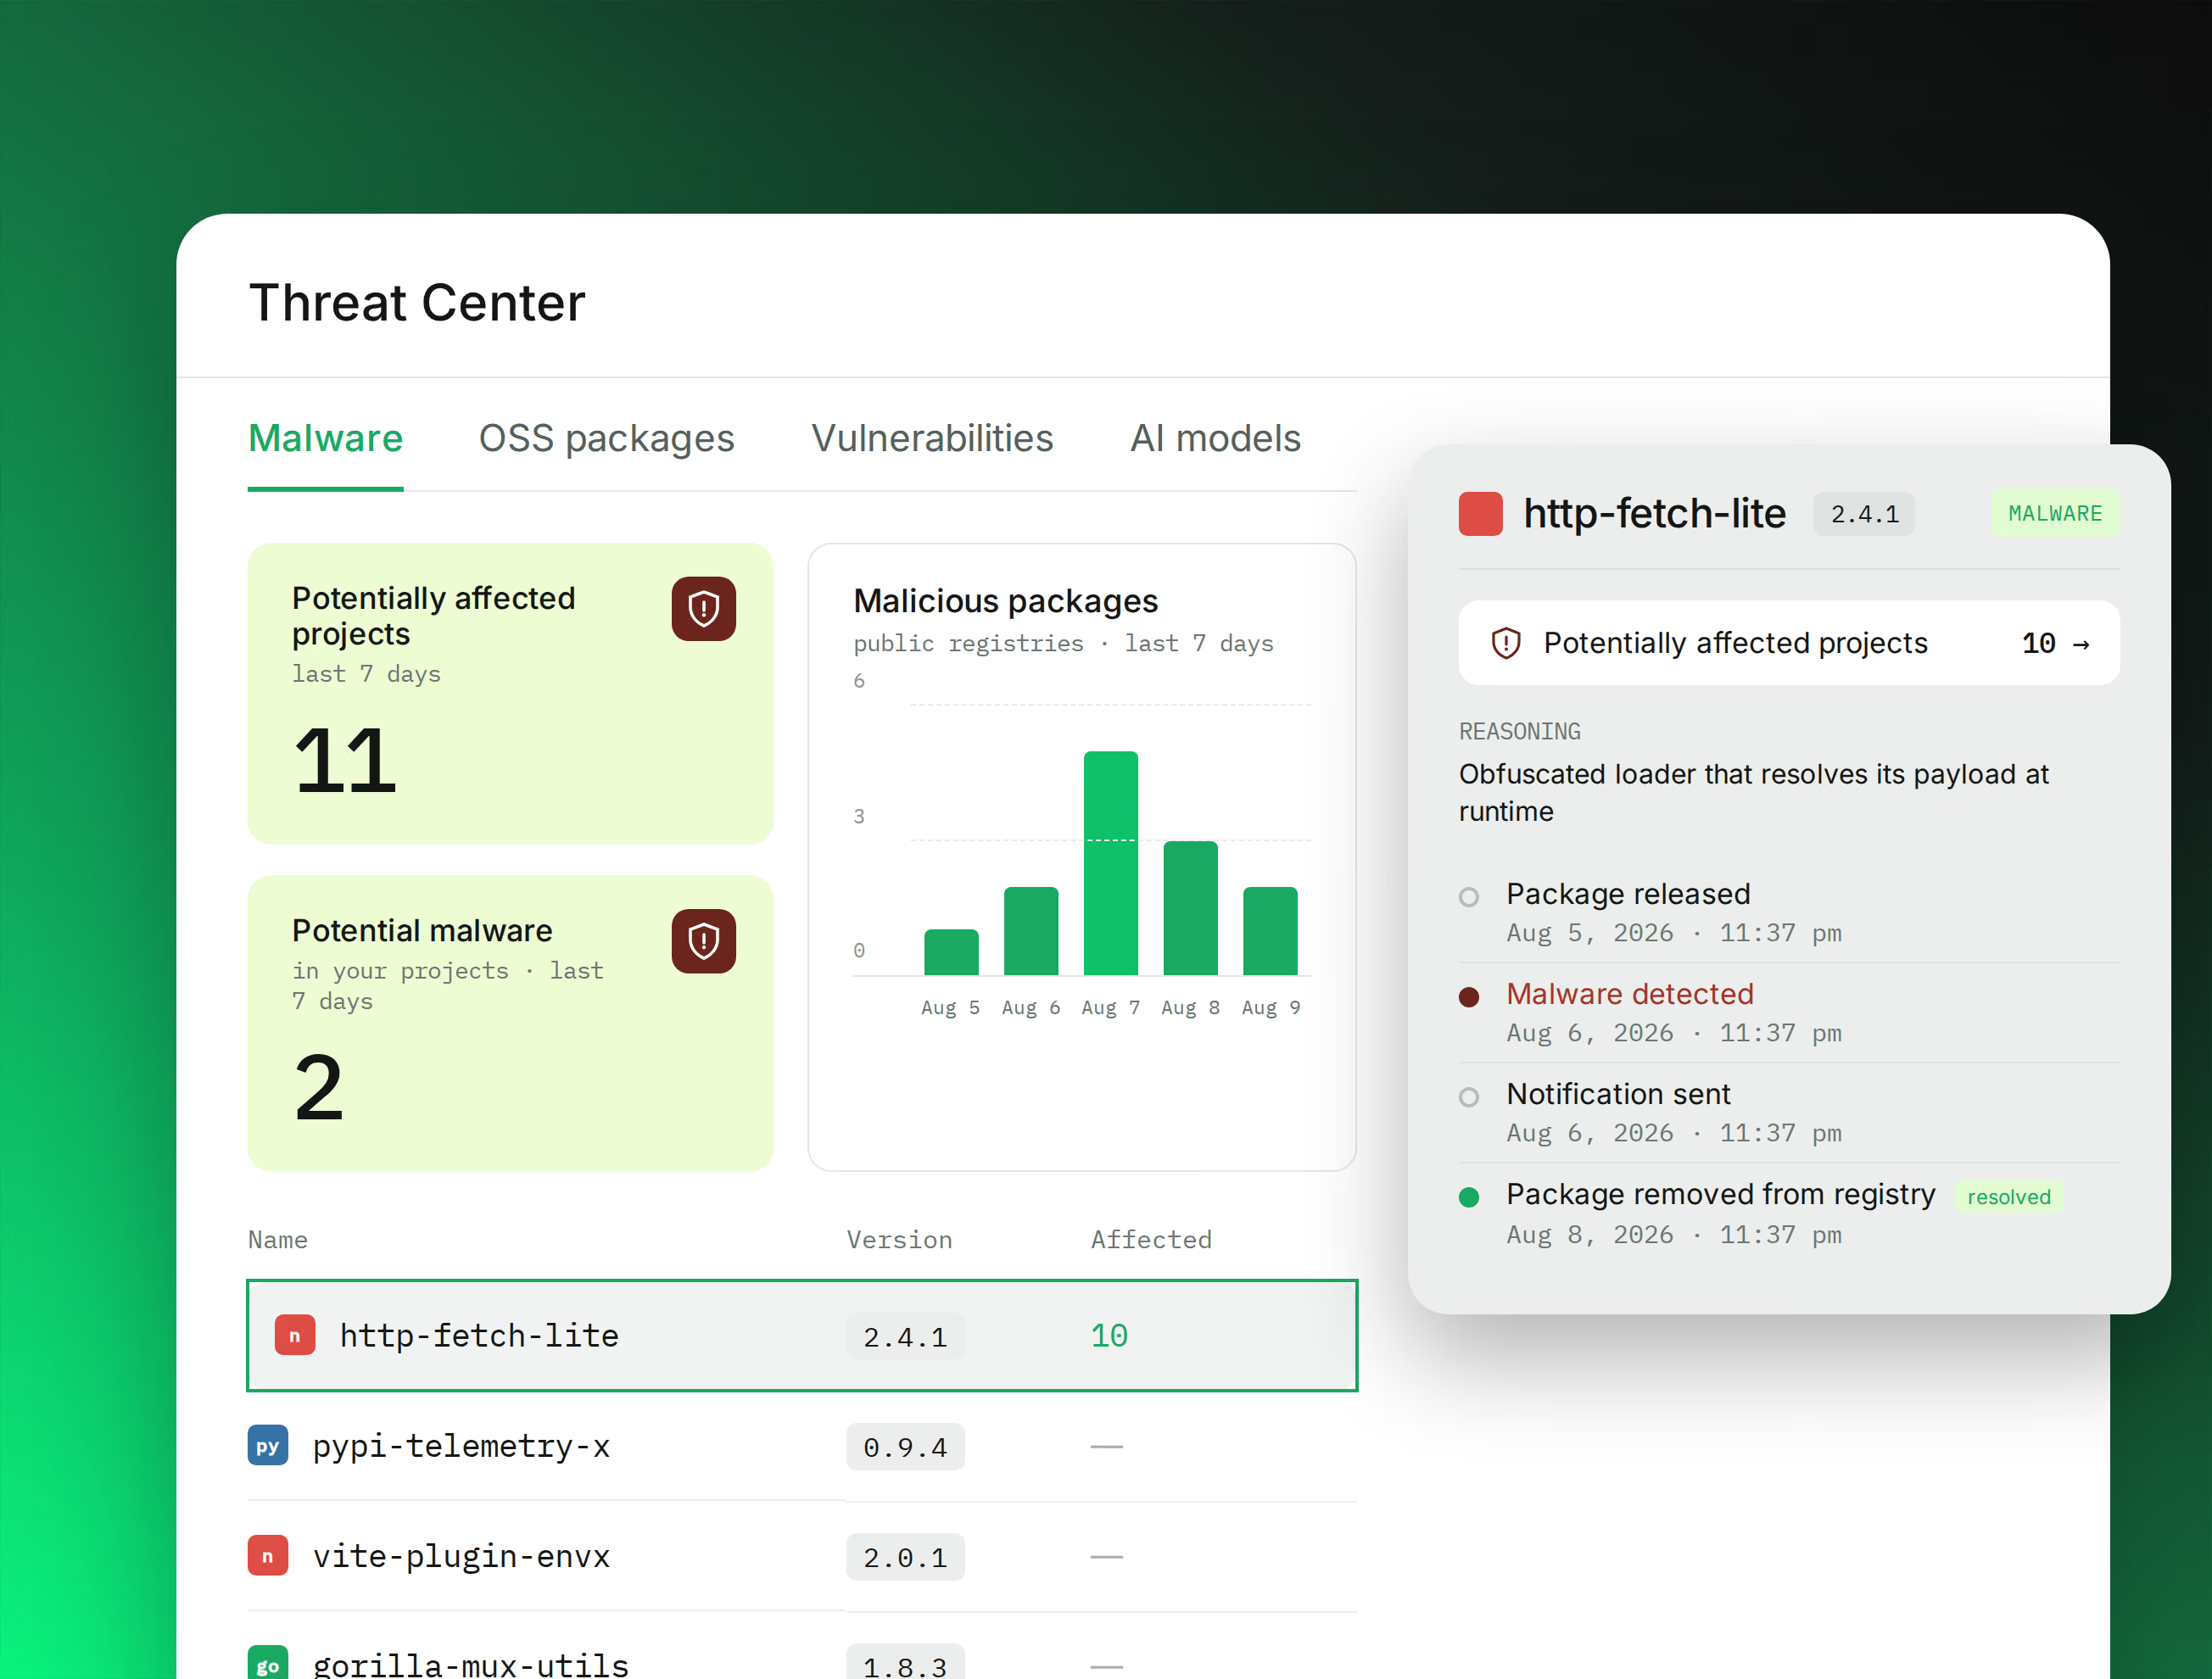
Threat Center gives a real-time view of every malware across ecosystems like npm and PyPI, mapped to your own projects.
Track confirmed malicious packages the moment they're verified, with the detection reasoning behind each finding.
Every finding is scanned against 150+ signals across 4.5M + open source dependencies and unclear results are verified by the Endor Labs security research team, so you act on confirmed threats.
Catch typosquatting, dependency confusion, obfuscated payloads, and code split across files that public feeds miss.
Learn more
Pre-install detection
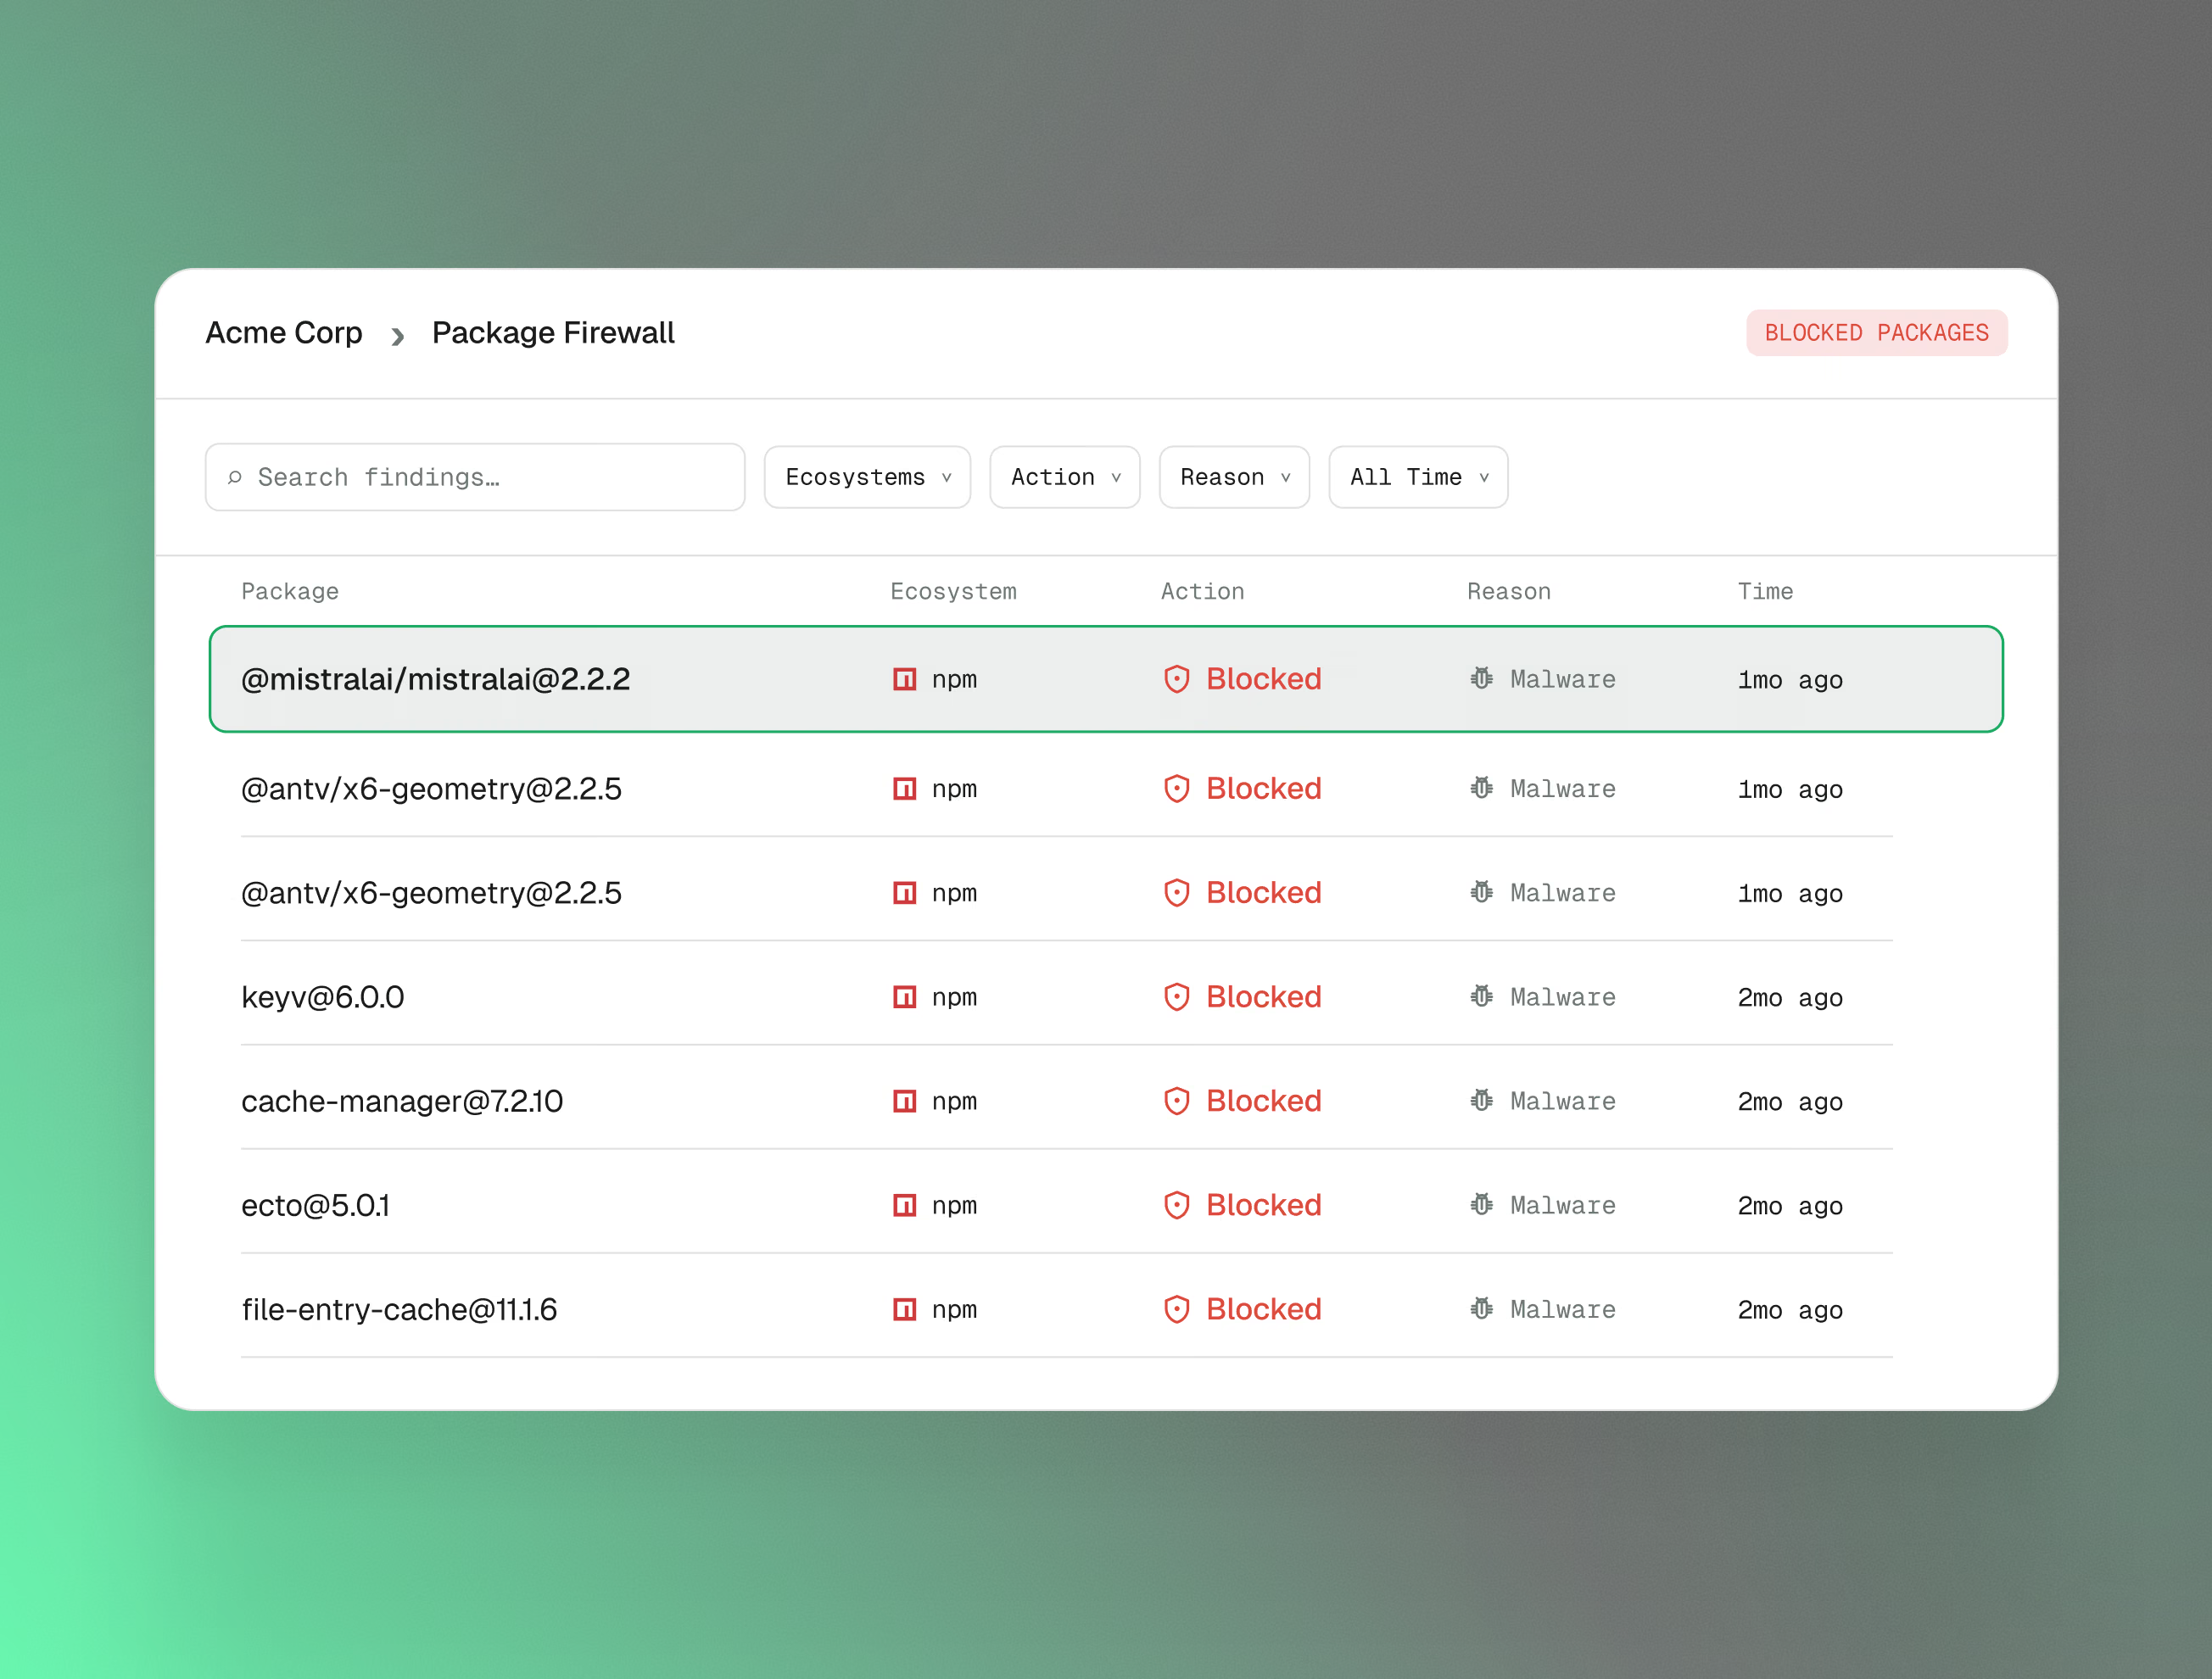
Package Firewall blocks malicious packages before a developer or AI agent ever runs the install.
Block known malicious packages before an AI coding agent or developer runs the install script.
Integrate with Cursor hooks and other IDE-level controls to intercept dependencies at the moment of risk.
Apply the same policy to AI agents and humans, so AI adoption doesn't become a path around your controls.
Learn more
Find it in your code
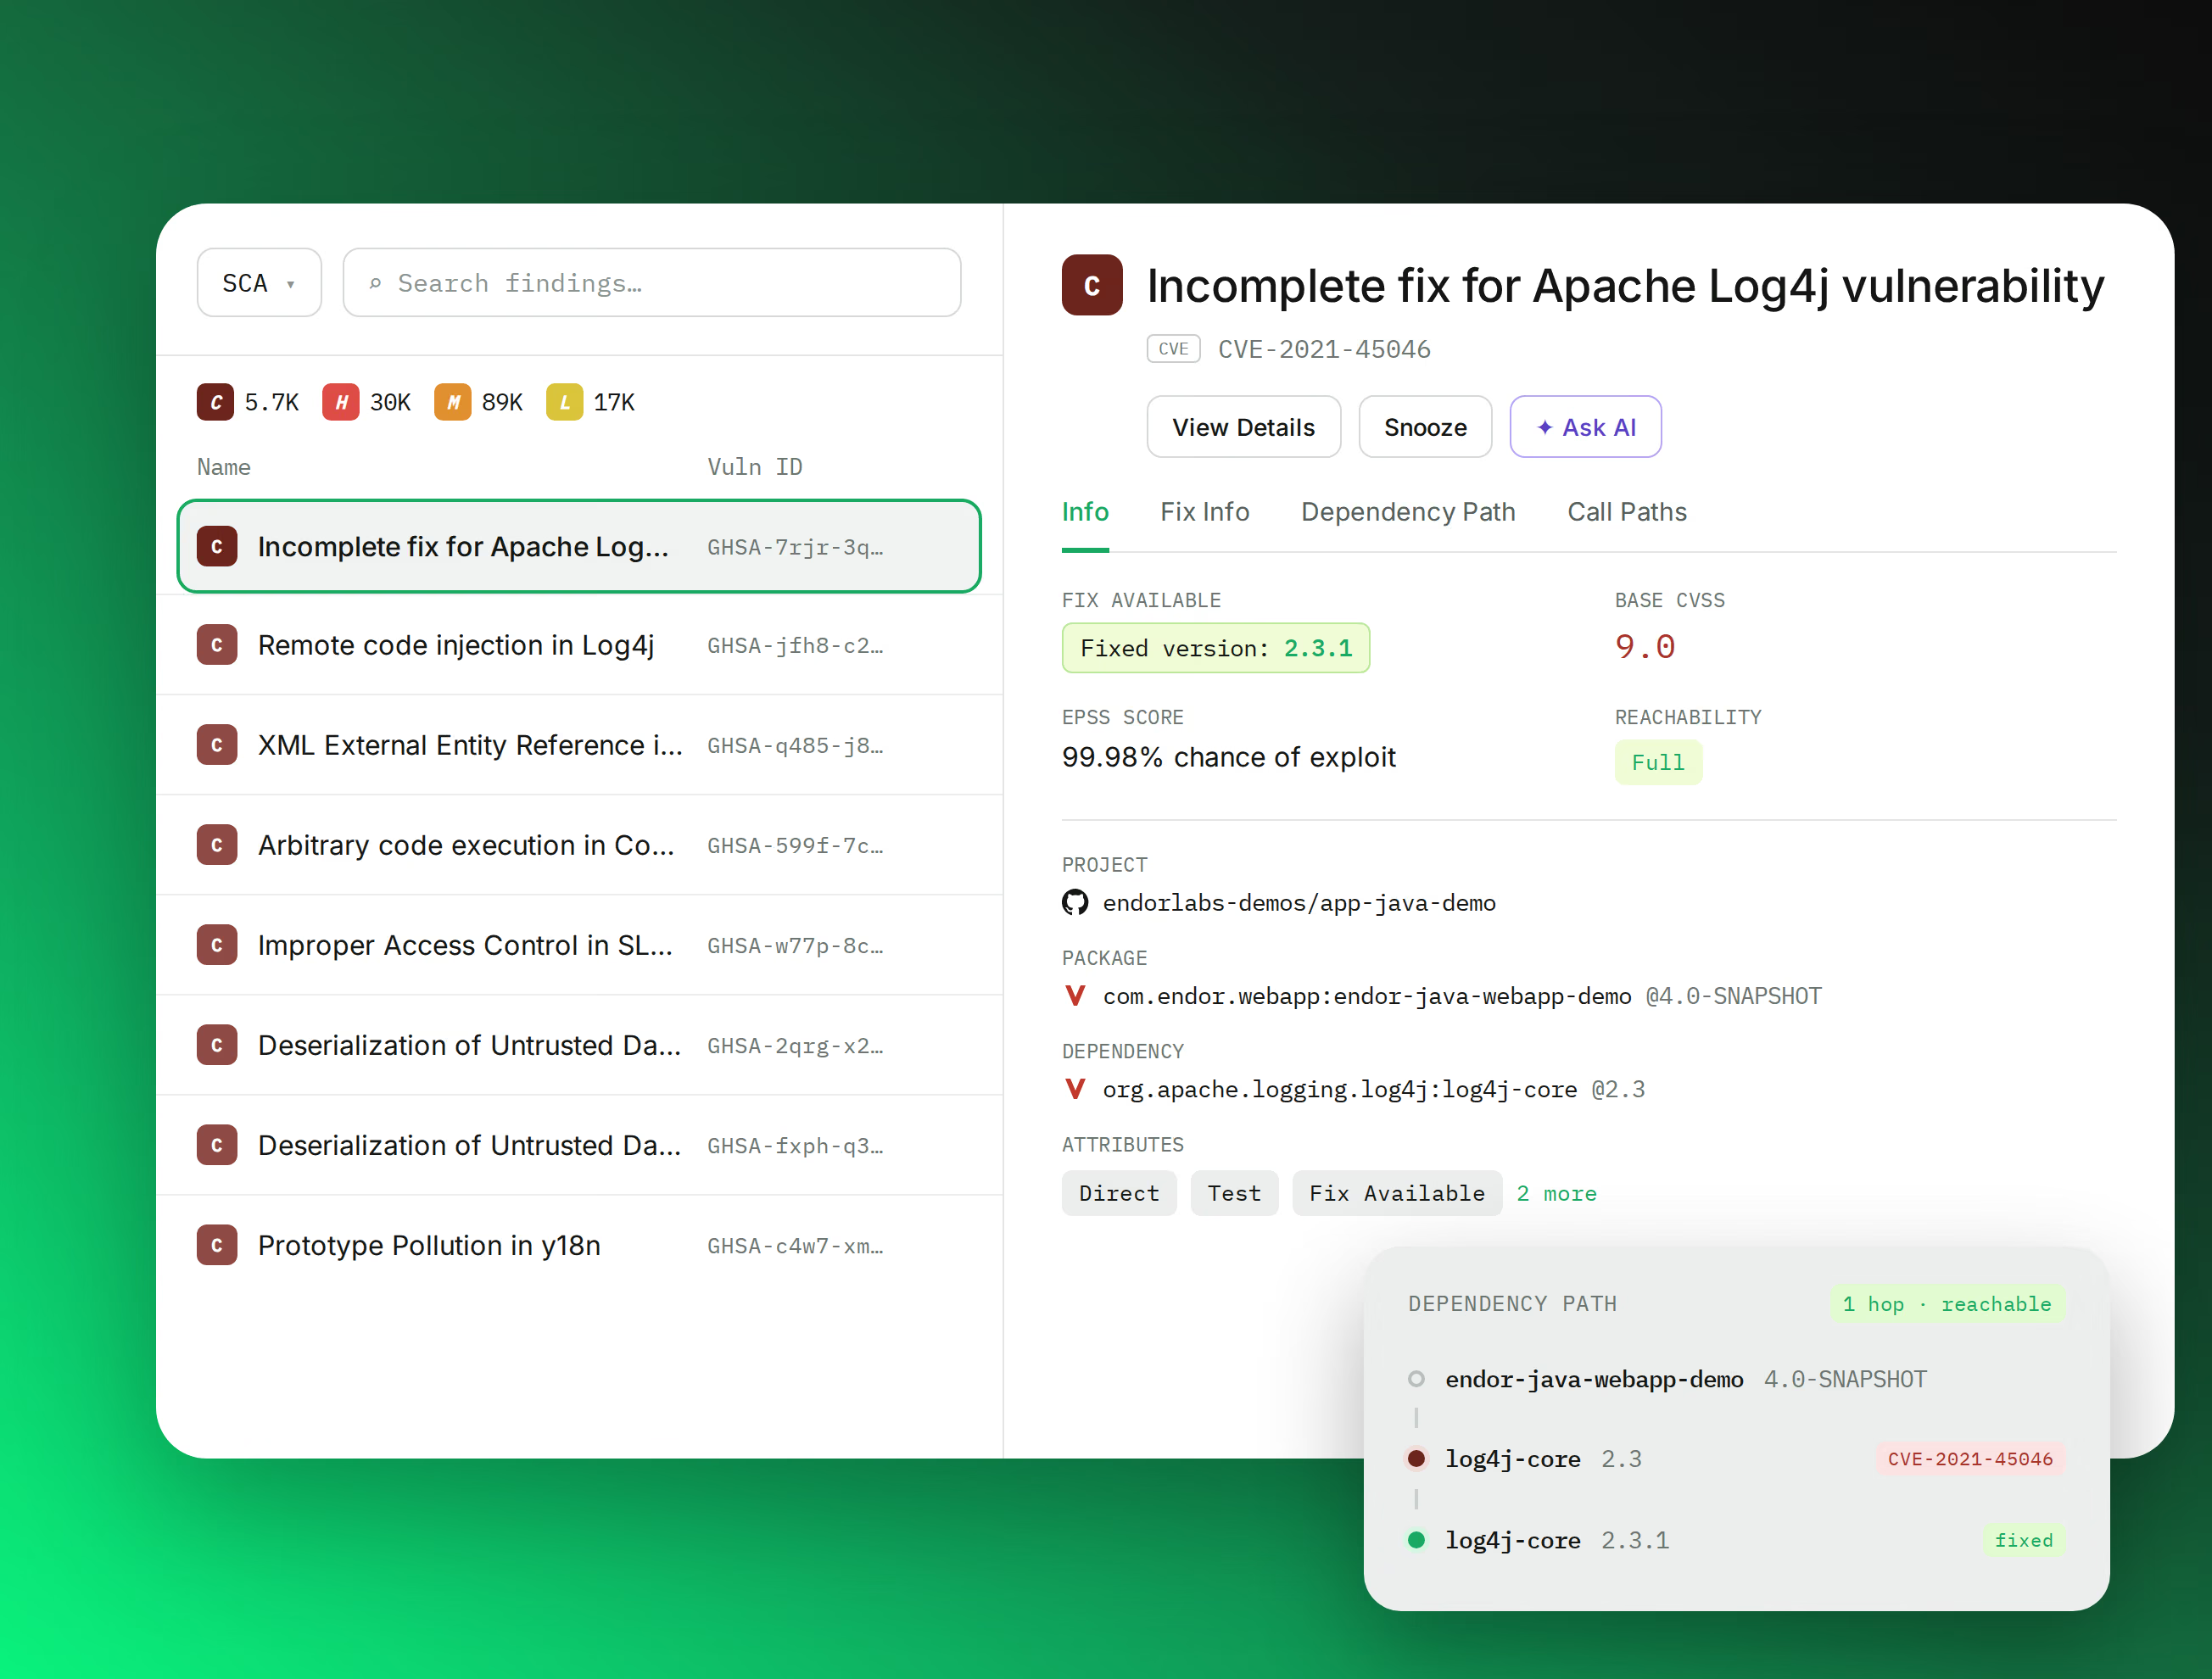
SCA scans the applications you already have, so a new disclosure never means days of hunting through repositories and lockfiles.
Search the package inventory of every project and SBOM for a specific malicious version the moment it's published.
Flag unpinned dependencies that would have resolved to the malicious version on the next install. 
Build a durable malware program with policies for cooldown periods, unpinned dependencies, and unused code.
Learn more

See it in action

Flowchart showing integration paths from GitHub, GitLab, and PHP to Slack and Microsoft platforms, with a C# icon connected to Slack.

Your Tools, Your Languages
— All Secured
Learn how Endor Labs fits into your ecosystem.
Flow diagram connecting software development tools and platforms including .NET, JetBrains, GitHub, Google, and Vercel.

FAQs

How is malware different from a vulnerability?

A vulnerability is a flaw in legitimate code with a CVE and a patch window; malware is malicious from day one, has no CVE, and can execute the moment you run install. That's why advisory-matching scanners miss it and why detection has to happen before install.

Why aren't public malware feeds enough?

Research shows roughly 40% of known malicious packages aren't available through public registries, and registry takedowns lag the attack. Malicious Package Detection covers threats removed from or not yet in public feeds, scanning against 150+ signals.

Does it cover AI coding agents?

Yes. Detection runs in the IDE and integrates with Cursor hooks and other controls to intercept a package before an AI agent or developer runs the install script — applying the same policy to agents and humans.

How do you keep false positives from overwhelming us?

Unclear findings are routed to the Endor Labs security research team for human verification, so alerts represent confirmed threats and engineering trusts them enough to act.

How fast can we tell if we're exposed to a new campaign?

You can confirm or rule out exposure across every application in minutes by searching the package inventory of every project and SBOM for the malicious version, instead of manually hunting through repositories for days.

Where does it run?

In the IDE before an AI agent or developer installs, in CI before a build ships, and across the package inventory of every existing application.

Code without compromise