SCA with Reachability

SCA built for AI-speed development
92% false positive cut with function-level reachability
One scan for every dependency, with SBOM and VEX export
Upfront fixes that cut developer remediation time
SCA with reachability analysis hero graphic
Loved by security teams, painless for developers at:
“Over 97% of vulnerabilities flagged by our previous tool weren't reachable in our application. Endor Labs shows the few impactful vulnerabilities, so we can patch quickly, focusing on what matters.”
Travis McPeak
Travis McPeak

Security Lead, Cursor (Anysphere)

How SCA with Reachability works
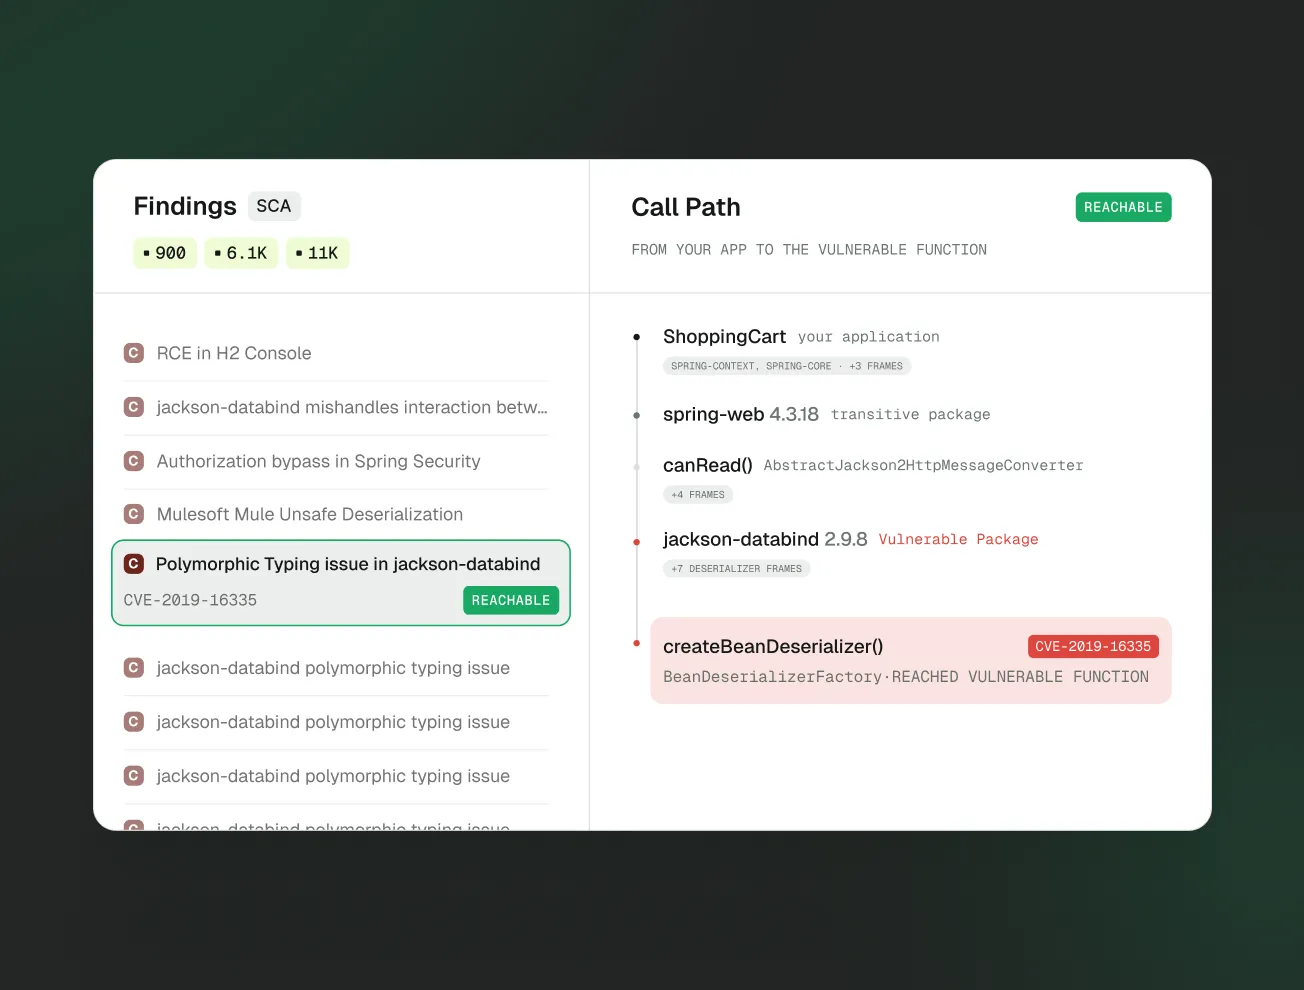
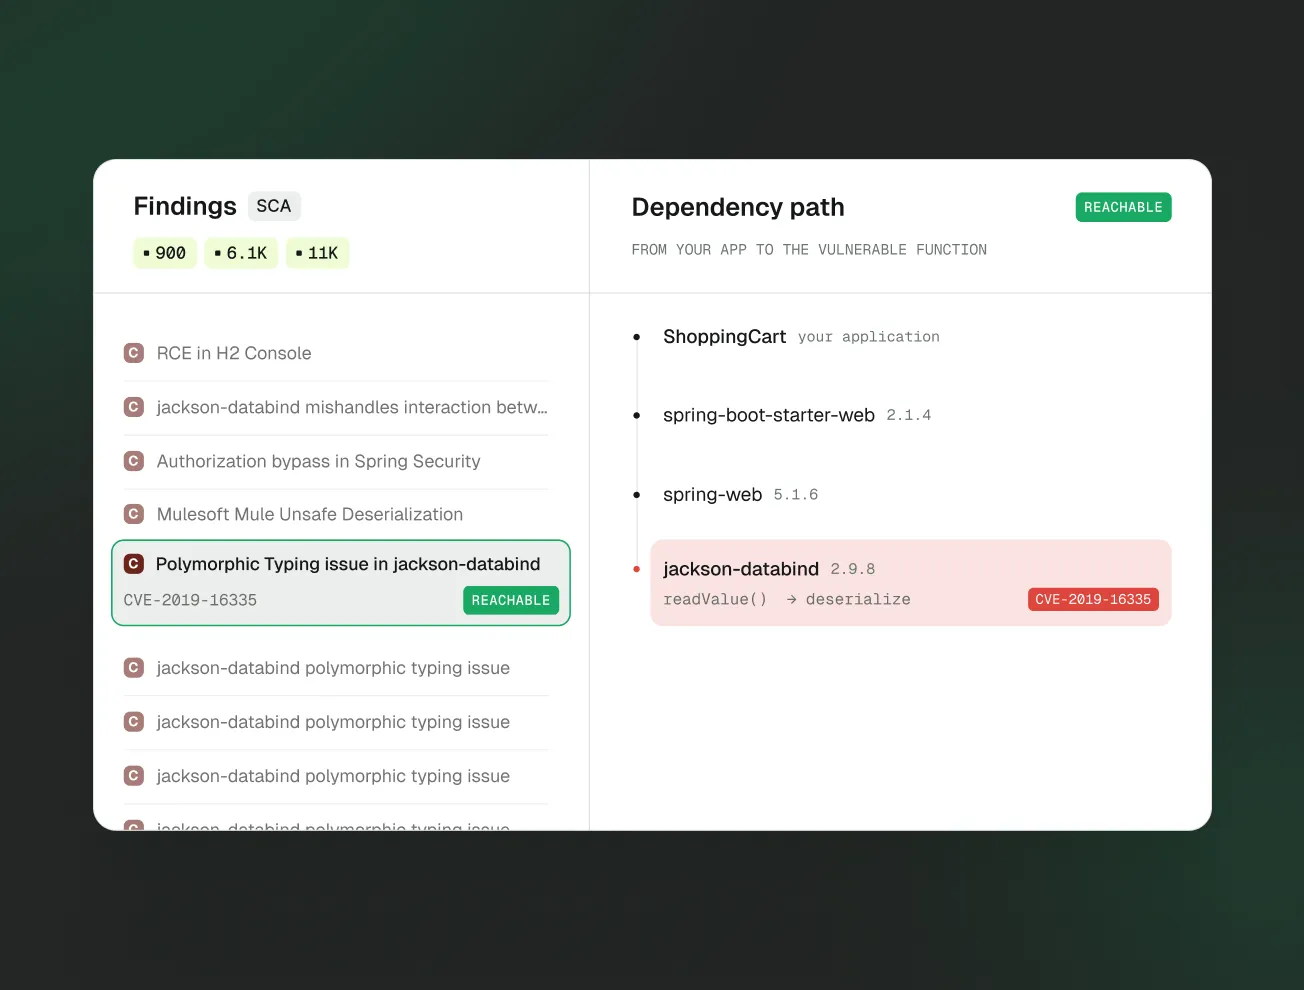
Function-level reachability graphic showing vulnerable function call paths
Function-level reachability
Identify which vulnerabilities are actually callable in your code, down to the function.
Cut SCA findings by 92% by filtering out vulnerabilities that are not actually callable in your code.
Trace exploitability across direct and transitive dependencies down to the specific vulnerable function.
Combine reachability with EPSS, fix availability, and production context to rank what to fix first.
Book a Demo
Complete inventory
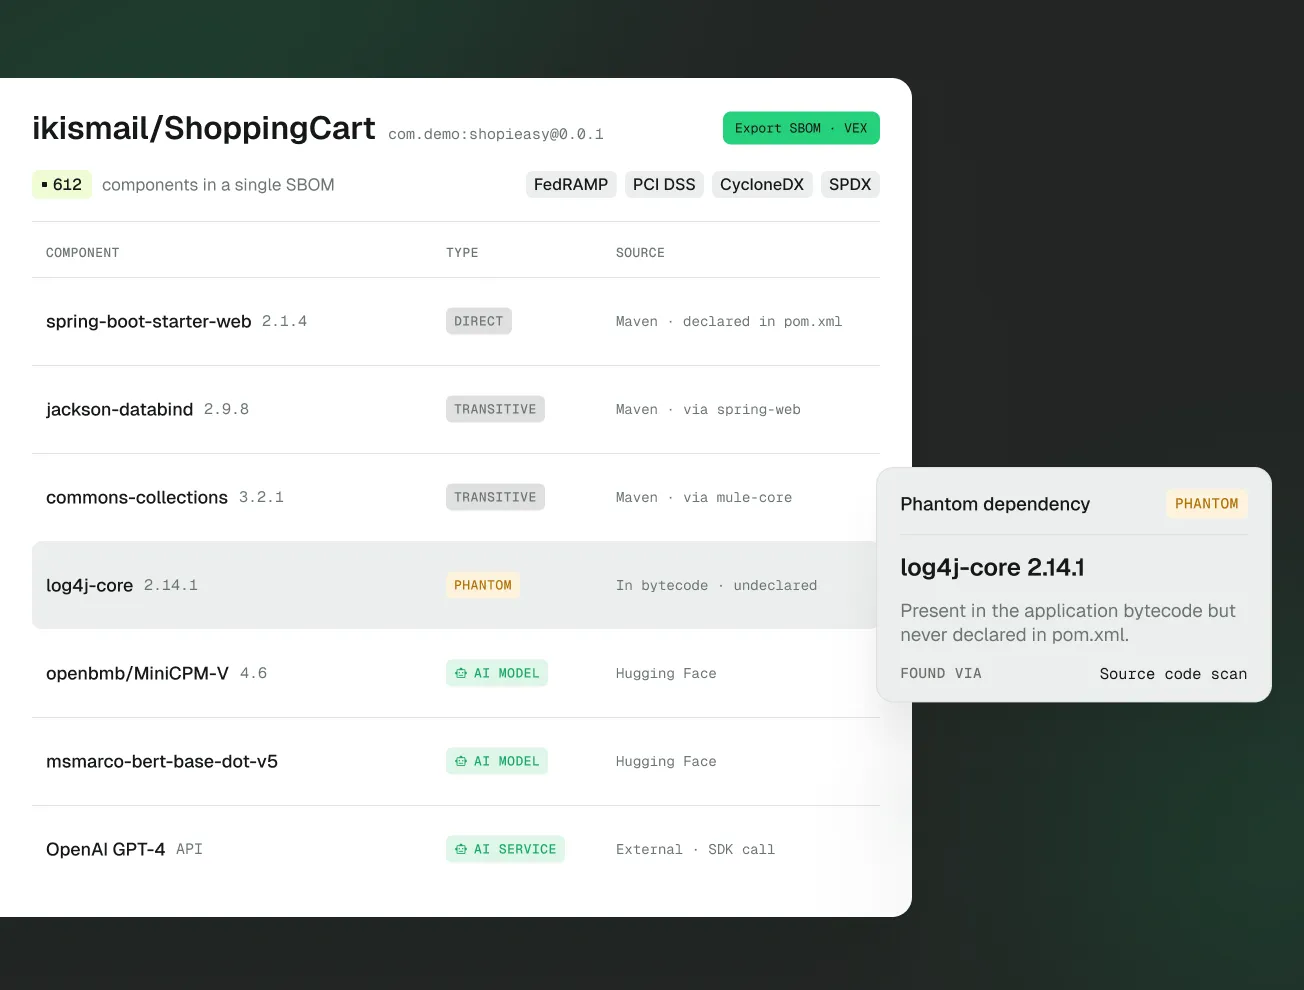
Discover every direct, transitive, and phantom dependency — including AI models — from source code.
Discover every direct, transitive, and phantom dependency by scanning source code, not just manifest files.
Inventory AI models and AI services alongside open source libraries in a single SBOM.
Export SBOM and VEX documents that meet FedRAMP, PCI DSS, and other compliance requirements.
Book a Demo
Complete inventory graphic showing all open source dependencies
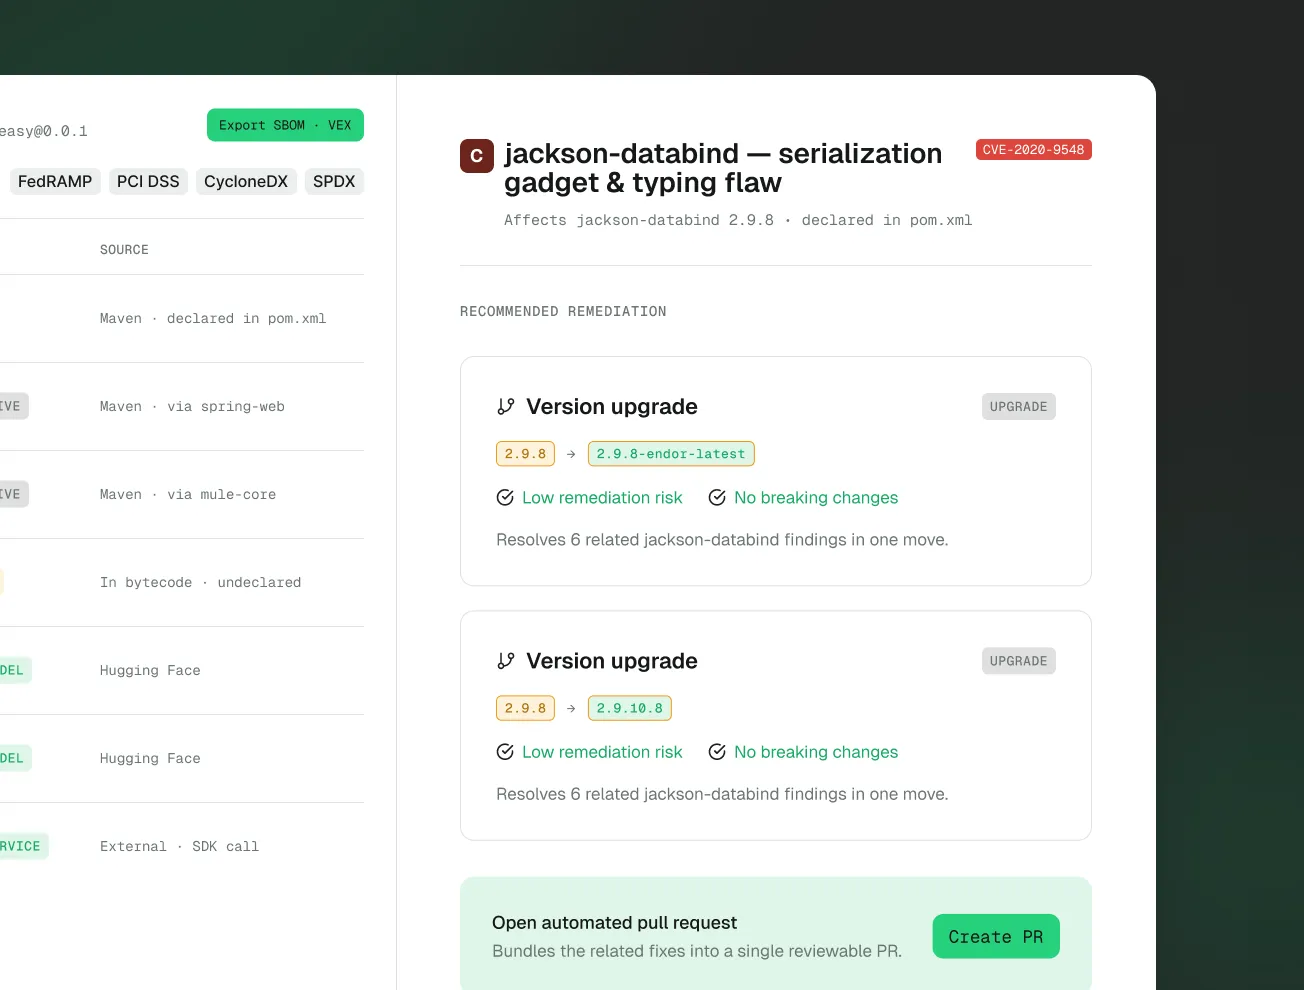
Safe remediation graphic showing upgrade risk analysis
Safe remediation
Guide developers to the upgrades that fix the most risk with the least disruption.
Tell developers which upgrades are safe and which will introduce breaking changes before the work starts.
Resolve more findings per upgrade with automated pull requests that bundle related fixes.
Patch transitive dependencies at build time when an upgrade is not practical.
Book a Demo
Interactive demo

See function-level reachability in a few clicks
In this guided demo, you'll see how Endor Labs groups SCA findings, ranks them by severity and reachability, and shows the call path and fix context for each one.

FAQs

What does 'reachability' actually mean?

Instead of asking whether a vulnerable library is present, reachability asks whether the vulnerable function is actually callable in your application. Endor Labs analyzes this at the function level across direct and transitive dependencies.

How much noise does it remove?

Function-level reachability cuts SCA findings by 92% by filtering out vulnerabilities that aren't callable in your code, so developers focus on what's exploitable.

What does it find that manifest-based SCA misses?

It scans source code as ground truth to catch transitive dependencies, phantom dependencies, and AI models and services that manifest-based tools miss entirely.

How does it help with remediation?

It tells developers which upgrades are safe and which introduce breaking changes before the work starts, bundles related fixes into automated pull requests, and can patch transitive dependencies at build time when an upgrade isn't practical.

Can it support our compliance needs?

Yes. It builds a complete inventory including AI models and exports SBOM and VEX documents that meet FedRAMP, PCI DSS, and other requirements.

How does it prioritize what to fix first?

It combines reachability with EPSS, fix availability, and production context, and draws on proprietary CVE annotations going back to 2018 to rank the findings that matter most.

Code without compromise.