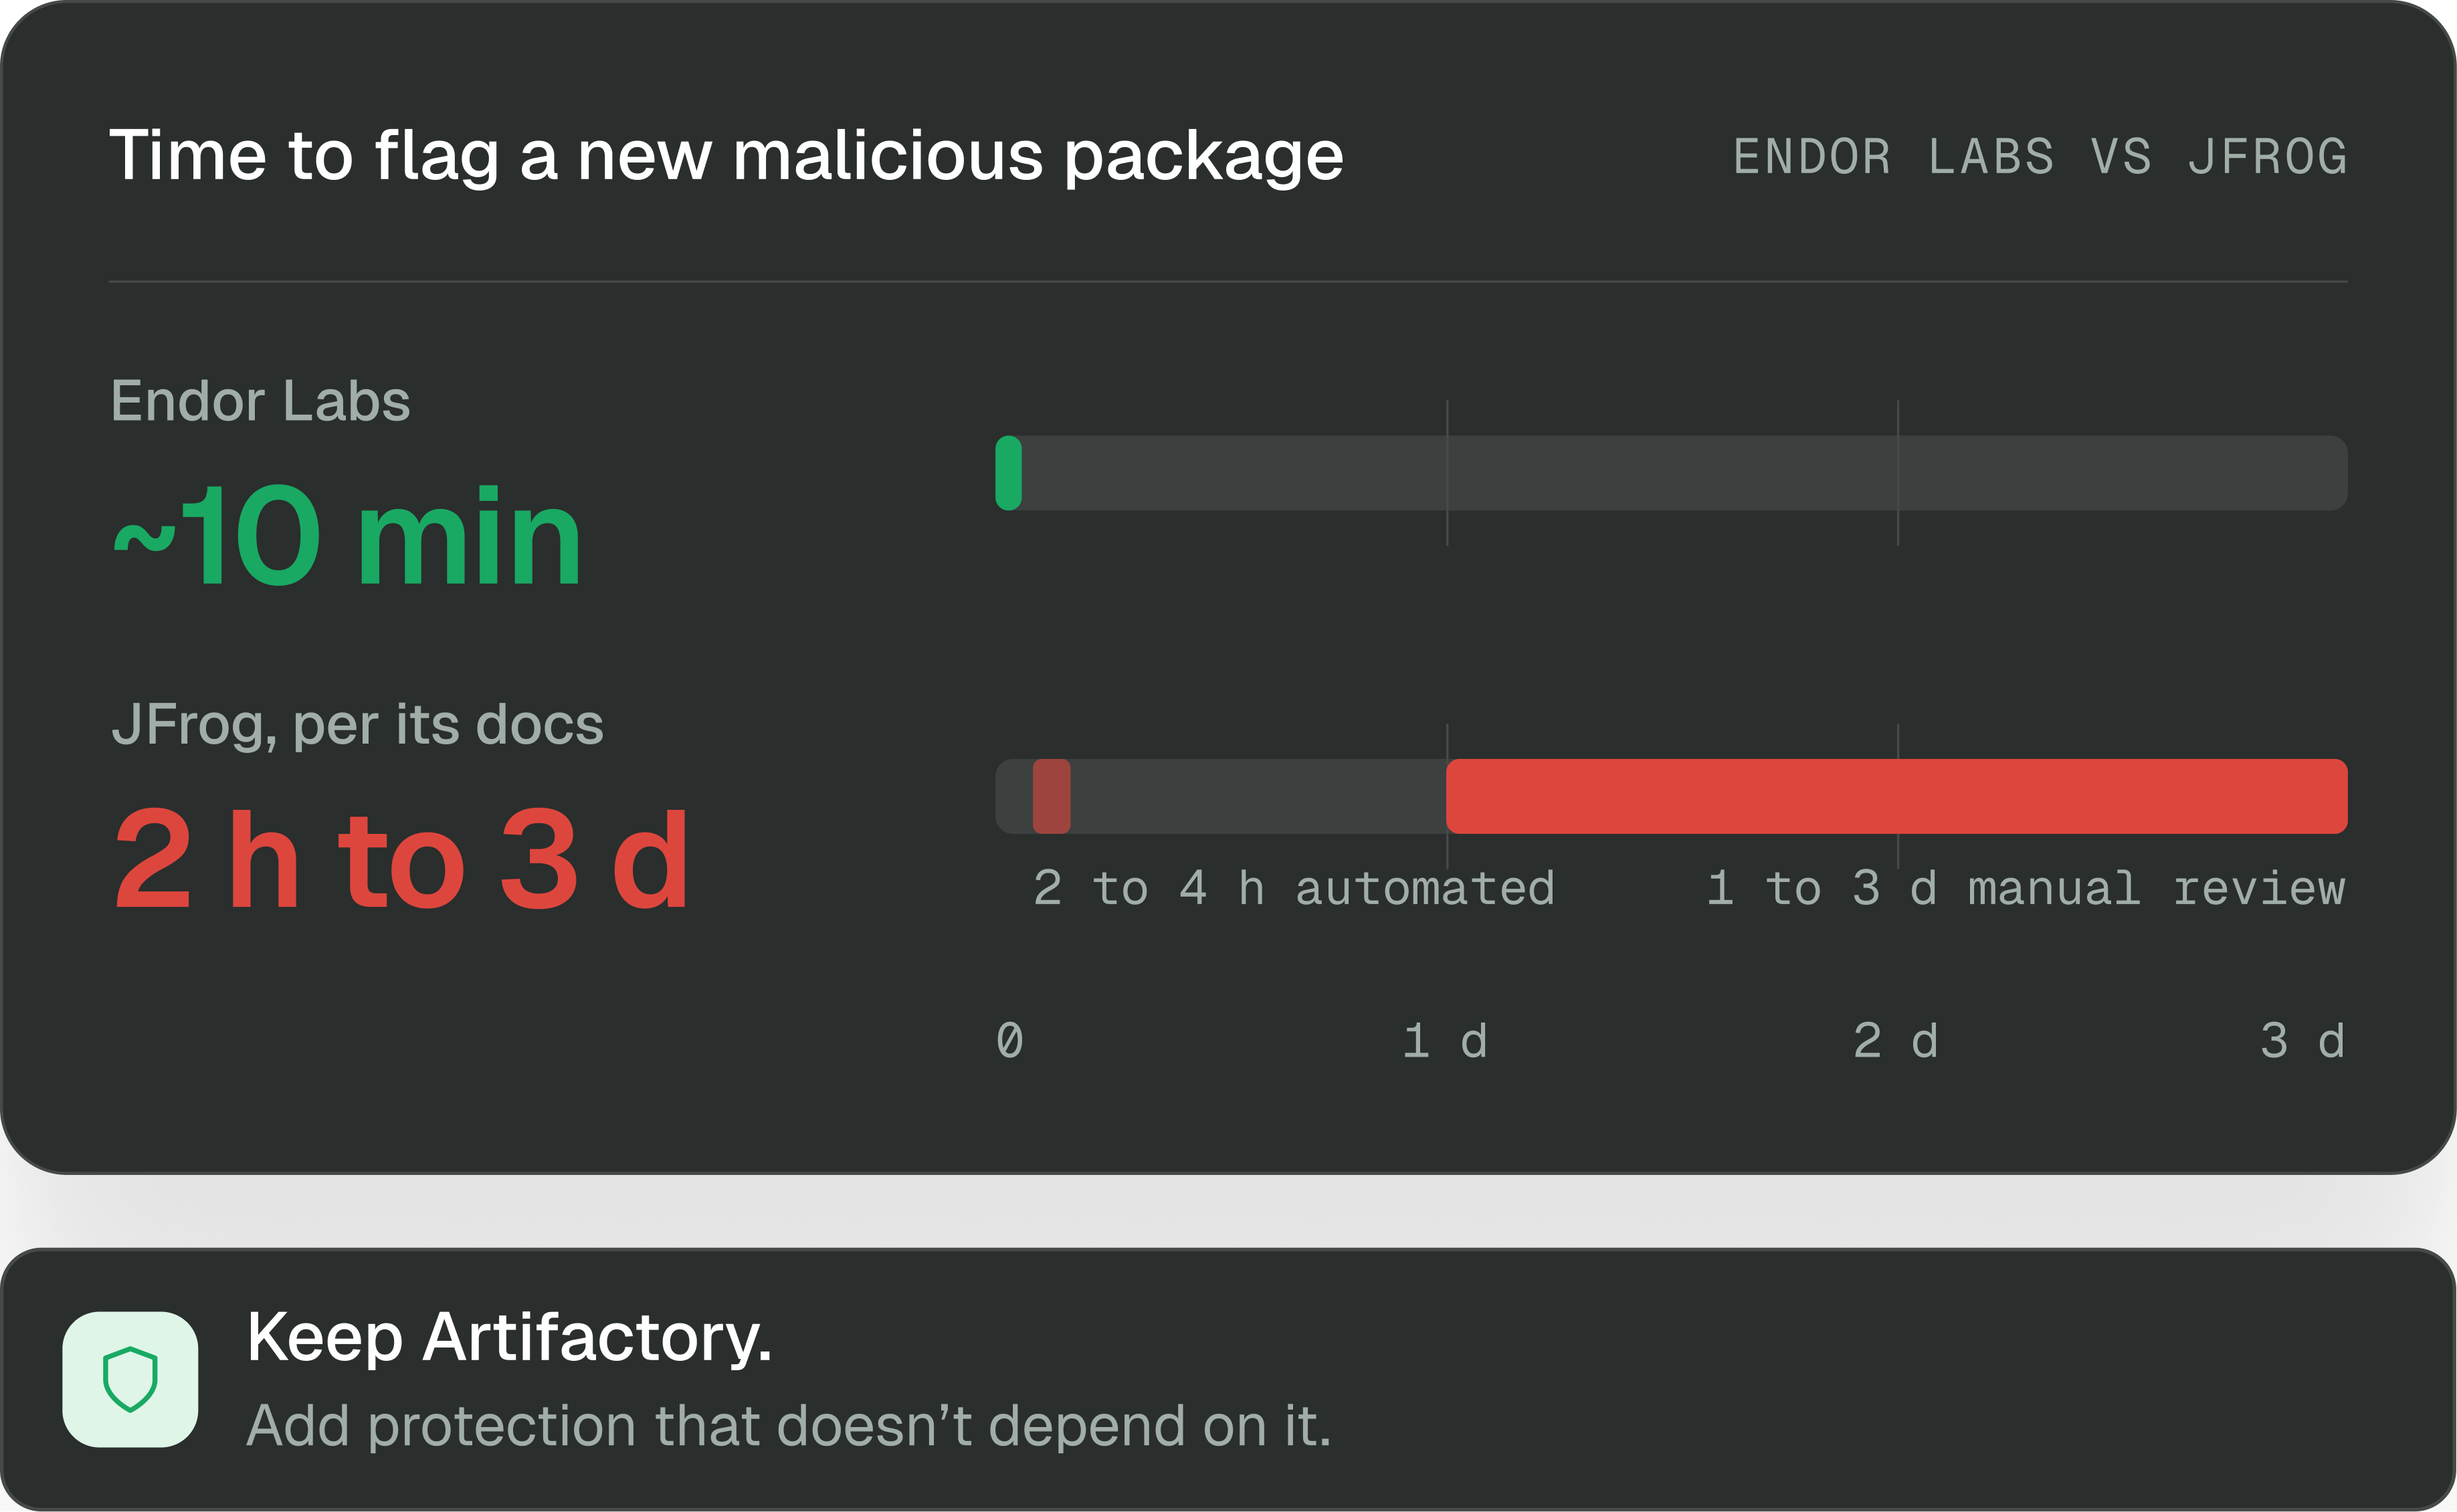
JFrog customers: catch malware faster, for one flat price.




Why customers choose Endor Labs over JFrog
How Endor Labs compares to JFrog
What security teams say




FAQs
No. Endor Labs does not make an artifact repository. Package Firewall is complementary to Artifactory: it integrates with Artifactory and can also be set up in supported package clients and on developer and CI machines, so you are not locked into Artifactory as the only place protection runs. You keep your repository, caches, and workflows.
Three places you can combine: with your artifact repository (JFrog Artifactory, Sonatype Nexus, and Google Artifact Registry today, with more repositories being added); in supported package clients with no repository needed; and on developer and CI machines through MDM or CI configuration, including machines running AI coding agents.
JFrog is deprecating Xray's Block Download for remote repositories, in phases through November 2026. After that, blocking for remote repositories is only available in Curation. Xray scanning continues, and Xray still blocks on local repositories. If you relied on remote-repository blocking, this is a good time to compare Curation with Package Firewall for the same job.
Both aim to cut noise. The difference is coverage. JFrog Contextual Analysis has scanners for about 1,600 CVEs, mostly critical and high, and a CVE without a scanner gets no answer. Endor Labs has function-level reachability for 20,000+ CVEs at every severity, computed from your code's call graph across direct and transitive dependencies, with the call path on each finding. Run both on your codebase and count how many findings come back with an answer.
Package Firewall is a standalone product priced per developer, with no artifact repository required and no consumption charges. For an existing Artifactory customer, the useful comparison is the SKUs you would add on the JFrog side versus adding Package Firewall. SCA, patches, and other Endor Labs products are priced separately.