Blog

Learn about software supply chain security and Endor Labs
Endor Labs Named in the 2026 Gartner® Hype Cycle™ for Secure Software Engineering

Endor Labs Named in the 2026 Gartner® Hype Cycle™ for Secure Software Engineering

Endor Labs Named in the 2026 Gartner® Hype Cycle™ for Secure Software Engineering

Claude Sonnet 5 with Claude Code: strong on function, average on security, and unusually honest

Claude Sonnet 5 with Claude Code: strong on function, average on security, and unusually honest

Claude Sonnet 5 with Claude Code: strong on function, average on security, and unusually honest

Endor Labs’ AI SAST Finds Zero Day Memory-Amplification DoS in Anthropic’s buffa library

Endor Labs’ AI SAST Finds Zero Day Memory-Amplification DoS in Anthropic’s buffa library

Endor Labs’ AI SAST Finds CVE-2026-55407: Memory-Amplification DoS in buffa

Benchmarking Endor Labs AI SAST: 2.6x more real vulnerabilities found than frontier models

Benchmarking Endor Labs AI SAST: 2.6x more real vulnerabilities found than frontier models

AI SAST found 192 real vulnerabilities, 2.6x more than Claude Code

Shai-Hulud Strikes Leo Platform npm

Shai-Hulud Strikes Leo Platform npm

Open source carries the world. Patching it at Mythos-scale can't fall to maintainers alone.

Open source carries the world. Patching it at Mythos-scale can't fall to maintainers alone.

Endor Labs is a Visionary in the 2026 Gartner® Magic Quadrant™ for Software Supply Chain Security

Endor Labs is a Visionary in the 2026 Gartner® Magic Quadrant™ for Software Supply Chain Security

Endor Labs is a Visionary in the 2026 Gartner® Magic Quadrant™ for Software Supply Chain Security

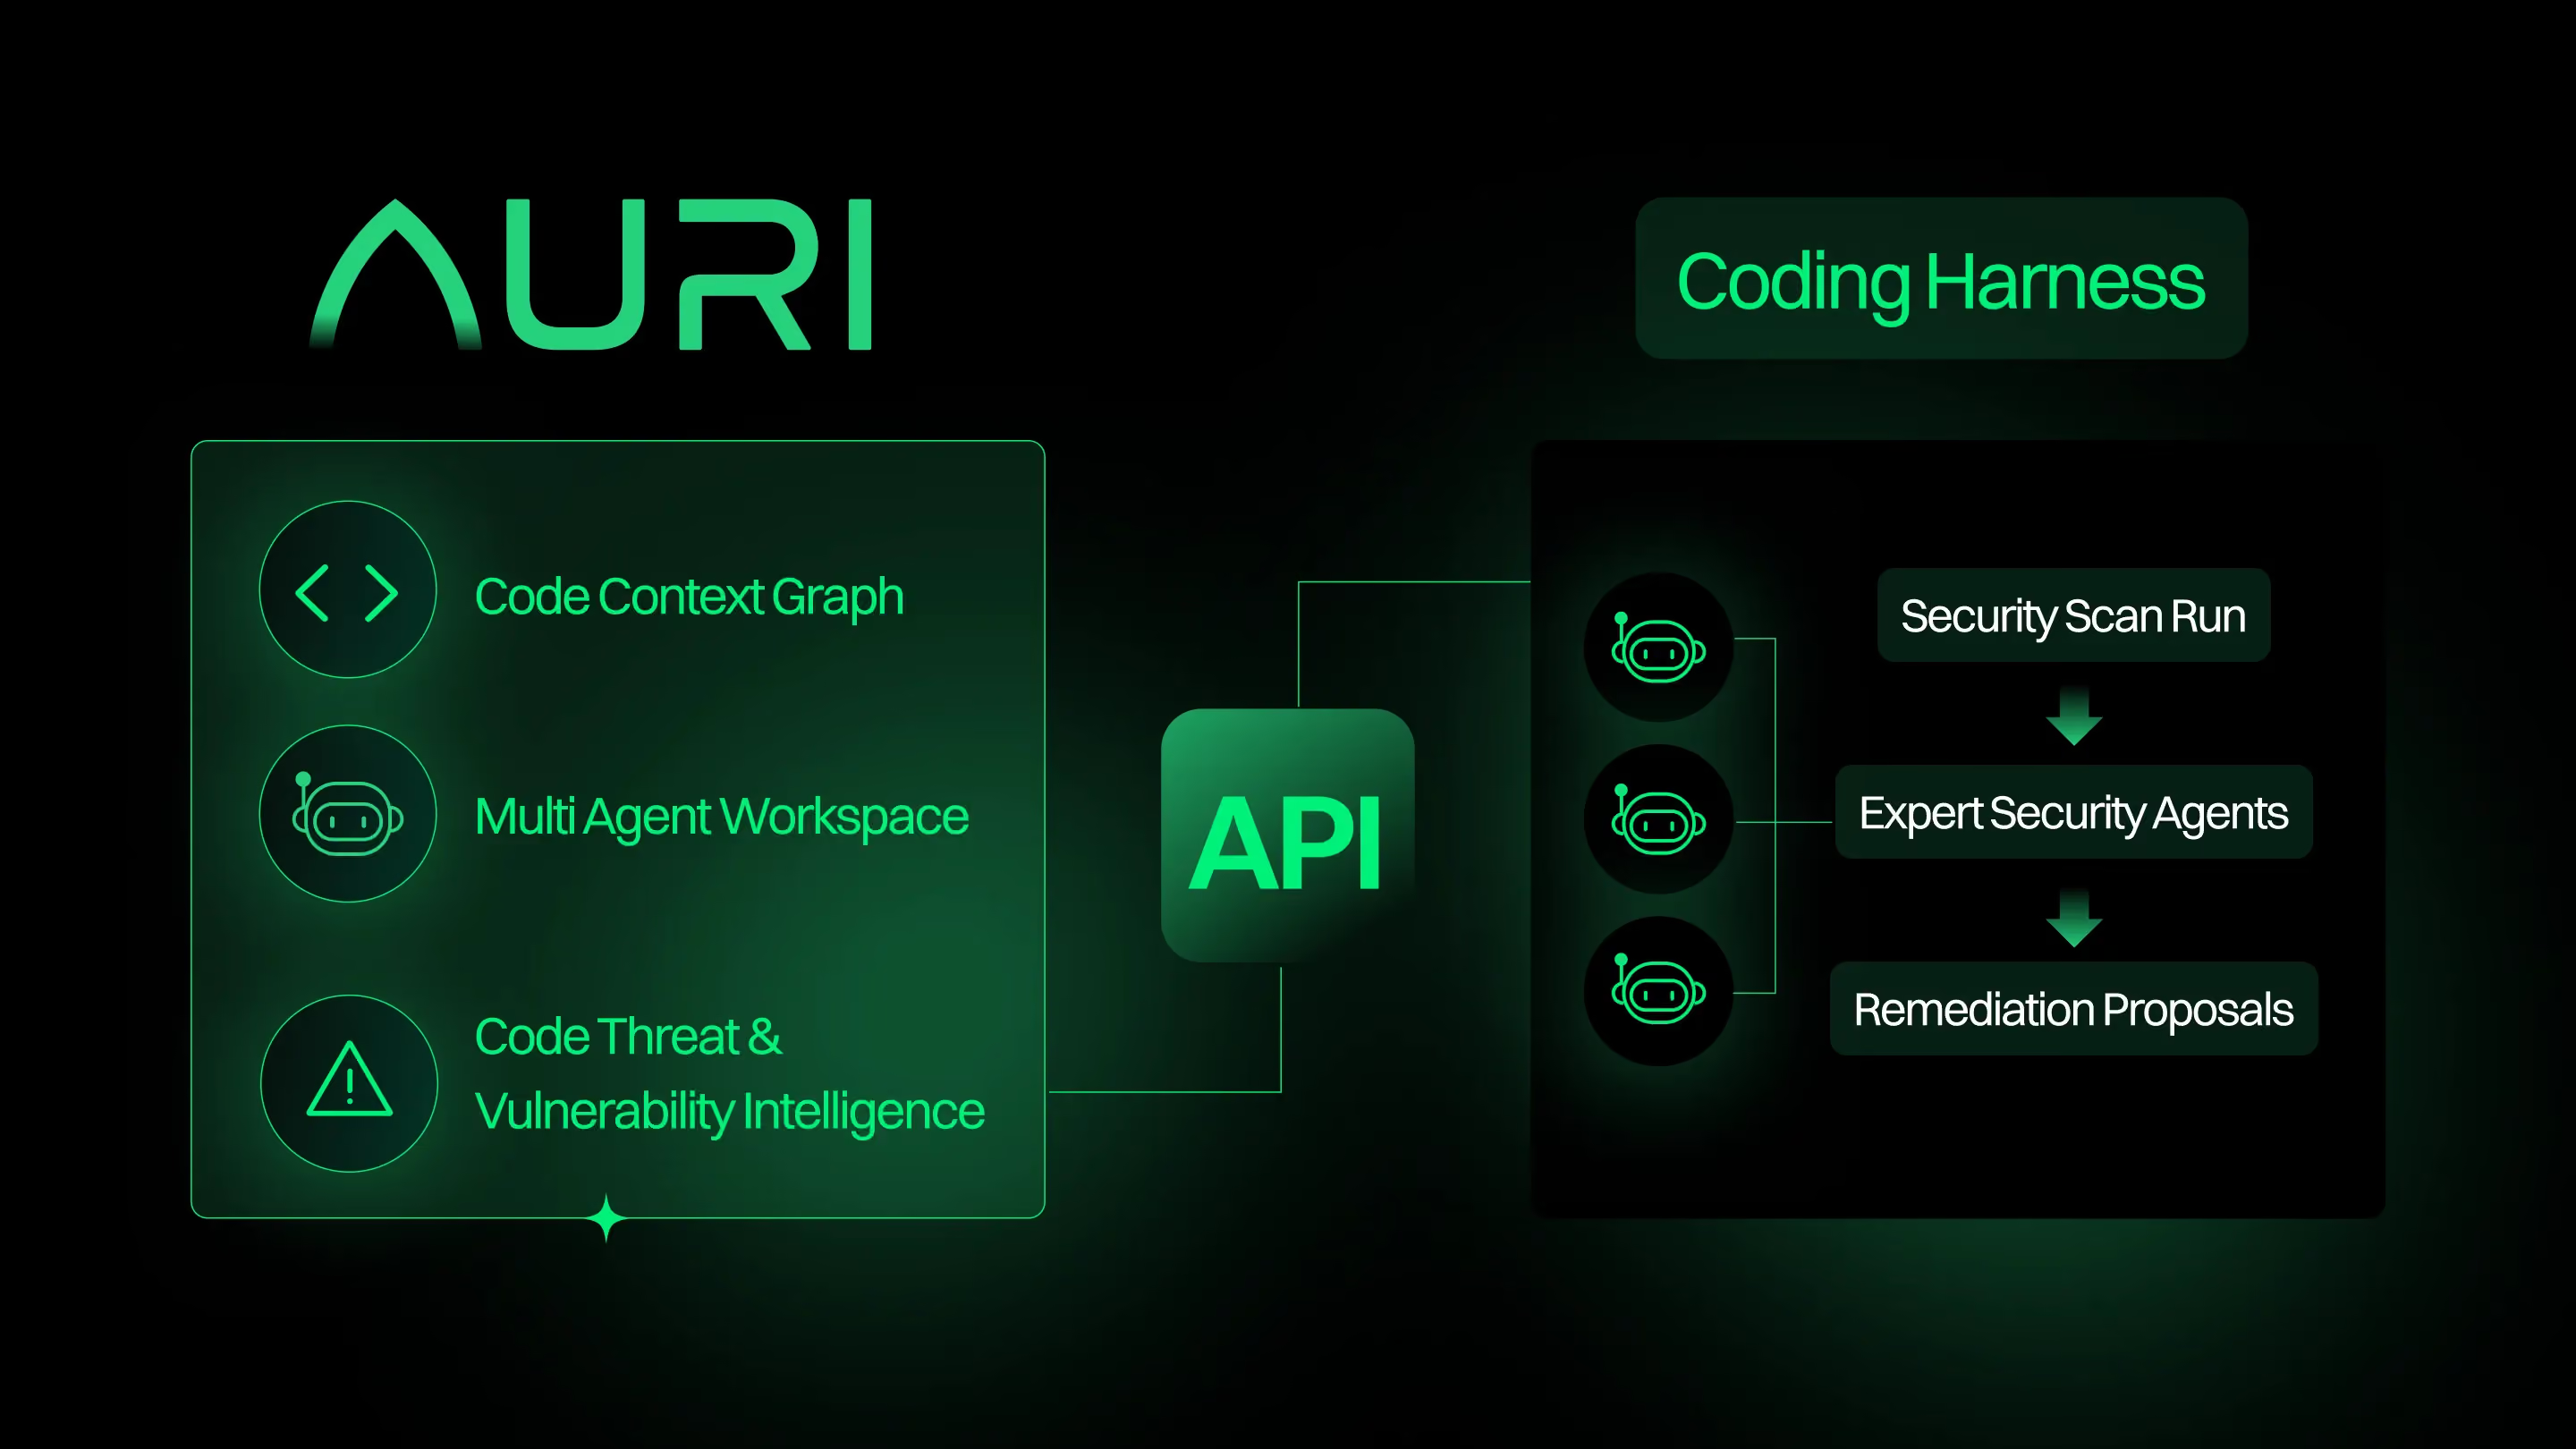
Claude Fable 5, take two: same model, different harness, and a very different result

Claude Fable 5, take two: same model, different harness, and a very different result

Claude Fable 5, take two: same model, different harness, and a very different result

AppSec was built to find problems. The Mythos era demands you fix them, fast.

AppSec was built to find problems. The Mythos era demands you fix them, fast.

AppSec was built to find problems. The Mythos era demands you fix them, fast.

Mastra npm Org Compromised: Multiple Packages Trojanized to Drop a Remote Payload via easy-day-js

Mastra npm Org Compromised: Multiple Packages Trojanized to Drop a Remote Payload via easy-day-js

A single hijacked maintainer account pushed multiple trojanized packages across the entire @mastra scope in 27 minutes, each carrying a typosquat dependency that runs a remote payload on install. Combined reach is over 28 million downloads a month.
Build vs. Buy Code Security: Same Model, Same Tasks, 12x the Token Bill

Build vs. Buy Code Security: Same Model, Same Tasks, 12x the Token Bill

The token economics of using AI coding agents for security tasks

Claude Fable 5: Mythos-grade hype, record cheating, and a few hall-of-fame entries

Claude Fable 5: Mythos-grade hype, record cheating, and a few hall-of-fame entries

Average results with 59.8% on functional solves and just 19.0% on security solves

Recall, not reasoning: how AI coding agents cheat security benchmarks

Recall, not reasoning: how AI coding agents cheat security benchmarks

Recall, not reasoning: how AI coding agents cheat security benchmarks

Endor Labs Named a Representative Vendor in the 2026 Gartner® Innovation Insight for Agentic Application Security Testing

Endor Labs Named a Representative Vendor in the 2026 Gartner® Innovation Insight for Agentic Application Security Testing

Endor Labs Named a Representative Vendor in the 2026 Gartner® Innovation Insight for Agentic Application Security Testing

Shai-Hulud "Hades" Wave Hits Six PyPI Bioinformatics Packages via Stolen Tokens

Shai-Hulud "Hades" Wave Hits Six PyPI Bioinformatics Packages via Stolen Tokens

Shai-Hulud "Hades" Wave Hits Six PyPI Bioinformatics Packages

Trojanized ai-sdk-ollama Delivers Miasma, a Self-Replicating npm Worm via binding.gyp

Trojanized ai-sdk-ollama Delivers Miasma, a Self-Replicating npm Worm via binding.gyp

Malicious Payload in ai-sdk-ollama npm Package

Endor Labs Recognized in the Forrester Agentic Development Security Tools Landscape

Endor Labs Recognized in the Forrester Agentic Development Security Tools Landscape

Endor Labs Recognized in the Forrester Agentic Development Security Tools Landscape

Endor Labs + Cursor: Building the security foundation for agentic coding

Endor Labs + Cursor: Building the security foundation for agentic coding

Endor Labs + Cursor: Building the security foundation for agentic coding

Designing Reports for Three Different Workflows

Designing Reports for Three Different Workflows

Designing Reports for Three Different Workflows

Endor Labs Recognized by Gartner® in the 2026 Hype Cycle™ for Platform Engineering

Endor Labs Recognized by Gartner® in the 2026 Hype Cycle™ for Platform Engineering

Endor Labs named a Representative Vendor for Software Supply Chain Security.

Trojanized Microsoft SDK: durabletask 1.4.1 through 1.4.3 Deliver Credential-Stealing Malware

Trojanized Microsoft SDK: durabletask 1.4.1 through 1.4.3 Deliver Credential-Stealing Malware

Malicious PyPI package durabletask 1.4.1-1.4.3 steals AWS, Azure, and GCP credentials on import. 417k monthly downloads affected.

Endor Labs and Chainguard Partner to Deliver End-to-End Software Supply Chain Security

Endor Labs and Chainguard Partner to Deliver End-to-End Software Supply Chain Security

Endor Labs and Chainguard Partner to Deliver End-to-End Software Supply Chain Security

Mini Shai-Hulud Returns: 600+Malicious npm Packages Fake Sigstore Badges in AntV Ecosystem Attack

Mini Shai-Hulud Returns: 600+Malicious npm Packages Fake Sigstore Badges in AntV Ecosystem Attack

Mini Shai-Hulud Returns: 42 Malicious npm Packages Fake Sigstore Badges in AntV Ecosystem Attack

Designing AI Coding Agent Governance: A New Surface for AI Risk

Designing AI Coding Agent Governance: A New Surface for AI Risk

Designing AI Coding Agent Governance: A New Surface for AI Risk

When the Guardrails Slip: The Case for Hook-Based Governance Across Agent Platforms

When the Guardrails Slip: The Case for Hook-Based Governance Across Agent Platforms

When the Guardrails Slip: The Case for Hook-Based Governance Across Agent Platforms

Book a Demo

Protect your open source dependencies, secrets, and CI/CD pipelines without slowing down devs.