Secure the pipeline without slowing it down




How CI/CD Security works
Your Tools, Your Languages
— All Secured
See it in action
Related Resources
FAQs
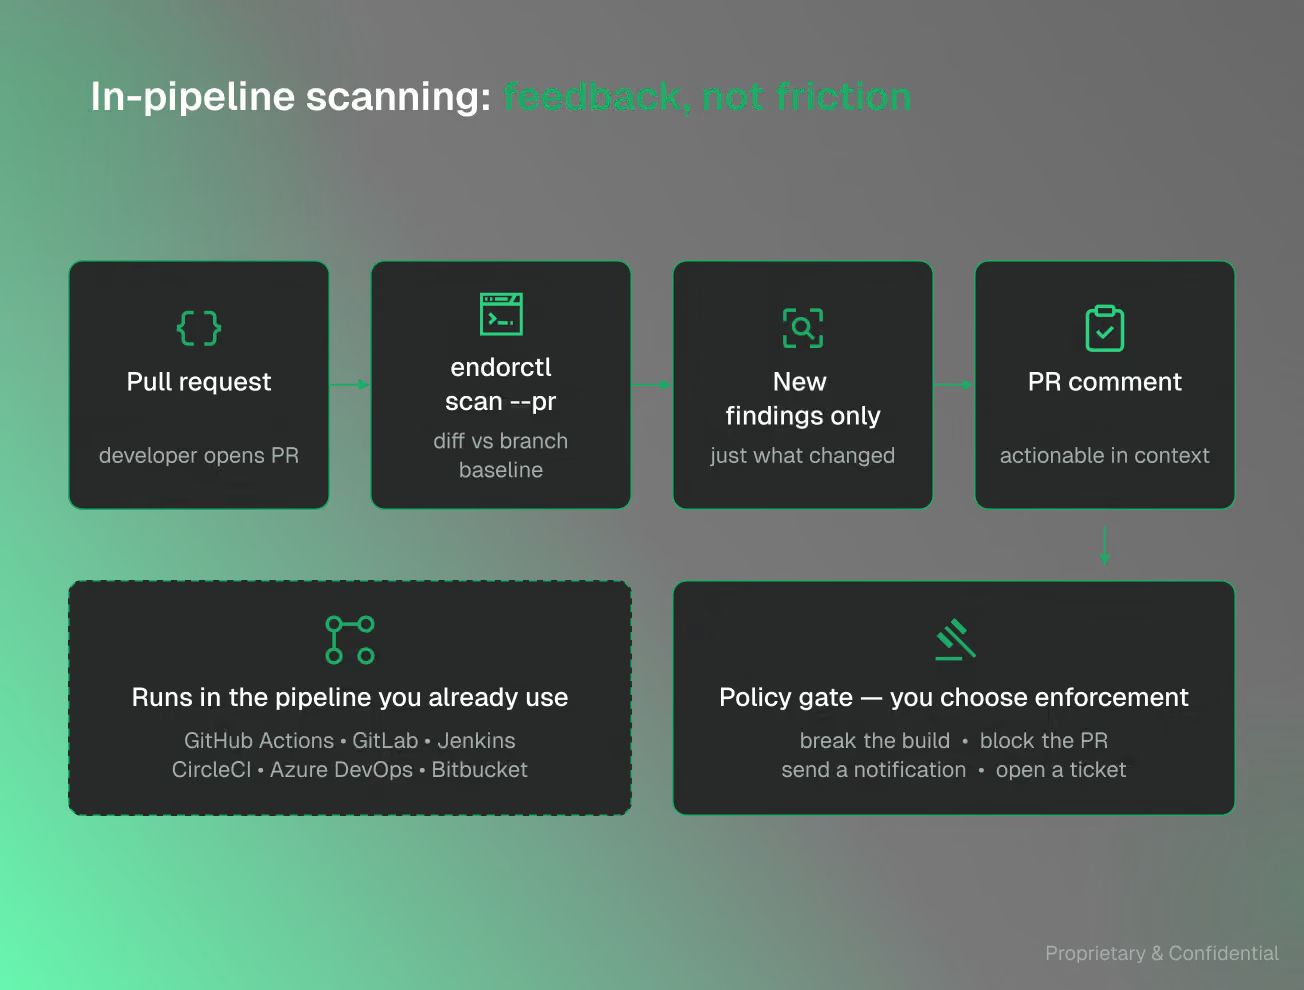
Scans run through the endorctl CLI or native integrations for GitHub Actions, GitLab, Jenkins, CircleCI, Azure DevOps, Bitbucket, Google Cloud Build, and Buildkite. Keyless authentication is the recommended path, so there are no long-lived secrets to rotate.
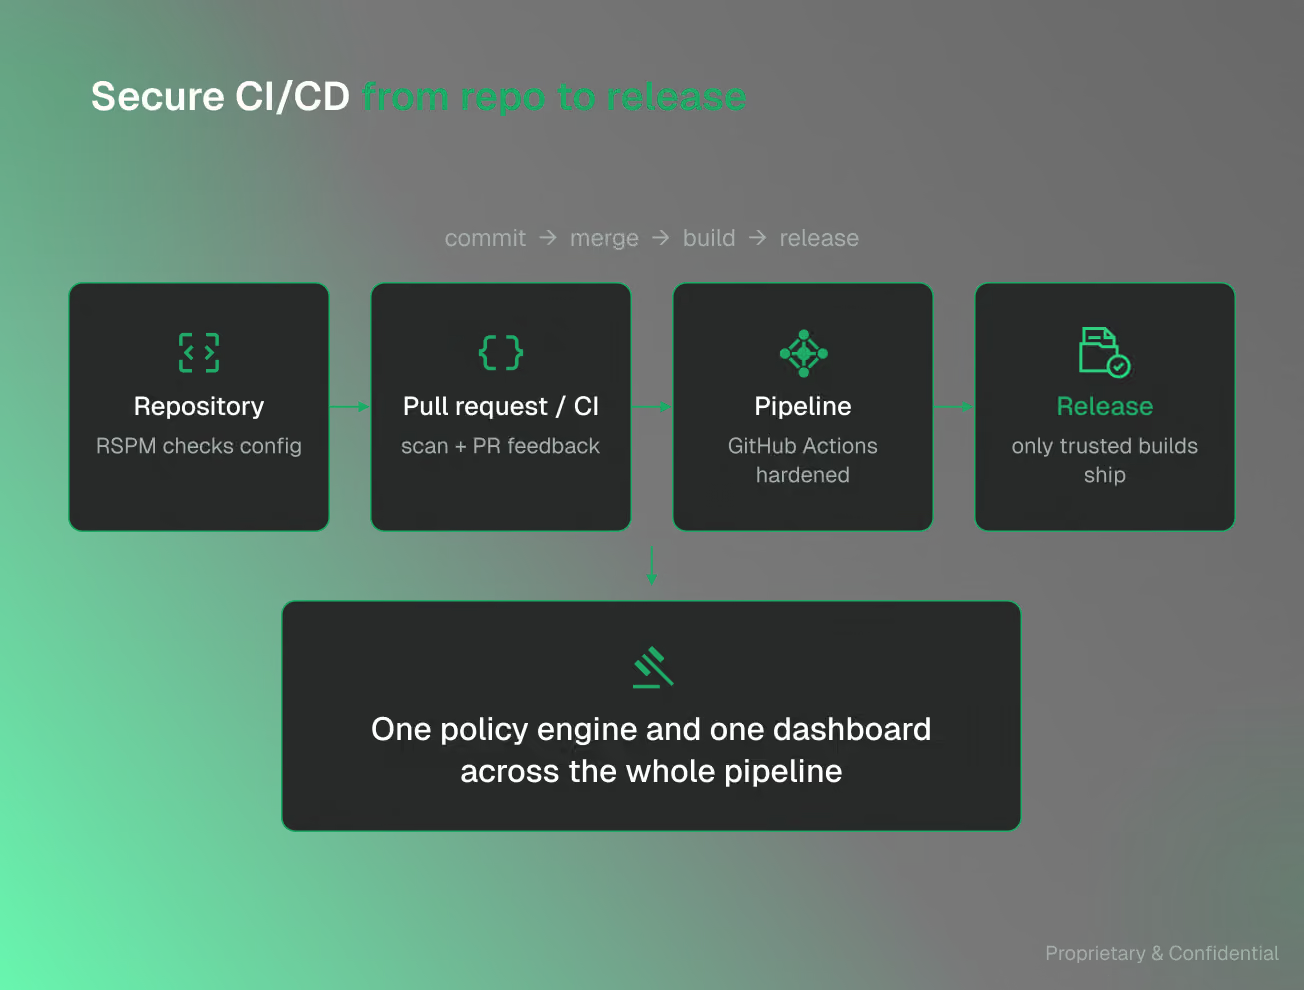
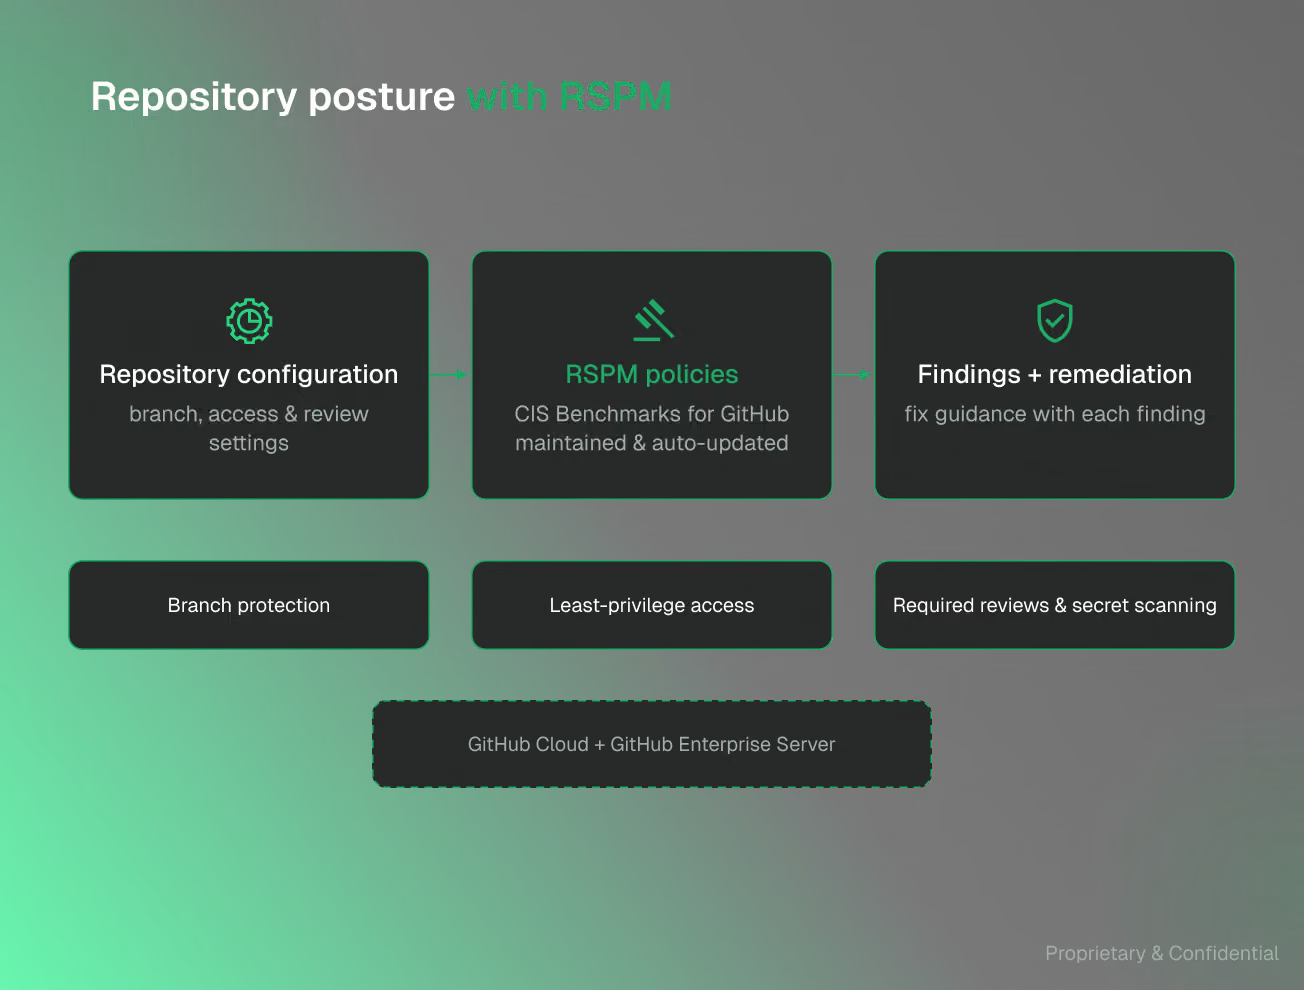
Repository Security Posture Management checks the configuration of your source-control repositories against maintained policies, including CIS Benchmarks for GitHub, and returns remediation guidance so you can fix issues before projects start. It currently supports GitHub Cloud and GitHub Enterprise Server.
CI scans compare against a branch baseline and report only new, actionable findings as PR comments, so developers see just what changed. You decide what enforcement looks like — break the build, block the PR, notify, or open a ticket — per policy.
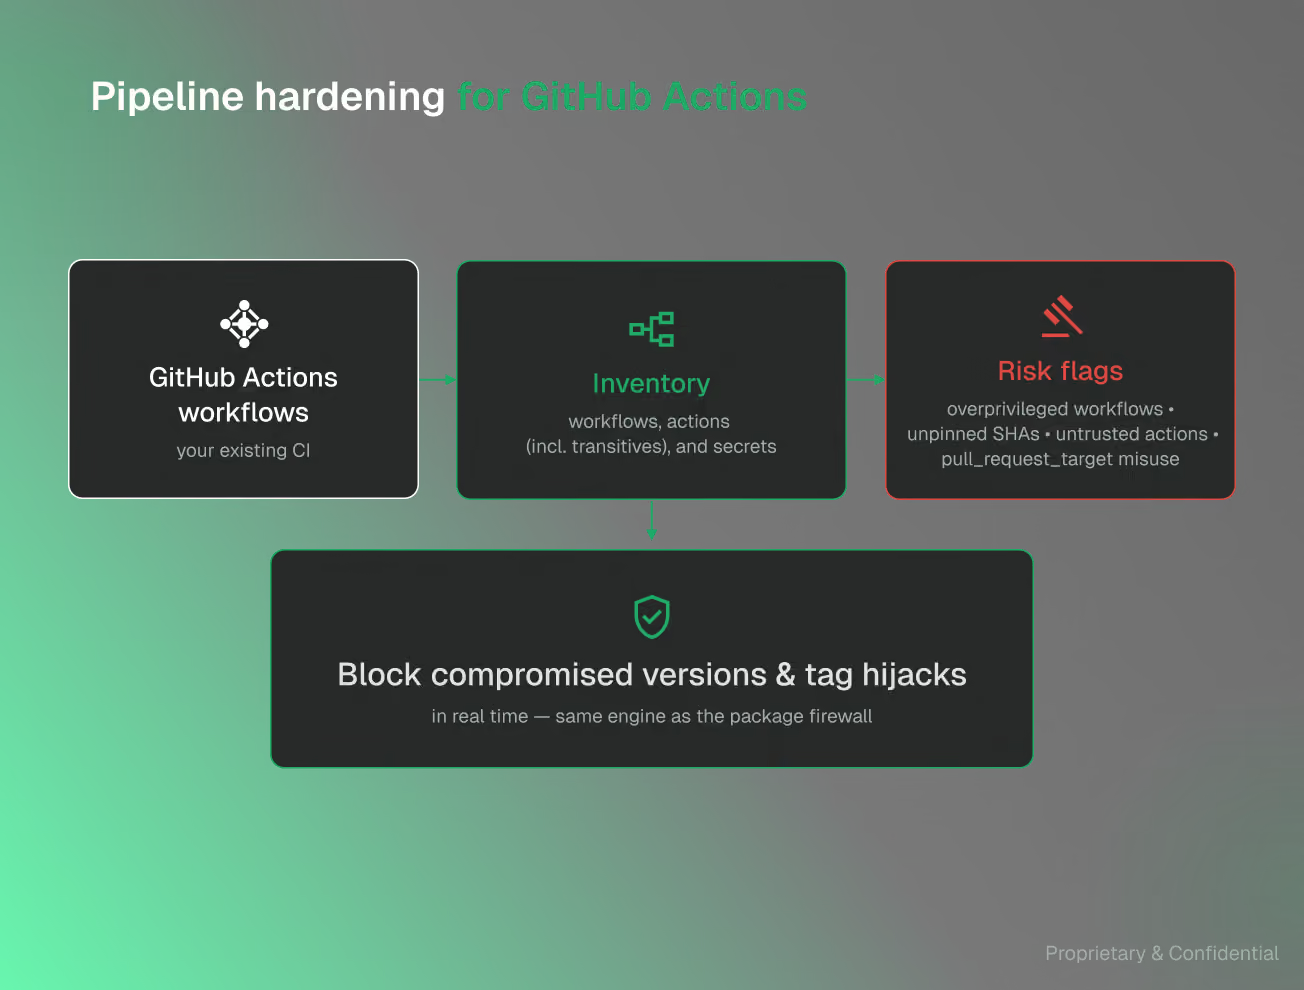
Endor Labs inventories every workflow and the actions it pulls in, scores each action, and flags risky patterns like overly broad permissions, unpinned tags, and untrusted input flowing into shell commands. Compromised action versions and tag hijacks can be blocked in real time.
No. The same reachability, Endor Scores, dashboard, and policy engine that power dependency analysis apply to your pipelines and repositories, so CI/CD security lives in the same program and evidence model as the rest of your supply chain.
It drops into the CI/CD toolchain you already run without rip-and-replace, using keyless authentication and policy-as-code you can enforce across every repo and pipeline through the API.