Search Results

Learn about software supply chain security and Endor Labs
Search all our {count} unique resources
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Loading the Results...
Detecting Business Logic Flaws and IDOR with AI SAST
chrome_reader_mode
Blog

Detecting Business Logic Flaws and IDOR with AI SAST

IDOR and broken access control look like valid code, so rule-based SAST misses them. See vulnerable and fixed examples and how AI SAST finds them.

Best Application Security Platforms in 2027: 8 Ranked and Compared
chrome_reader_mode
Blog

Best Application Security Platforms in 2027: 8 Ranked and Compared

Eight application security platforms compared on reachability, noise, coverage, and remediation, with the team each one fits.

agent-framework compromised: Python startup hooks steal Azure and CI credentials
chrome_reader_mode
Blog

agent-framework compromised: Python startup hooks steal Azure and CI credentials

Java4Shell (CVE-2026-114938): Pre-Auth Heap Overflow in OpenJDK
chrome_reader_mode
Blog

Java4Shell (CVE-2026-114938): Pre-Auth Heap Overflow in OpenJDK

Fable 5.2: cheaper and faster, not more secure, and much more memorization
chrome_reader_mode
Blog

Fable 5.2: cheaper and faster, not more secure, and much more memorization

Anthropic released Claude Fable 5.2 on November 9, 2026, with a 20% price cut and a claim of large coding gains. We ran it under Claude Code on the same real-world coding tasks we use for the Agent Security League.

Secure Code Review Checklist
chrome_reader_mode
Blog

Secure Code Review Checklist

A copyable secure code review checklist for pull requests, organized by review area, with a why and an OWASP reference for each item, plus a PR template.

How to Benchmark AI Code Security Review Tools Before You Buy
chrome_reader_mode
Blog

How to Benchmark AI Code Security Review Tools Before You Buy

Benchmark AI code security review tools before you buy. Seed 8 flaw categories with decoys, run PRs on your own stack, and score evidence, triage, and fixes.

Hijacked GitHub Accounts Push “wfx” CI Secret Stealer to Thousands of Repositories
chrome_reader_mode
Blog

Hijacked GitHub Accounts Push “wfx” CI Secret Stealer to Thousands of Repositories

Endor Labs + OpenAI: Strengthening the Defense Factory With Accelerated Remediation
chrome_reader_mode
Blog

Endor Labs + OpenAI: Strengthening the Defense Factory With Accelerated Remediation
How AI SAST Works: Detection, Triage, and Remediation Agents
chrome_reader_mode
Blog

How AI SAST Works: Detection, Triage, and Remediation Agents

See how AI SAST works step by step: what the detection, triage, and remediation agents do, the context each one uses, and how they hand off.

AI SAST vs Traditional SAST: What Changes When Static Analysis Can Reason
chrome_reader_mode
Blog

AI SAST vs Traditional SAST: What Changes When Static Analysis Can Reason

AI SAST vs traditional SAST, compared: how reasoning changes detection of authorization flaws, false positives, triage, fixes, speed, and cost

5 Best ADLC Security Tools for Teams Shipping with Coding Agents (2027)
chrome_reader_mode
Blog

5 Best ADLC Security Tools for Teams Shipping with Coding Agents (2027)

Which tools secure the agentic development lifecycle? A practical map of agent governance, dependency security, code review, secrets, and runtime controls.

Best AI SAST Tools in 2027
chrome_reader_mode
Blog

Best AI SAST Tools in 2027

Which AI SAST tools find access control and logic flaws rule-based scanners miss? See 9 tools ranked, a comparison table, and how to test them on your PRs.

What is AI SAST? A guide to AI-powered static application security testing
chrome_reader_mode
Blog

What is AI SAST? A guide to AI-powered static application security testing

AI SAST combines program analysis, dataflow tracing, and LLM reasoning to find logic flaws rule-based SAST misses. Learn how it works and how to evaluate tools.

2.6x the findings, 12x fewer tokens: Getting more from your security review agents
chrome_reader_mode
Blog

2.6x the findings, 12x fewer tokens: Getting more from your security review agents

Simplifying Onboarding for Diverse SCMs
chrome_reader_mode
Blog

Simplifying Onboarding for Diverse SCMs

AI Code Review vs SAST: What Each Catches and How to Use Both
chrome_reader_mode
Blog

AI Code Review vs SAST: What Each Catches and How to Use Both

AI code review vs SAST: how detection, bug coverage, determinism, false positives, and cost differ, and why combining them catches more real risk.

What Is AI Code Review? The Complete Guide
chrome_reader_mode
Blog

What Is AI Code Review? The Complete Guide

AI code review uses AI to review pull requests for bugs, quality, and security. Learn how it works, how it differs from SAST and linters, and what agentic review adds.

Best Code Security Review Tools and Solutions in 2027
chrome_reader_mode
Blog

Best Code Security Review Tools and Solutions in 2027

Compare the best code security review tools of 2026 for pull requests and CI. See how Endor Labs and 8 others review first-party and AI-generated code before merge.
What is code security review? A guide to secure code review in the AI era
chrome_reader_mode
Blog

What is code security review? A guide to secure code review in the AI era

Learn what code security review is, what to check in every pull request, and how AI coding agents change the job, with a workflow and metrics AppSec teams can use.

Endor Labs is a Leader in The Forrester Wave™ for Agentic Development Security
chrome_reader_mode
Blog

Endor Labs is a Leader in The Forrester Wave™ for Agentic Development Security
Decoding the agent stack: What MCP servers, skills, plugins, hooks, and harnesses actually do for AppSec
chrome_reader_mode
Blog

Decoding the agent stack: What MCP servers, skills, plugins, hooks, and harnesses actually do for AppSec

Meta’s New Muse Wonder: record FuncPass, but mid-table SecPass
chrome_reader_mode
Blog

Meta’s New Muse Wonder: record FuncPass, but mid-table SecPass

Docker Sandboxes vulnerability lets AI agents access sensitive files outside their sandbox (CVE-2026-103916)
chrome_reader_mode
Blog

Docker Sandboxes vulnerability lets AI agents access sensitive files outside their sandbox (CVE-2026-103916)

Docker Sandboxes vulnerability lets AI agents access sensitive files outside their sandbox (CVE-2026-103916)

The Binance hack is a warning: developer workstations hold the keys to your business
chrome_reader_mode
Blog

The Binance hack is a warning: developer workstations hold the keys to your business

What is an AI bill of materials (AIBOM)?
chrome_reader_mode
Blog

What is an AI bill of materials (AIBOM)?

An AI bill of materials (AIBOM) is a machine-readable inventory of the models, datasets, and AI components in a system. Learn what it contains and which standards apply.

ADLC metrics: How to measure agentic development security
chrome_reader_mode
Blog

ADLC metrics: How to measure agentic development security

A guide to ADLC security metrics, baselines, and scorecards.

Endor Labs + Google Antigravity: Secure code by default in agentic workflows
chrome_reader_mode
Blog

Endor Labs + Google Antigravity: Secure code by default in agentic workflows
Endor Labs + Google Antigravity: Secure code by default in agentic workflows
Endor Labs AI SAST Finds Two Apache Kafka Zero-Days: Unbounded Memory Allocation from Brokers to Kafka Streams
chrome_reader_mode
Blog

Endor Labs AI SAST Finds Two Apache Kafka Zero-Days: Unbounded Memory Allocation from Brokers to Kafka Streams
Endor Labs AI SAST Finds Two Apache Kafka Zero-Days: Unbounded Memory Allocation from Brokers to Kafka Streams

ADLC compliance: Mapping agentic development to NIST SSDF, the OWASP LLM Top 10, and the EU AI Act
chrome_reader_mode
Blog

ADLC compliance: Mapping agentic development to NIST SSDF, the OWASP LLM Top 10, and the EU AI Act

Coding agents changed how software gets built. Here's how ADLC stages map to SSDF practices, OWASP GenAI risks, and the EU AI Act, and what evidence holds up.

The ADLC maturity model: stages of agentic development security
chrome_reader_mode
Blog

The ADLC maturity model: stages of agentic development security

Score your agentic development security across the code agents write and the actions they take, with clear stages, proof artifacts, and progress metrics.

How to evaluate ADLC security solutions: A buyer's checklist
chrome_reader_mode
Blog

How to evaluate ADLC security solutions: A buyer's checklist

A practical checklist for evaluating ADLC security solutions: coverage for code and coding agents, evidence-backed accuracy, agent-loop workflow fit, and a proof of concept you can score.

Introducing AURI Fix for Open Source
chrome_reader_mode
Blog

Introducing AURI Fix for Open Source

Introducing AURI Fix for Open Source

What is a software factory? How it works and where AI fits
chrome_reader_mode
Blog

What is a software factory? How it works and where AI fits

A software factory definition in plain terms: how the workflow runs from request to release, and where AI agents, security, and people fit.

Everything, everywhere, all at once… the week software broke
chrome_reader_mode
Blog

Everything, everywhere, all at once… the week software broke

ADLC security best practices: how to secure agentic development from prompt to production
chrome_reader_mode
Blog

ADLC security best practices: how to secure agentic development from prompt to production

ADLC security best practices for AppSec and platform teams: inventory agents and MCP servers, enforce policy on agent actions, vet packages at install, and secure agent code.

What is the AI-native SDLC? AI SDLC, AI-DLC, and ADLC explained
chrome_reader_mode
Blog

What is the AI-native SDLC? AI SDLC, AI-DLC, and ADLC explained

A clear guide to AI-native SDLC terminology, including the difference between Agentic Development Lifecycle and Agent Development Lifecycle.

eMudhra Intermediate CA Compromise: The Trust Stores You Patched, and the Ones You Didn't Know You Had
chrome_reader_mode
Blog

eMudhra Intermediate CA Compromise: The Trust Stores You Patched, and the Ones You Didn't Know You Had

LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials
chrome_reader_mode
Blog

LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials

LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619)
chrome_reader_mode
Blog

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619)

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619)

Once upon a codebase forest: The story behind Harness Your Mechs
chrome_reader_mode
Blog

Once upon a codebase forest: The story behind Harness Your Mechs

Harness Your Mechs: What to build & what to buy when you bring AI into AppSec
chrome_reader_mode
Blog

Harness Your Mechs: What to build & what to buy when you bring AI into AppSec

Gemini 4 Argon on Cursor: solid security score, two unique solves, but slower and more expensive
chrome_reader_mode
Blog

Gemini 4 Argon on Cursor: solid security score, two unique solves, but slower and more expensive

Cursor with Gemini 4 Argon matches Fable 5 at 29% SecPass — tying for the top security score on Cursor — and uniquely solves two tasks no other combo on the leaderboard secures. But it is also the slowest and most expensive recent frontier combo we have tested.
The applied AI playbook for AppSec
chrome_reader_mode
Ebook/Report

The applied AI playbook for AppSec

The rest of the EU Cyber Resiliency Act lands on December 11th, 2027.
chrome_reader_mode
Blog

The rest of the EU Cyber Resiliency Act lands on December 11th, 2027.

Same analysis, your account: BYOK for Endor Labs AI SAST
chrome_reader_mode
Blog

Same analysis, your account: BYOK for Endor Labs AI SAST

Run Endor Labs AI SAST on your own approved LLM provider.

Endor Labs and Bright Security Partner to Close the Gap Between Discovery and Remediation
chrome_reader_mode
Blog

Endor Labs and Bright Security Partner to Close the Gap Between Discovery and Remediation

Endor Labs and Bright Security Partner to Close the Gap Between Discovery and Remediation

Tensorlake npm package compromised by Shai-Hulud in latest software supply chain attack
chrome_reader_mode
Blog

Tensorlake npm package compromised by Shai-Hulud in latest software supply chain attack

Endor Labs + SpaceXSI: Securing every stage of agentic software delivery
chrome_reader_mode
Blog

Endor Labs + SpaceXSI: Securing every stage of agentic software delivery

Endor Labs + SpaceXSI: Building the security foundation for agentic coding

What does it mean to sandbox an AI coding agent?
chrome_reader_mode
Blog

What does it mean to sandbox an AI coding agent?

A compromised release of the nx build package shipped a post-install script that did something the industry had not seen before.

GPT-6.1 Sol on Codex: Astra-level security, a third faster, zero cheating
chrome_reader_mode
Blog

GPT-6.1 Sol on Codex: Astra-level security, a third faster, zero cheating

Nine days after GPT-6 Sol, Codex with GPT-6.1 Sol scores 77.7% FuncPass and 34.1% SecPass — within one task of GPT-6 Astra on security, a third faster, and with zero confirmed cheating.

Sandboxes: A Primer on Containing Things That Don't Want to Be Contained
chrome_reader_mode
Blog

Sandboxes: A Primer on Containing Things That Don't Want to Be Contained

Sandboxes Explained: What Each Type Actually Isolates

GPT-6 Sol on Codex: average scores, quarter the cost
chrome_reader_mode
Blog

GPT-6 Sol on Codex: average scores, quarter the cost

Codex with GPT-6 Sol scores 72.1% FuncPass and 25.1% SecPass for $104 on Azure — 78% cheaper than Astra ($468) — with zero confirmed cheating.

Endor Labs Featured in Gartner Research on Claude Code Permissions and Agent Governance
chrome_reader_mode
Blog

Endor Labs Featured in Gartner Research on Claude Code Permissions and Agent Governance

Endor Labs was recently featured in the Gartner® report First Take: Claude Code Is Defaulting to Automated Permissions — Update Your Governance Controls, published August 24, 2026. The report examines an important change in how Claude Code handles permissions and the broader governance implications as coding agents take more actions without requiring a developer to approve each one.
Project-Mount Symlink Traversal in brig: How a Sandbox Reaches Host Directories It Was Never Given
chrome_reader_mode
Blog

Project-Mount Symlink Traversal in brig: How a Sandbox Reaches Host Directories It Was Never Given

Opus 5.5: 6x cheaper and 2x faster than Fable 5.1, but only 33.5% of code is secure
chrome_reader_mode
Blog

Opus 5.5: 6x cheaper and 2x faster than Fable 5.1, but only 33.5% of code is secure

Claude Code with Opus 5.5 finishes coding tasks in a median of 2.2 minutes for $116 in total, the fastest run on our board and the cheapest Anthropic run by far, but lands at only 33.5% for secure code.
Engineering a security harness for AI coding agents
chrome_reader_mode
Blog

Engineering a security harness for AI coding agents

Engineering a security harness for AI coding agents

The first part of the EU Cyber Resiliency Act comes into effect on September 11th. Are you ready?
chrome_reader_mode
Blog

The first part of the EU Cyber Resiliency Act comes into effect on September 11th. Are you ready?

The first part of the EU Cyber Resiliency Act comes into effect on September 11th. Are you Ready?

Introducing Package Firewall for VS Code Extensions: Detect and Block Malicious Extensions From the IDE
chrome_reader_mode
Blog

Introducing Package Firewall for VS Code Extensions: Detect and Block Malicious Extensions From the IDE

Learn how Endor Labs detects malicious VS Code extensions and poisoned updates and blocks them with Package Firewall before they reach developer workstations.

Introducing Threat Center and Package Firewall for VS Code Extensions: Malware Protection From the Registry to the Developer Workstation
chrome_reader_mode
Blog

Introducing Threat Center and Package Firewall for VS Code Extensions: Malware Protection From the Registry to the Developer Workstation

Threat Center and Package Firewall for VS Code Extensions

Better models are making agent patch review more expensive, not less
chrome_reader_mode
Blog

Better models are making agent patch review more expensive, not less

Agent fixes got 47% cheaper to generate. Review still costs ten times more.
GPT-6 Astra on Codex - the Biggest Codex Leap to Date
chrome_reader_mode
Blog

GPT-6 Astra on Codex - the Biggest Codex Leap to Date

GPT-6 Astra on Codex - the Biggest Codex Leap to Date

How Endor Labs AI SAST Learns What Matters to Your Organization
chrome_reader_mode
Blog

How Endor Labs AI SAST Learns What Matters to Your Organization

How Endor Labs AI SAST Learns What Matters to Your Organization

From SDLC to ADLC: why application security needs coding agent governance
chrome_reader_mode
Blog

From SDLC to ADLC: why application security needs coding agent governance

From SDLC to ADLC: why application security needs coding agent governance

The Secure Agentic Development Lifecycle (ADLC), Explained
chrome_reader_mode
Blog

The Secure Agentic Development Lifecycle (ADLC), Explained

Learn what a secure Agentic Development Lifecycle (ADLC) means, how it differs from SDLC, and which controls help govern coding agents and their output.

Agentic Development Security: How to Secure Code Your Agents Write
chrome_reader_mode
Blog

Agentic Development Security: How to Secure Code Your Agents Write

Learn agentic development security best practices to secure AI-generated code, dependencies, tools, and MCP workflows without slowing teams.

Hooks are the control plane for the agentic development lifecycle
chrome_reader_mode
Blog

Hooks are the control plane for the agentic development lifecycle

Hooks are the control plane for the agentic development lifecycle

The real test of AI-native code analysis: is your security debt shrinking?
chrome_reader_mode
Blog

The real test of AI-native code analysis: is your security debt shrinking?

The real test of AI-native code analysis: is your security debt shrinking?

Mini Shai-Hulud worm hits openapi-react-query-codegen, spreads across npm, RubyGems, and PyPI
chrome_reader_mode
Blog

Mini Shai-Hulud worm hits openapi-react-query-codegen, spreads across npm, RubyGems, and PyPI

FedRAMP 2026 vulnerability rules make reachability a requirement
chrome_reader_mode
Blog

FedRAMP 2026 vulnerability rules make reachability a requirement

FedRAMP 2026 vulnerability rules make reachability a requirement

Customer Zero: Implementing Package Firewall at Endor Labs
chrome_reader_mode
Blog

Customer Zero: Implementing Package Firewall at Endor Labs

Customer Zero: Implementing Package Firewall at Endor Labs

Heaps of Built-in's: How JavaScript Sandboxes work
chrome_reader_mode
Blog

Heaps of Built-in's: How JavaScript Sandboxes work

How JavaScript Sandboxes Work

GHSA-864f-rcv7-6rh4: Critical Type Confusion Vulnerability in isolated-vm
chrome_reader_mode
Blog

GHSA-864f-rcv7-6rh4: Critical Type Confusion Vulnerability in isolated-vm

GHSA-864f-rcv7-6rh4: Critical Type Confusion Vulnerability in isolated-vm

Why C Has Always Broken Static Analysis
chrome_reader_mode
Blog

Why C Has Always Broken Static Analysis

Why C Has Always Broken Static Analysis

Why Endor Labs AI SAST for C finds what other tools miss
chrome_reader_mode
Blog

Why Endor Labs AI SAST for C finds what other tools miss

Why Endor Labs AI SAST for C finds what other tools miss

Hacking your life with AI can get you hacked
chrome_reader_mode
Blog

Hacking your life with AI can get you hacked

Hacking your life with AI can get you hacked

How AI orchestration platforms ship RCE by design
chrome_reader_mode
Ebook/Report

How AI orchestration platforms ship RCE by design

How AI orchestration platforms ship RCE by design

When you can't upgrade: open source examples of Endor Patches
chrome_reader_mode
Blog

When you can't upgrade: open source examples of Endor Patches

When you can't upgrade: open source examples of Endor Patches

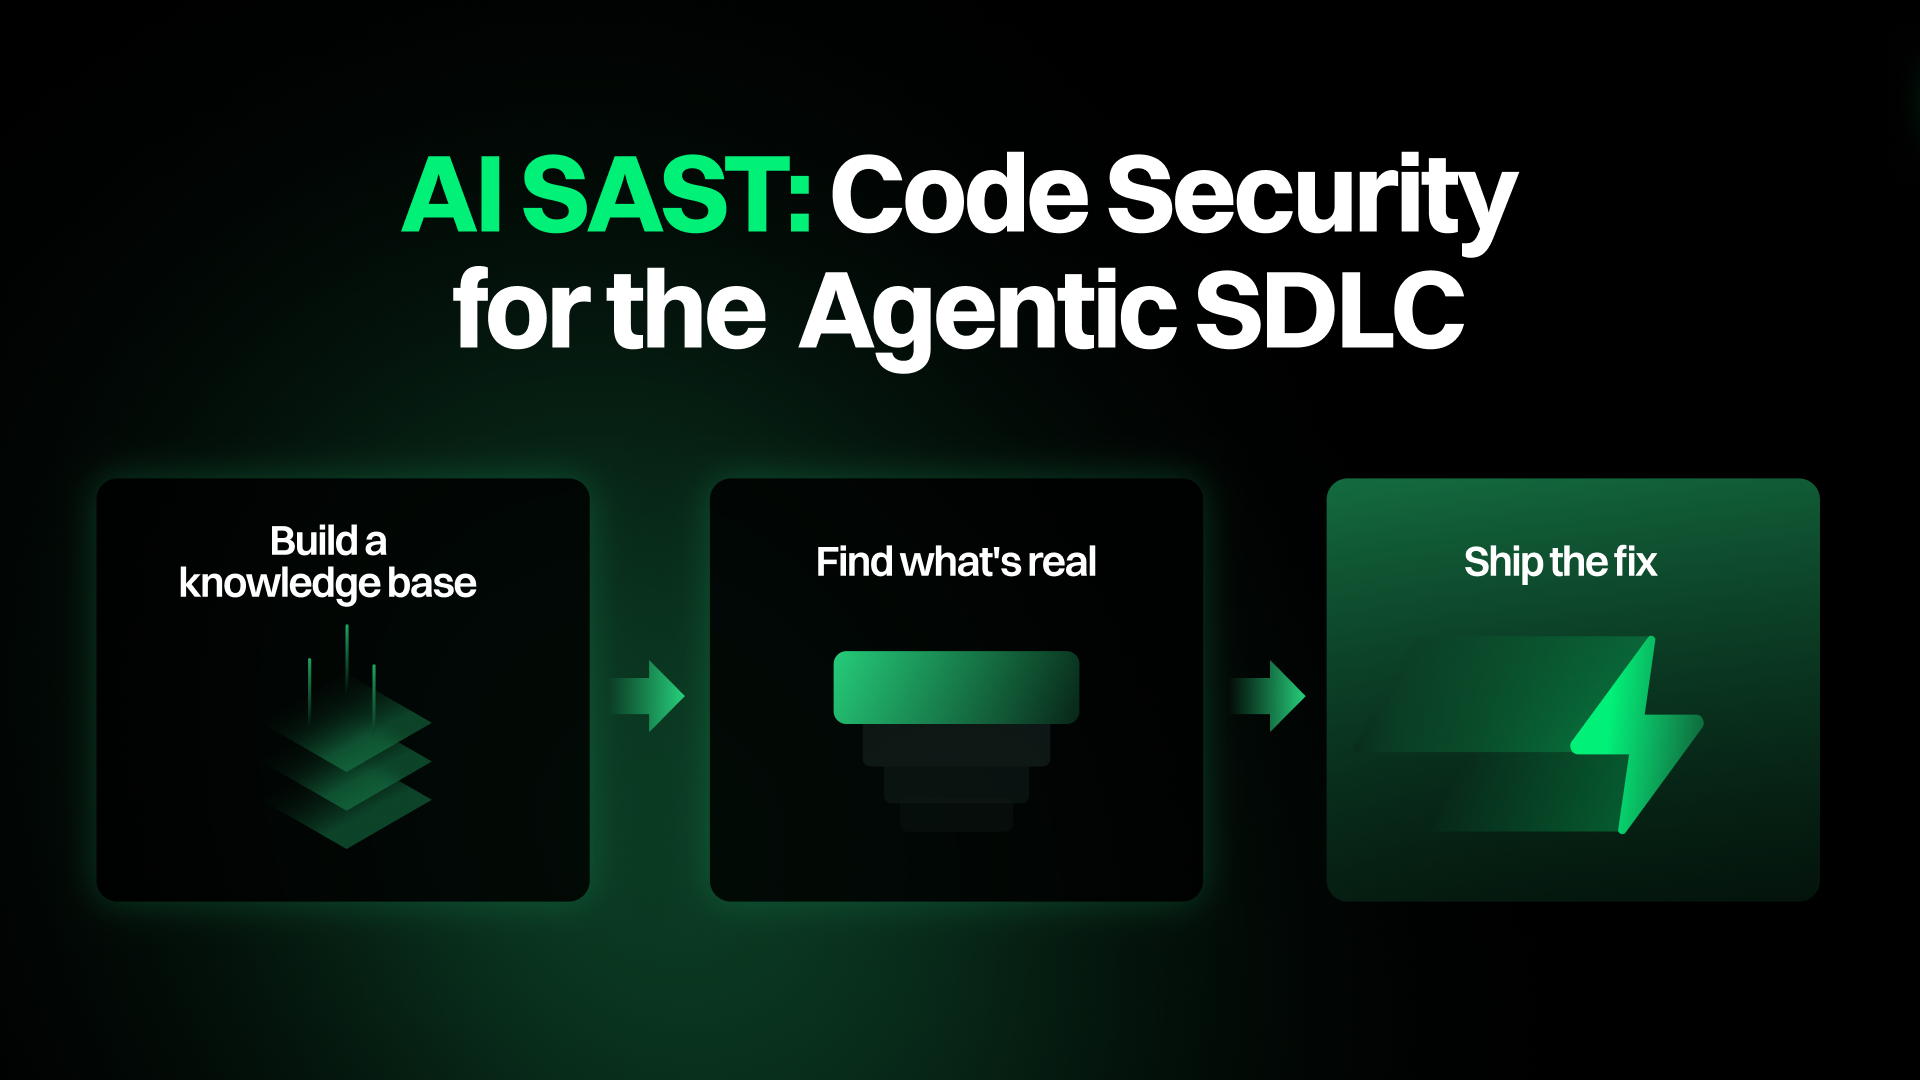
AI SAST: Code Security for the Agentic SDLC
chrome_reader_mode
Ebook/Report

AI SAST: Code Security for the Agentic SDLC

How Endor Labs AI SAST combines program analysis, agentic reasoning, and deterministic engineering to find and fix the flaws that matter in AI-written code.

CISO's Guide: Build vs Buy AI Code Security
chrome_reader_mode
Ebook/Report

CISO's Guide: Build vs Buy AI Code Security

CISO's Guide: Build vs Buy AI Code Security

Why NPM Malware Keeps Reaching for Bun
chrome_reader_mode
Blog

Why NPM Malware Keeps Reaching for Bun

Why NPM Malware Keeps Reaching for Bun | Supply Chain Security

Best in Class, Novel in Method: Opus 5 and the Recall-Then-Diverge Pattern
chrome_reader_mode
Blog

Best in Class, Novel in Method: Opus 5 and the Recall-Then-Diverge Pattern

Best in Class, Novel in Method: Opus 5 and the Recall-Then-Diverge Pattern

The Registry Just Became a Checkpoint. It Still Isn't Your Perimeter.
chrome_reader_mode
Blog

The Registry Just Became a Checkpoint. It Still Isn't Your Perimeter.

NPM Malware Compromises keyv and cacheable with 500M+ Weekly Downloads and Spreads to Hundreds of Packages
chrome_reader_mode
Blog

NPM Malware Compromises keyv and cacheable with 500M+ Weekly Downloads and Spreads to Hundreds of Packages

Critical Security Controls for Governing AI Coding Agents
chrome_reader_mode
Blog

Critical Security Controls for Governing AI Coding Agents

Endor Labs for Connected Products
chrome_reader_mode
Solution Brief

Endor Labs for Connected Products

Endor Labs for Connected Products

Endor Labs for Software & Tech
chrome_reader_mode
Solution Brief

Endor Labs for Software & Tech

Endor Labs for Software & Tech

Endor Labs for Financial Services
chrome_reader_mode
Solution Brief

Endor Labs for Financial Services

Endor Labs for Financial Services

SBOM Hub & VEX
chrome_reader_mode
Solution Brief

SBOM Hub & VEX

SBOM Hub & VEX

Endor Patches
chrome_reader_mode
Solution Brief

Endor Patches

Endor Patches

Artifact Signing
chrome_reader_mode
Solution Brief

Artifact Signing

Artifact Signing

AI Model Governance
chrome_reader_mode
Solution Brief

AI Model Governance

AI Model Governance

AI Code Review
chrome_reader_mode
Solution Brief

AI Code Review

AI Code Review

Container Security & Reachability
chrome_reader_mode
Solution Brief

Container Security & Reachability

Container Security & Reachability

Coding Agent Governance
chrome_reader_mode
Solution Brief

Coding Agent Governance

AI Coding Agent Governance: The Security Layer for the Agentic SDLC

Package Firewall
chrome_reader_mode
Solution Brief

Package Firewall

Package Firewall

Secrets Detection
chrome_reader_mode
Solution Brief

Secrets Detection

Secrets Detection: Find the Secrets That Are Actually Live

Software Supply Chain Security
chrome_reader_mode
Solution Brief

Software Supply Chain Security

Software Supply Chain Security

AI Code Governance: Secure AI-Generated Code and Govern the Agents That Write It
chrome_reader_mode
Solution Brief

AI Code Governance: Secure AI-Generated Code and Govern the Agents That Write It

AI Code Governance: Secure AI-Generated Code and Govern the Agents That Write It

no-results
Sorry, no results matching your search.

Book a Demo

Protect your open source dependencies, secrets, and CI/CD pipelines without slowing down devs.