Snyk is one of the most widely adopted application security platforms, and many engineering teams start looking for a replacement once their programs scale. Alert volume climbs, developers stop trusting the tickets, and the security team spends more time triaging findings than reducing risk.
In Snyk's G2 reviews, one user wrote that "there are a lot of false positives that need to be identified and separated." When developers are buried in tickets for vulnerabilities that aren't exploitable in their code, trust breaks down fast.
This guide covers 10 Snyk alternatives and competitors across different categories: developer-friendly application security platforms, enterprise suites, open source tools, freemium options, and specialized tools for runtime and cloud teams. We start with Endor Labs, which was built to fix the noise, coverage, and remediation problems that push most teams off Snyk, then show where each other option falls short by comparison.
Quick answer: Among Snyk alternatives, Endor Labs is built for engineering teams leaving Snyk because of alert noise, developer friction, or coverage gaps. Its function-level reachability across code, dependencies, and containers cuts SCA alerts by 92% on average, and AURI by Endor Labs pairs each real finding with evidence-based remediation. Other Snyk alternatives include the open source trio of Opengrep, Syft and Trivy, GitHub Advanced Security, Semgrep, Upwind, Wiz Code, Aikido Security, Checkmarx, Veracode and Black Duck, each with narrower coverage or more manual work.
What is Snyk?
Snyk is a security platform that scans your code and dependencies for vulnerabilities. It combines software composition analysis (SCA) for open source libraries, static application security testing (SAST) for your own code through Snyk Code, and container and infrastructure as code (IaC) scanning. It plugs into developer workflows through the CLI, IDE plugins, and CI/CD pipelines.
Snyk earned its popularity by making security accessible to developers rather than requiring a dedicated security team. You can run scans from your terminal, see results in your editor, and get alerts and fix pull requests in your repositories. The problems start as codebases, teams, and compliance requirements grow.
Why teams switch from Snyk
Most teams that leave Snyk run into one or more of these five problems.
1. Alert fatigue hurts productivity and morale
Snyk tends to surface every theoretical risk without enough context about exploitability. Snyk's reachability analysis covers only a subset of languages (Java, JavaScript and TypeScript, and Python), and other ecosystems fall back to severity-based scoring. For a typical engineering organization, that means thousands of findings, most of which aren't reachable by user input or executable in production. Security teams end up researching each one by hand, while developers learn to ignore the noise.
Common examples include:
- A critical alert for a logging library vulnerability when your application only uses that library's configuration parsing functions
- Hours spent investigating a dependency issue that affects a test utility, not production code
- A vulnerable function in a transitive dependency six layers deep that your code never calls
In one customer deployment, Endor Labs cut the monthly queue from 2,600 findings to 146 actionable issues after the team moved off Snyk, and across customers it measures a 92% average reduction in SCA alerts. At that volume, developers can act on every ticket instead of ignoring the queue.
2. Coverage thins out in complex build systems
If you use Bazel, monorepos, or C/C++ codebases, Snyk's coverage gets noticeably thinner. Teams report managing separate configurations for each service in a monorepo, and results that differ between the CLI and SCM integrations, which leaves security and engineering unsure which findings are real. Silent failures, coverage gaps, and inaccurate results waste time on false positives and miss real vulnerabilities.
3. Per-developer pricing climbs at scale
Snyk prices per contributing developer. Its Team plan starts at $25 per developer per month, its Ignite plan starts at $1,260 per developer per year for organizations with fewer than 50 developers, and Enterprise pricing is custom. Across hundreds of developers, teams often end up choosing between full coverage and budget.
4. Deployment and data residency requirements
Snyk is delivered primarily as SaaS. Teams with air-gapped environments or strict data residency rules often find its deployment options narrower than they need.
5. The AI promise needs proof
Like most vendors, Snyk has rebranded heavily around AI. Teams expecting mature AI-driven analysis, especially AI model discovery and governance, should confirm which capabilities ship today and which sit on a roadmap. Coding agents now write a growing share of code, so security checks need to run where agents write it, before it reaches a pull request. Our guide to the secure agentic development lifecycle (ADLC) explains how to secure that workflow.
How to narrow the field: start with what you're replacing
Before comparing tools, name the problem driving the switch. For the most common reasons teams leave Snyk, Endor Labs is the place to start.
What are the top Snyk alternatives in 2027?
Endor Labs leads the list as the most complete replacement for Snyk. The other nine cover narrower use cases.
- Developer-friendly alternative: Endor Labs
- Open source alternatives: Opengrep, Syft and Trivy
- Freemium alternative: GitHub Advanced Security
- Open core alternative: Semgrep
- Runtime alternative: Upwind
- Cloud teams alternative: Wiz Code
- Small teams alternative: Aikido Security
- Enterprise SAST alternative: Checkmarx
- Compliance-focused alternative: Veracode
- License compliance alternative: Black Duck
Detailed comparison of Snyk alternatives
1. Developer-friendly Snyk alternative: Endor Labs
Endor Labs was built to fix the three problems that push teams off Snyk: noise, shallow reachability, and developer friction.
What makes Endor Labs different
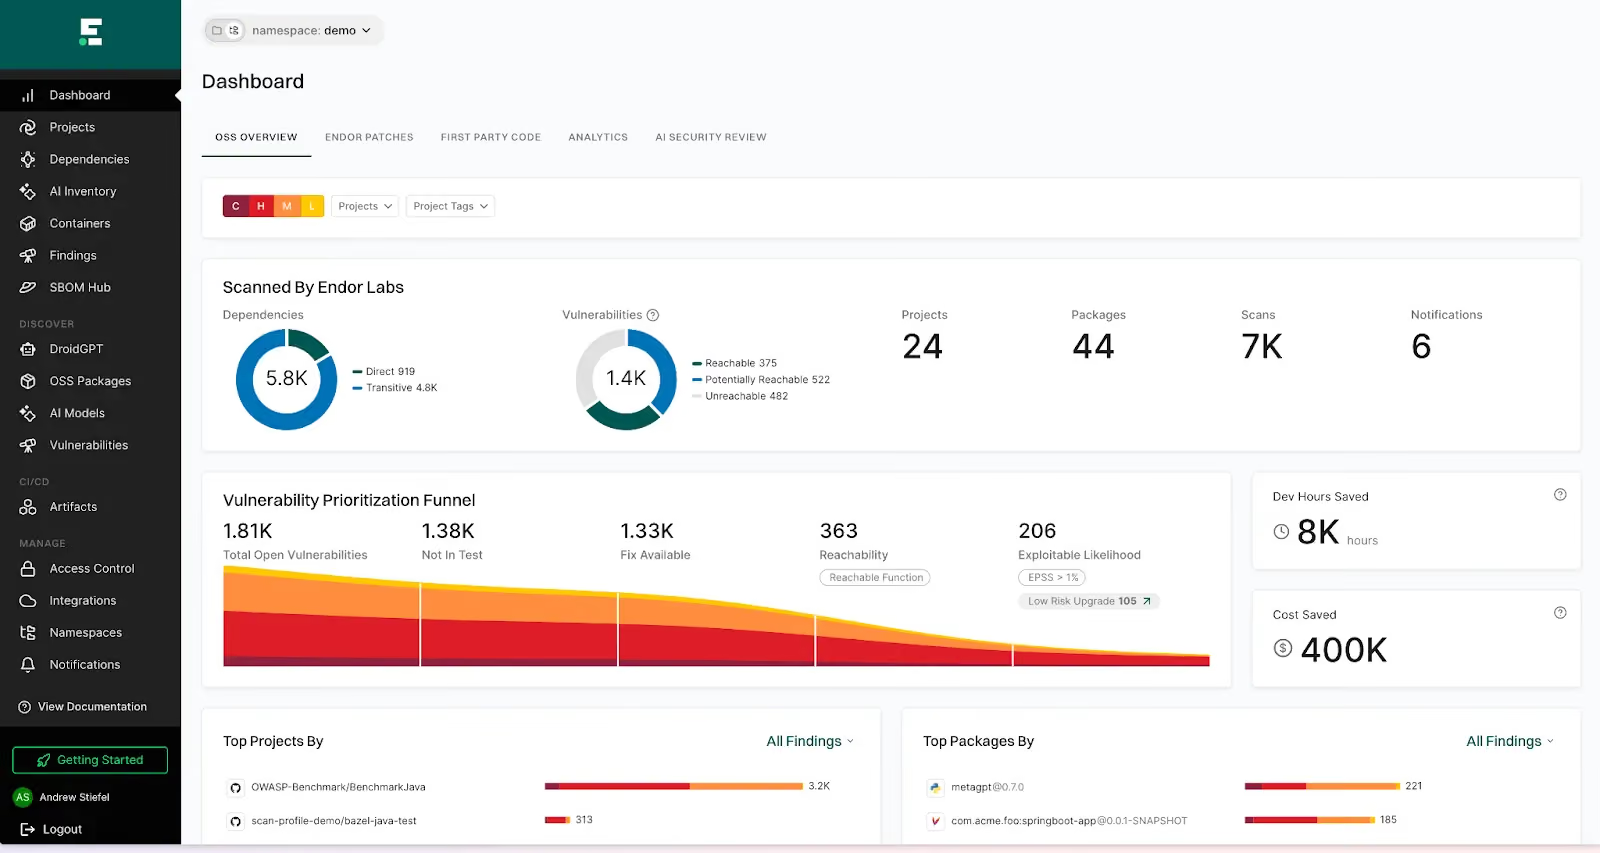
Endor Labs was designed as an AI-native platform from the start. It builds a call graph that connects your code, dependencies, and container layers, then runs function-level reachability analysis across all three. That means it can tell you whether vulnerable code is actually called by your application, which sharply reduces false positives.
The reachability extends through the entire dependency graph, including transitive dependencies. When a critical vulnerability appears in a package six layers deep, Endor Labs can determine whether your code ever reaches that function. If it doesn't, your engineers don't spend time on a theoretical risk.
What reachability looks like on a real finding
Take the logging library example above. A package-level scanner sees a vulnerable version in your manifest and opens a critical ticket for every service that includes it. Function-level reachability traces your call paths, finds that most services only call the library's configuration parser, and deprioritizes those findings with the call-path evidence attached. The service that does reach the vulnerable function gets the ticket, along with the exact path from your code to the flaw. For a side-by-side look at dependency identification, false positive reduction, and prioritization, see our benchmark of Endor Labs and Snyk across 10 open source projects.
Full coverage across code, secrets, open source dependencies, containers, and CI/CD
The Endor Labs platform includes SAST, SCA, secrets detection, malicious package detection, and container scanning in one experience. For AI governance, its AI-BOM and AI-SPM capabilities discover and inventory every AI model and service in your applications, then assess security, licensing, and compliance risks.
Endor Labs' AI SAST uses multiple specialized AI agents working together to analyze code context, achieving a 95% false positive reduction through triage and prioritization. These agents use your codebase and business context to decide which findings matter.
AURI by Endor Labs, the platform's AI security analyst, uses this program understanding to deliver evidence-based remediation. AURI also works where coding agents write code, through Hooks, Skills, MCP, CLI, and API, so agents can choose safe dependencies before code reaches a pull request.
A developer experience teams trust
Endor Labs shows clear evidence directly in pull requests and IDEs, with no context switching. When a vulnerability matters, developers see why it matters, where it's reachable, and how to fix it. Upgrade impact analysis identifies breaking changes before suggesting a fix, and Endor Patches provide fixes for libraries you can't safely upgrade.
Organizations like Atlassian, Cursor, and OpenAI have switched to Endor Labs to reduce noise and rebuild developer trust in their application security programs.
Who should consider Endor Labs
- Engineering organizations with 50 or more developers that are tired of noise
- Companies using Bazel, C/C++, or complex build systems that need complete coverage
- Teams building AI-native applications or using coding agents who need AI governance in production now
- Security programs that have lost developer trust and need to rebuild it with accurate, actionable findings
Book a demo to see function-level reachability on your own repositories.
2. Open source Snyk alternatives: Opengrep, Syft, Trivy
If you're comfortable with command-line tools and have engineering resources to build your own security workflows, open source tools provide scanning without vendor lock-in.
What it includes
- Opengrep is a fork of Semgrep's open source SAST engine, focused on pattern-based static analysis. It's fast and supports a wide range of languages.
- Syft generates software bills of materials (SBOMs) and identifies dependencies in container images and filesystems.
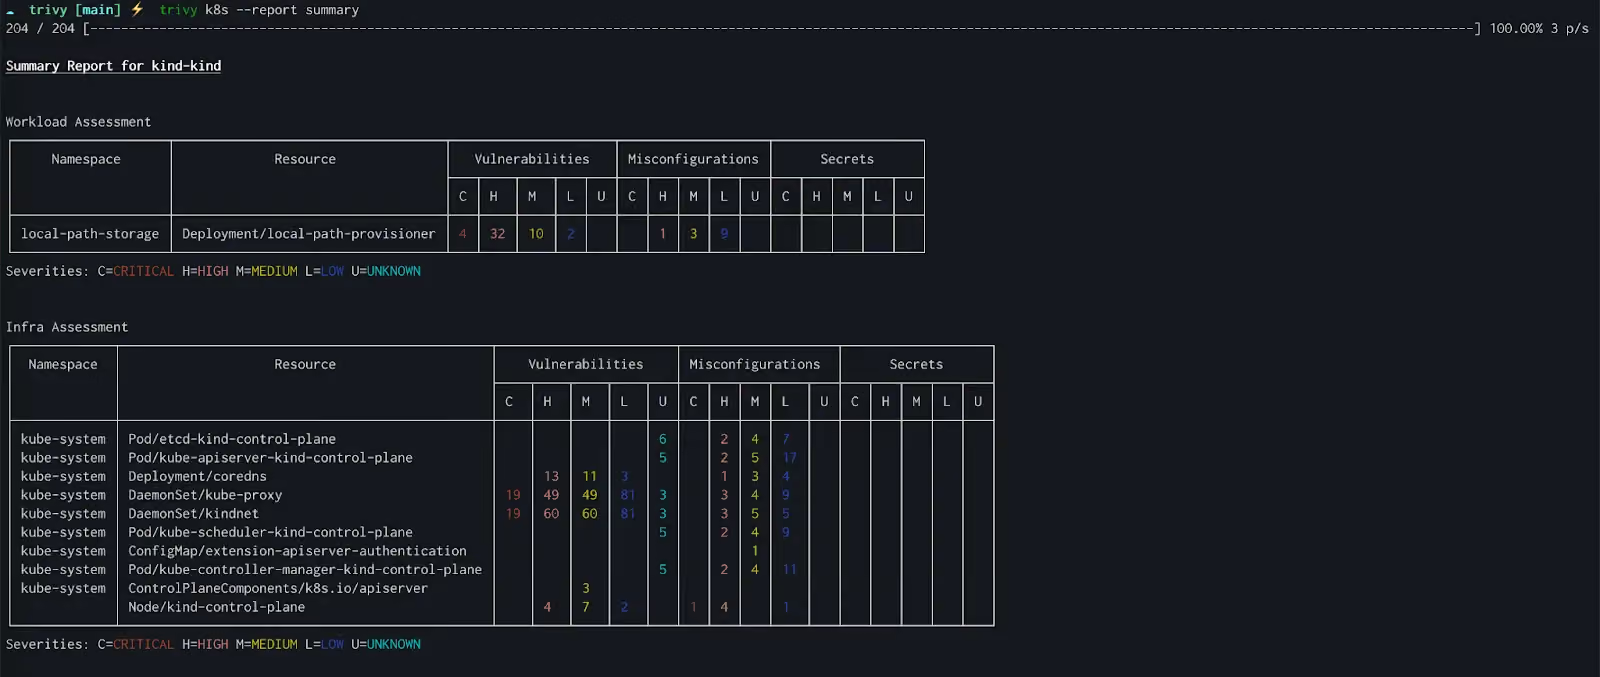
- Trivy scans for vulnerabilities in containers, Kubernetes, IaC, and code.
These tools are actively maintained and free, but running them takes ongoing engineering work. You maintain rule sets, tune for false positives, build CI/CD integrations, and create dashboards. Compared with Snyk, you give up centralized reporting, automated remediation, reachability analysis, and a unified policy engine.
Noise can also get worse, because each tool generates findings independently with no shared context. Your security team becomes the integration layer, triaging across several sources of truth.
Who should consider it
- Small engineering teams with dedicated security engineers
- Organizations with strict open source requirements
- Companies building custom security platforms that are comfortable investing engineering time in tooling
How Endor Labs compares: Endor Labs gives you SAST, SCA, secrets detection, and container scanning in one platform, with function-level reachability and a single policy engine, so your security team stops acting as the integration layer.
3. Freemium Snyk alternative: GitHub Advanced Security
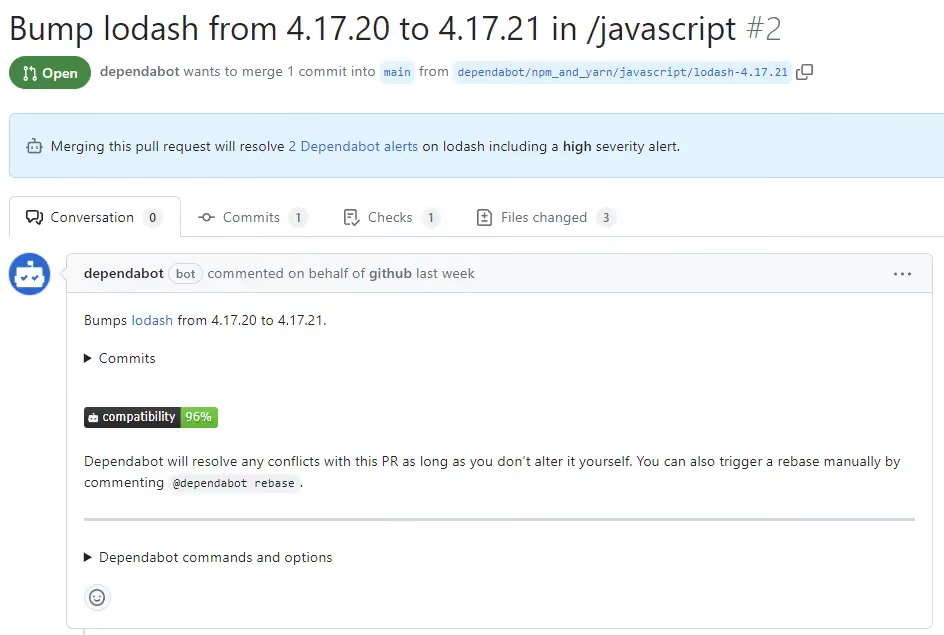
If your organization already builds on GitHub, GitHub Advanced Security (GHAS) provides built-in scanning without adding another vendor. Since April 2025, GitHub sells it as two products, GitHub Secret Protection and GitHub Code Security, and both are available on GitHub Team as well as Enterprise plans.
What it includes
GHAS offers CodeQL for SAST, Dependabot for SCA, and secret scanning. Developers see security alerts where they already work: pull requests, the security tab, and code scanning results.
Its main advantage is convenience: teams already on GitHub get scanning without a separate login, interface, or vendor.
Limitations
Like many scanning tools, GHAS can be noisy. CodeQL generates findings from taint analysis, but without deep reachability analysis you'll see alerts for code paths that aren't exploitable. Dependabot alerts on every vulnerable dependency, whether or not your code uses the affected functions.
GHAS also covers only GitHub repositories. If you use GitLab, Bitbucket, or several source control systems, it won't cover your whole codebase. Its secret scanning lacks the depth and validation of dedicated secrets tools.
Who should consider it
- Teams standardized on GitHub with security budgets to match
- Organizations that want good-enough scanning without adding vendor complexity
- Companies where the GitHub integration matters more than finding-level accuracy
How Endor Labs compares: Endor Labs works alongside GitHub Advanced Security and adds function-level reachability to cut Dependabot noise, and it also covers GitLab, Bitbucket, and other source control systems.
4. Open core Snyk alternative: Semgrep
Semgrep offers a middle ground: an open source SAST engine with a commercial platform layer for teams that need more. See our full list of Semgrep alternatives.
What Semgrep does well
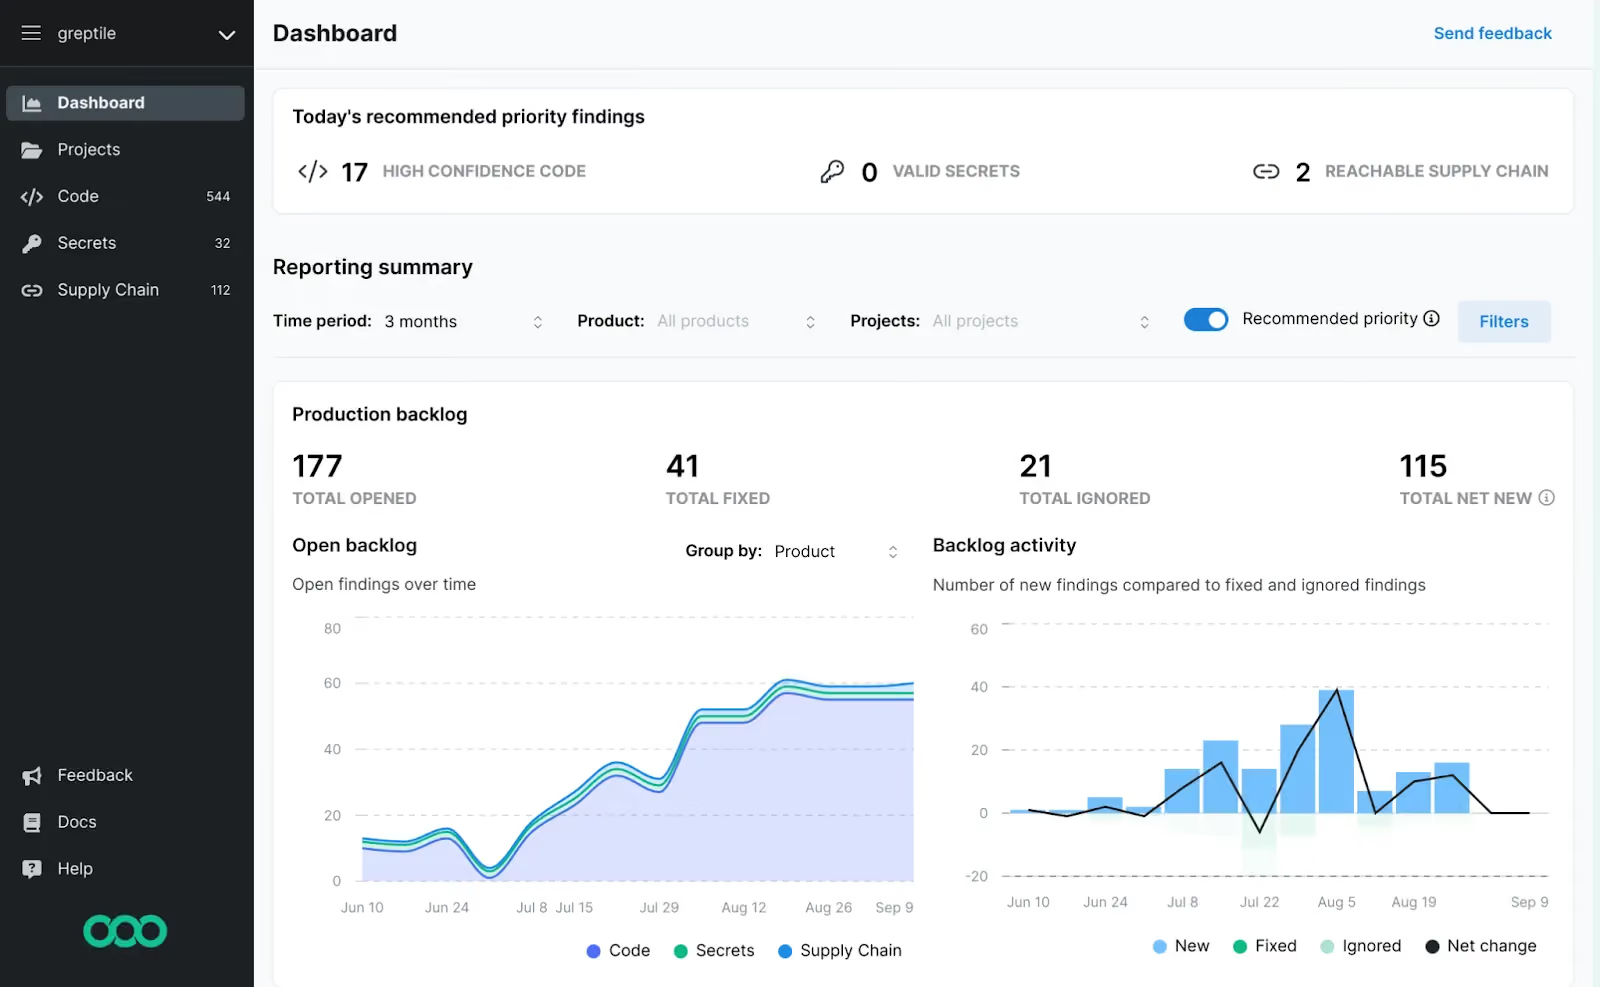
The open source engine is excellent for custom rule writing. If your security team needs to detect specific patterns, such as proprietary frameworks, internal libraries, or company-specific anti-patterns, Semgrep makes rule writing relatively straightforward. The Pro tier adds managed rules, prioritization, and some remediation.
For SCA, Semgrep offers reachability analysis, but only for direct dependencies. It doesn't extend to transitive dependencies, which is where most vulnerabilities hide in modern applications.
Limitations
SAST requires extensive rule writing to be effective. Out-of-the-box rules catch common patterns, but reaching low false positives with good coverage takes significant time in rule development and tuning.
Container scanning isn't included, so containerized applications need another tool. That recreates the multi-tool fragmentation many teams are trying to escape.
Who should consider it
- Security teams with engineering resources for rule development
- Organizations that need deep customization for proprietary code patterns
- Companies comfortable with a multi-tool stack where Semgrep handles SAST and other tools cover containers and infrastructure
How Endor Labs compares: Endor Labs extends reachability through transitive dependencies and includes container scanning, so you don't need a second tool to cover what Semgrep leaves out. See Endor Labs vs Semgrep.
5. Runtime Snyk alternative: Upwind
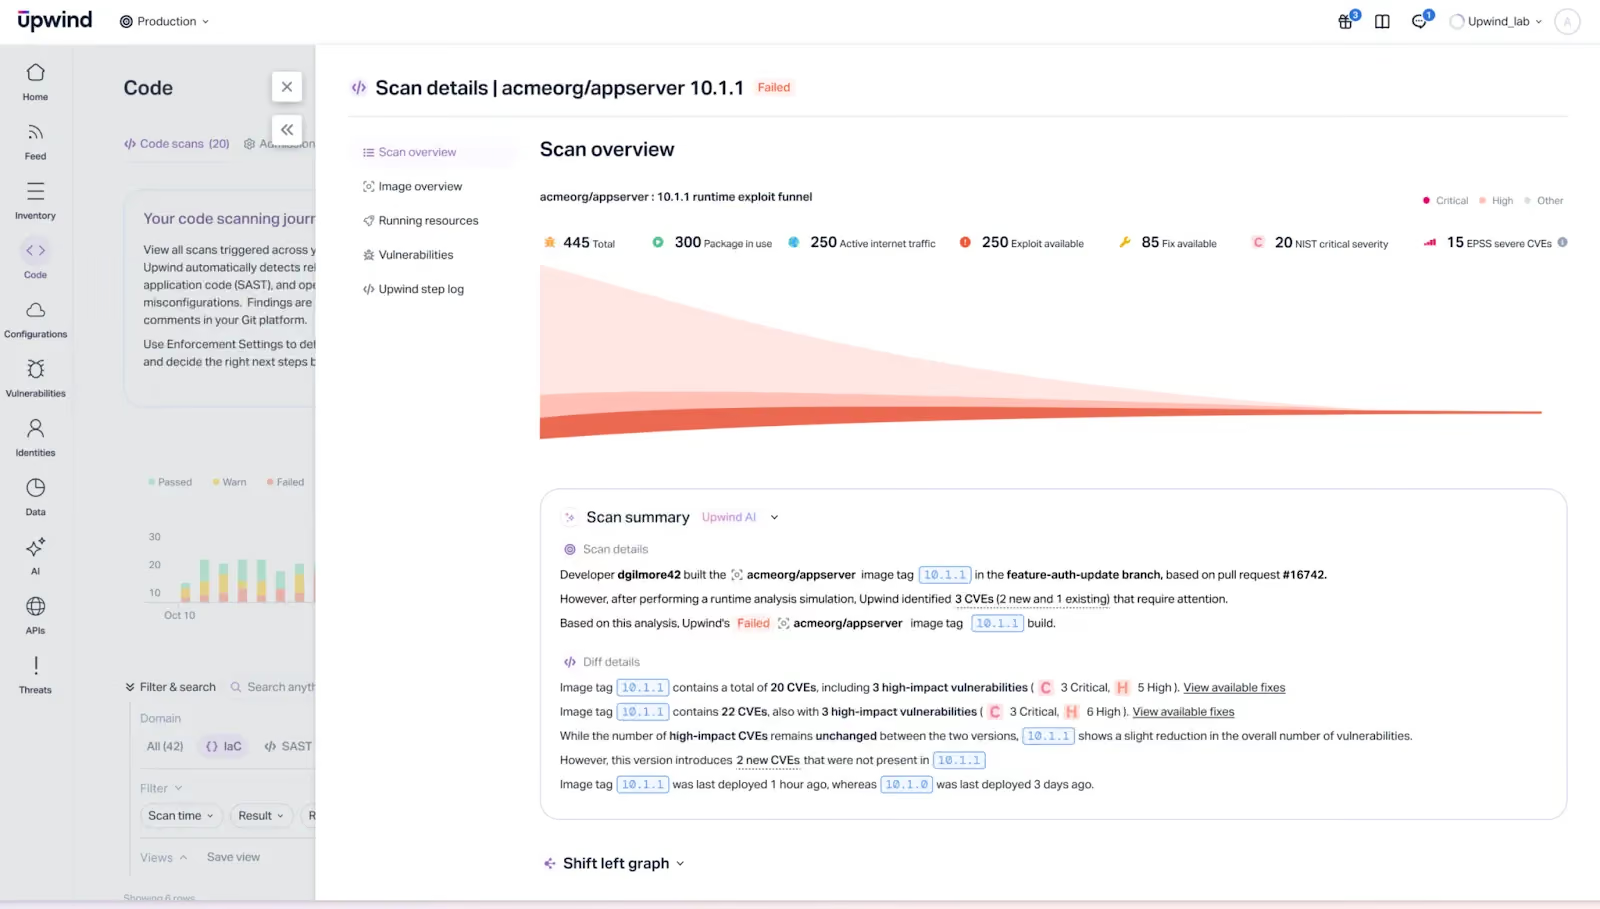
Upwind focuses on runtime analysis, flagging the vulnerabilities your production environment actually executes.
What it includes
Upwind monitors applications in production with eBPF-based instrumentation to observe which code paths execute, which libraries load, and which functions run. That lets it flag vulnerabilities that real traffic reaches.
If a vulnerable function never executes in production, Upwind deprioritizes it. Upwind also provides runtime SCA, secrets detection, and attack detection, so it can flag exploitation attempts in real time. For Kubernetes workloads, the eBPF approach gives deep visibility without installing an agent in every container.
Limitations
Runtime analysis only works for code that's already deployed. You don't get security feedback during development or in pull requests, so vulnerabilities can reach production before you know about them.
It also requires production instrumentation. Some security teams are comfortable with a tool observing production traffic and application behavior, and others aren't, even when the performance overhead is small.
Who should consider it
- Teams with mature CI/CD pipelines who want runtime validation on top of scanning during development
- Organizations that need production context to prioritize large vulnerability backlogs
- Security programs that have the basics covered and want runtime threat detection
How Endor Labs compares: Endor Labs shows reachability evidence in the pull request, before code ships, so teams fix exploitable issues before they reach production. See Endor Labs vs runtime SCA.
6. Cloud security Snyk alternative: Wiz Code
For organizations where cloud infrastructure security is the priority and application security comes second, Wiz provides cloud-native application protection (CNAPP) with some AppSec capabilities.
What it includes
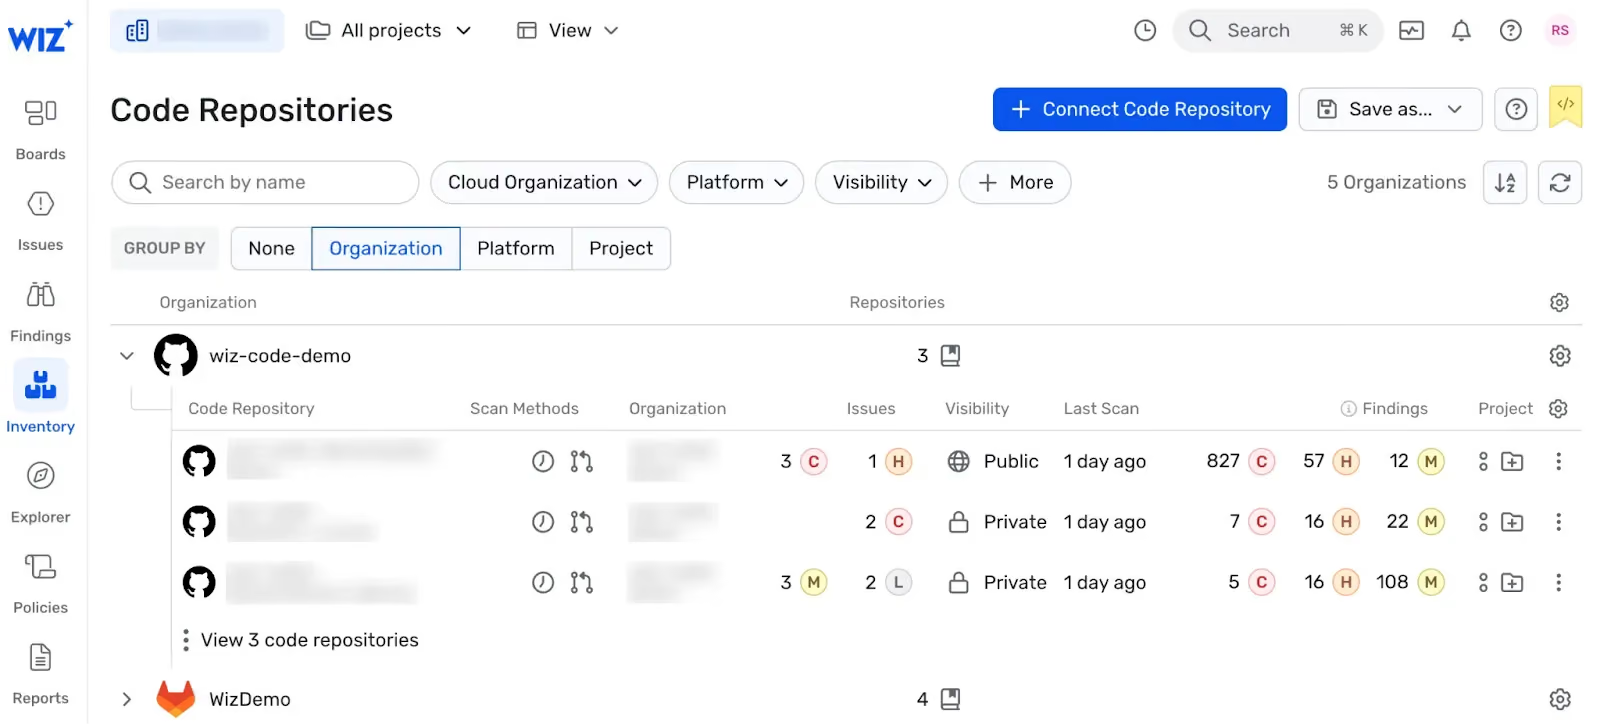
Wiz has been expanding into AppSec with Wiz Code, but code scanning remains secondary to its cloud infrastructure focus. It offers SCA, IaC scanning, and secrets detection, though it relies on integrating third-party scanners like Checkmarx for deeper SAST analysis.
Wiz is strongest at connecting application risk to cloud and runtime context. If you already use Snyk or another AppSec tool, Wiz can ingest those findings and enrich them with cloud context, showing which vulnerabilities sit in internet-exposed workloads versus isolated environments.
Limitations
Wiz's AppSec features aren't designed for deep developer workflow integration. The platform is built for security teams monitoring production, not developers working in IDEs and pull requests. If your goal is to catch issues during development, Wiz isn't optimized for that.
Who should consider it
- Cloud-heavy organizations where infrastructure security is the primary concern
- Teams that need multi-cloud visibility and risk correlation
- Security programs willing to run separate tools for AppSec and cloud security, or that want to add cloud context to an existing AppSec tool
How Endor Labs compares: Endor Labs puts reachability findings in the IDE and pull request, where developers fix them, and gives teams deep AppSec coverage that a cloud security platform does not.
7. Snyk alternative for small teams: Aikido Security
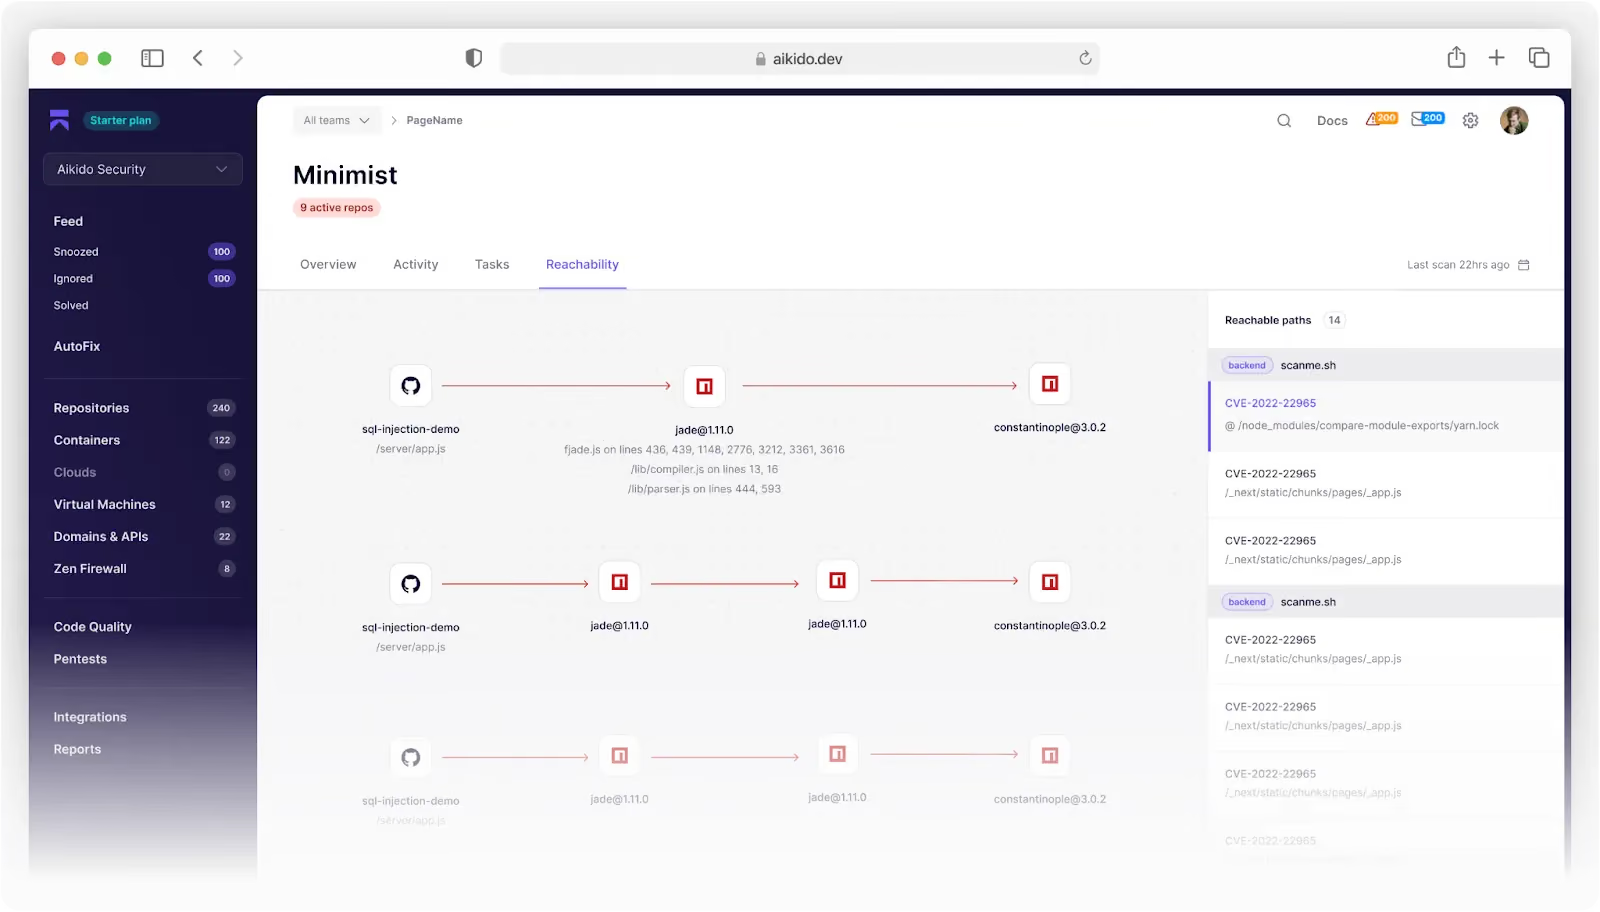
For small teams just starting out, Aikido Security wraps open source tools (Opengrep, Syft, Trivy) into a unified dashboard with a thoughtful UI. See our full list of Aikido alternatives.
What it includes
Aikido consolidates several open source scanners into one platform: SAST, SCA, container scanning, IaC analysis, and secrets detection, without managing each tool separately. The dashboard gives a single view of findings, and the UI is well designed.
For small teams early in their security journey, that consolidation matters. You aren't maintaining several tools, writing integrations, or building dashboards.
Limitations
As organizations grow, Aikido gets harder to run at scale. Because it wraps existing open source tools rather than building native capabilities, it's limited in how far it can push accuracy, performance, or deep reachability analysis. It also pushes you into feeds to review and lacks a granular policy engine to automate workflows at scale.
Enterprise needs such as fine-grained policies, custom workflows, and deep integrations with complex toolchains expose these limits. Teams that adopted Aikido for its simplicity often outgrow it as their security program matures.
Who should consider it
- Small engineering teams (under 25 developers)
- Organizations that prioritize ease of setup over depth of capabilities
How Endor Labs compares: Endor Labs builds its own program analysis instead of wrapping open source scanners, and its policy engine is designed for large organizations, so teams do not outgrow it.
8. Enterprise SAST Snyk alternative: Checkmarx
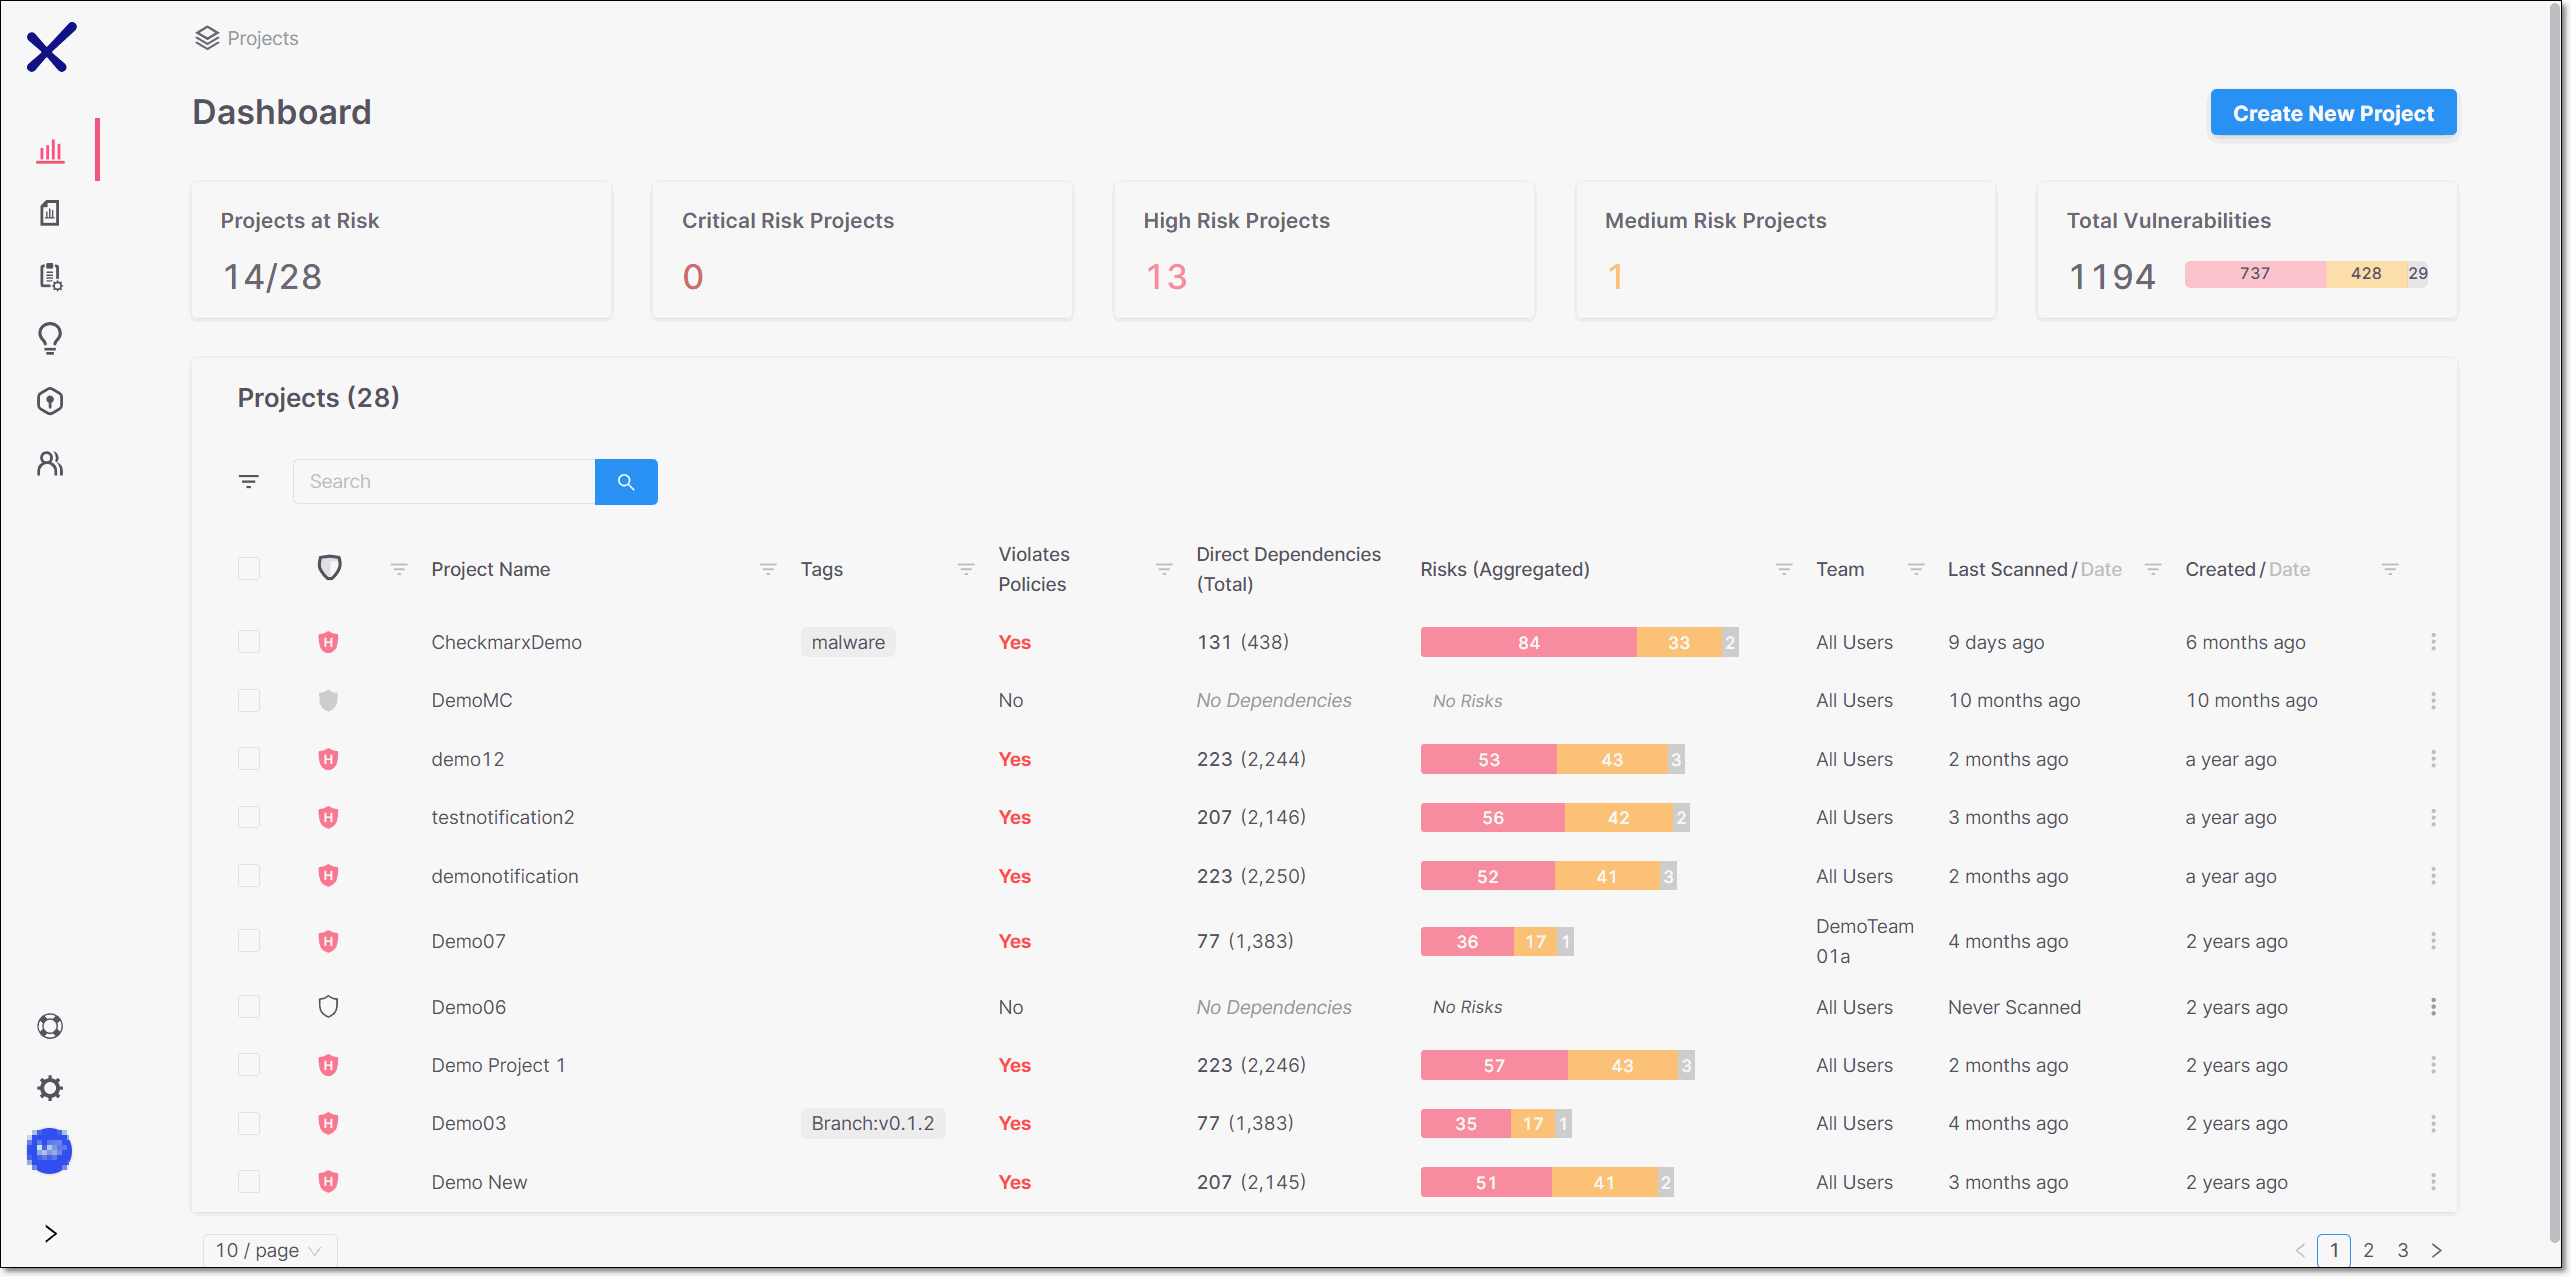
Checkmarx is an established enterprise application security platform with deep SAST capabilities. Checkmarx One combines static analysis, SCA, API security, and container scanning in one offering designed for large organizations. See our full list of Checkmarx alternatives.
What it includes
Mature SAST is Checkmarx's core strength, with extensive language and framework coverage and detailed vulnerability reports that meet enterprise audit requirements. Enterprise features include central policy management, compliance reporting, and governance controls, plus integrations with Jira, ServiceNow, and common CI/CD systems.
Limitations
The trade-offs are complexity and cost. Checkmarx has a steeper learning curve and higher implementation overhead than developer-focused alternatives, and its reachability analysis is limited to its SAST focus.
Who should consider it
- Large enterprises that want one platform for SAST, SCA, and API security
- Organizations in regulated industries that need extensive compliance reporting
- Teams with the resources to manage a feature-rich, complex tool
How Endor Labs compares: Endor Labs pairs AI SAST with function-level reachability for dependencies and containers, and it was built for developer workflows from the start, so security does not slow teams down.
9. Compliance-focused Snyk alternative: Veracode
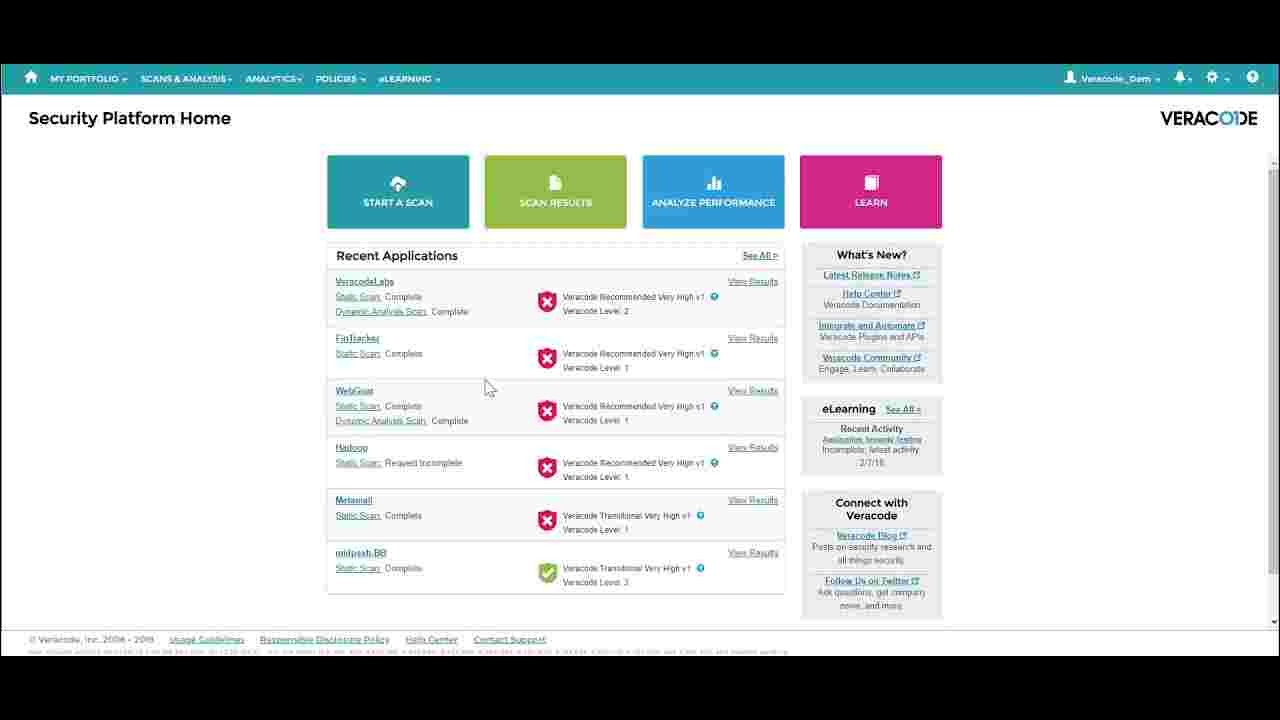
Veracode is an application security platform built around compliance and governance. It provides static analysis, dynamic analysis, and SCA, often bundled with manual penetration testing services. See our full list of Veracode alternatives.
What it includes
Veracode is strong at generating the reports and documentation required for audits like PCI DSS, HIPAA, and SOC 2, and its policy engine lets security teams define and enforce standards across the organization. Access to Veracode's security consultants for manual testing appeals to organizations that need high-confidence assessments.
Limitations
Veracode integrates less deeply with developer workflows than tools designed for continuous integration. Developers can experience it as a security gate rather than a tool that helps them ship.
Who should consider it
- Organizations in finance, healthcare, and government where compliance drives tool selection
- Teams that value expert services alongside automated scanning
How Endor Labs compares: Endor Labs delivers findings in pull requests and IDEs, and supports compliance programs such as SOC 2, PCI DSS, and FedRAMP without turning security into a gate.
10. License compliance Snyk alternative: Black Duck
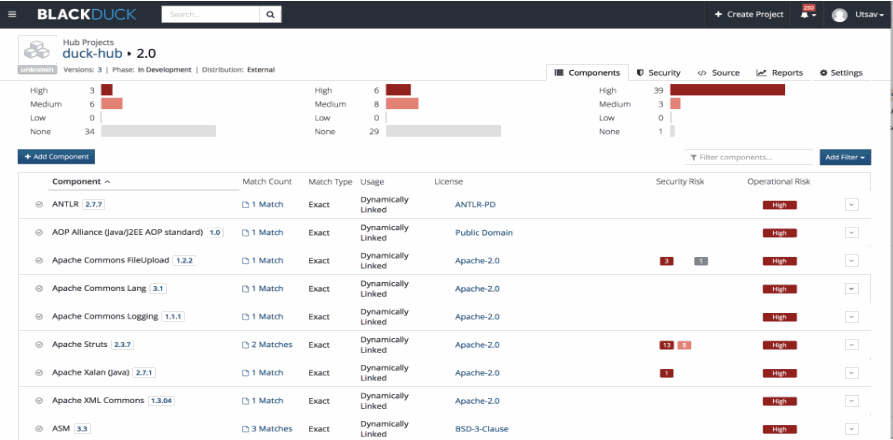
Black Duck specializes in open source governance and license compliance. It includes vulnerability scanning, but its main strength is identifying every open source component and managing the open source license obligations that come with it. See our full list of Black Duck alternatives.
What it includes
Black Duck maintains extensive license data and can identify conflicts or obligations that create legal risk. It generates SBOMs in standard formats like SPDX and CycloneDX, which more customers and regulators now ask for.
Limitations
Black Duck focuses on governance and reporting more than developer workflow integration, costs more, and doesn't offer reachability analysis.
Who should consider it
- Legal and security teams at large enterprises where open source license risk is a primary concern
- Organizations doing M&A due diligence
How Endor Labs compares: Endor Labs covers SBOMs and compliance and license risk, and adds function-level reachability, so license and vulnerability findings come from one platform.
Snyk alternatives comparison table
How to choose a Snyk alternative
Switching security tools is a significant decision. It affects developer workflows, creates migration overhead, and usually needs executive buy-in. These steps help you decide which alternative makes sense.
- Start with the problem you're solving. If alert fatigue and developer trust are your primary issues, you need a platform with reachability analysis and low false positives, which points to Endor Labs. If cost is the only constraint and you have security engineers to spare, open source tools like Trivy can cover the basics, at the price of the engineering time to run them.
- Evaluate your build environment. Teams using Bazel, monorepos, or older languages like C/C++ should confirm that alternatives support these environments in depth. Many tools check a box for "Bazel support" without the depth needed for accurate results. Endor Labs was built to handle Bazel monorepos and C/C++ codebases.
- Check detection accuracy and prioritization. Ask each vendor to show that a vulnerable function is actually called by your code. Package presence alone tells you very little. Look for contextual prioritization: a remote code execution flaw in a library used only for local configuration parsing is far lower risk than the same flaw in a web-facing API handler. Tools that analyze code execution paths generate far less noise than tools that only check package presence.
- Test developer workflow integration. Security tools succeed or fail on developer adoption. Check for:
- Native plugins for VS Code, JetBrains IDEs, or your team's preferred editors
- Support for your CI/CD platform (GitHub Actions, GitLab CI, Azure DevOps, Jenkins) and standard formats like SARIF
- Custom scan policies and thresholds
- Integration with your ticketing system
- Test remediation as well as detection. Look for remediation guidance with specific version recommendations. Ask whether the tool shows what an upgrade will break, and what happens when a library can't be upgraded. Endor Labs handles these cases with upgrade impact analysis and Endor Patches.
- Consider your AI strategy. If you're building AI-native applications or using AI coding agents extensively, AI model discovery, AI-BOM generation, and AI security code review are core requirements. Confirm they are available in production today, and ask whether the tool works where agents write code. Endor Labs ships all of these, along with AURI by Endor Labs for coding agent workflows.
- Run a two-week proof of value. Scope it against your own repositories rather than vendor benchmark repositories. Run two or three candidates on the same repositories as your current Snyk deployment and compare four numbers: total findings, the share confirmed reachable or exploitable, time from finding to merged fix, and pull requests blocked by security checks.
- Talk to references. Ask vendors for customers who switched from Snyk and can speak to the migration. What was harder than expected? What got easier? How long did it take developers to adjust?
How to migrate from Snyk
Migrating from Snyk needs careful planning so you don't disrupt development or miss critical vulnerabilities during the transition.
- Run tools in parallel. Start with a proof of concept on repositories that represent your typical codebase complexity, and confirm the new tool catches the same real vulnerabilities while reducing noise.
- Compare findings systematically. Run both tools against the same repositories and analyze the differences: false positive rates, remediation guidance quality, and how each handles your stack and build environment.
- Roll out gradually. Start with less critical repositories or a single team, refine the configuration, then expand. This also helps with change management and developer training.
- Rebuild what Snyk handled. Most migrations need these recreated in the new platform:
- CI/CD integrations and build-breaking thresholds
- Severity policies, exceptions, and ignore rules, including .snyk policy files
- Ticketing and pull request workflows
- SBOM and compliance exports
- Developer documentation and training on what changed
Conclusion
Most teams leave Snyk because of alert noise, coverage gaps in complex builds, or cost that climbs with headcount. Point tools and open source scanners each solve one piece of that, and leave your team to stitch the rest together.
Endor Labs solves the whole problem in one platform. Function-level reachability across code, dependencies, and containers confirms which findings are reachable, cutting SCA alerts by 92% on average. AURI by Endor Labs then delivers evidence-based remediation, safe upgrade paths, and patches when an upgrade isn't possible, and works where coding agents write code. For feature-level detail, see the Endor Labs vs Snyk comparison and our breakdown of SCA, SAST, and container scanning compared. Schedule a demo to see Endor Labs run against your own repositories.
FAQs about Snyk alternatives
What is the best alternative to Snyk?
For engineering teams leaving Snyk because of false positives and developer friction, Endor Labs is the strongest alternative. It provides AI-native analysis and full-stack reachability across code, open source dependencies, and container images, and cuts SCA alerts by 92% on average.
Who are Snyk's main competitors?
Snyk's main competitors include Endor Labs, which leads on reachability and noise reduction, along with GitHub Advanced Security, Semgrep, Checkmarx, Veracode, Black Duck, Wiz Code, Upwind, and Aikido Security, plus open source tools like Opengrep, Syft, and Trivy. Most of them cover a narrower slice of what Snyk does, or require more manual work to reach the same coverage.
Why do companies switch from Snyk?
Companies typically switch from Snyk because of alert fatigue from high false positive rates, reachability analysis that covers only some languages, inconsistent results between CLI and SCM integrations, gaps in complex build systems, per-developer costs at scale, and gaps between AI marketing and production capabilities. In one customer deployment, Endor Labs cut monthly security tickets from 2,600 findings to 146 actionable issues.
Why does Snyk get expensive as teams grow?
Snyk prices per contributing developer. Its Team plan starts at $25 per developer per month, its Ignite plan starts at $1,260 per developer per year for organizations with fewer than 50 developers, and Enterprise pricing is custom. Because cost scales with headcount, large engineering organizations often end up weighing coverage against budget.
Is Endor Labs better than Snyk?
Endor Labs is designed to address Snyk's core limitations. It provides function-level reachability analysis across the entire application graph (including transitive dependencies), AI-native SAST with 95% false positive reduction, and production-ready AI governance. Companies like Atlassian, Cursor, Dropbox, and OpenAI choose Endor Labs to reduce noise and rebuild developer trust. See the full Endor Labs vs Snyk comparison.
What are the limitations of Snyk?
Snyk's main limitations include high false positive rates without enough exploitability context, reachability analysis limited to a subset of languages, inconsistent scanning results between integration methods, limited support for complex build systems like Bazel, and per-developer pricing that climbs with headcount.
Is Snyk a SAST or SCA tool?
Both. Snyk provides software composition analysis (SCA) for open source dependencies and static application security testing (SAST) through Snyk Code. It's historically better known for its SCA features and developer-friendly approach to dependency management.
Are there free or open source alternatives to Snyk?
Yes. Trivy, Syft, and Opengrep provide vulnerability scanning, SBOM generation, and SAST at no cost, and GitHub offers free code scanning for public repositories. A single free scanner rarely replaces Snyk end to end, though. You give up centralized reporting, automated remediation, reachability analysis, and policy management, and you take on the engineering time to run and tune the tools. Endor Labs also offers free developer tools for teams that want to start without a contract.
Can Snyk alternatives run on-premises or air-gapped?
Some can. Enterprise-focused tools such as Checkmarx and Black Duck offer self-hosted deployment for organizations with strict data residency requirements, and GitHub Advanced Security runs on GitHub Enterprise Server for self-hosted GitHub environments. Many cloud-native tools are SaaS only, so confirm deployment options during your evaluation.
What's next?
When you're ready to take the next step in securing your software supply chain, here are 3 ways Endor Labs can help: